smayank
Staff
Staff
February 25, 2025

Technical Tip: Significance of auth timeout and login session timeout when FortiAuthenticator acting as a IDP

  • February 25, 2025
  • 0 replies
  • 1696 views
Description

This article describes the significance of auth timeout and login session timeout when FortiAuthenticator is acting as an IDP

Scope FortiGate, FortiAuthenticator.
Solution

When configuring FortiAuthenticator as an IDP two timers should be taken into consideration.

  1. FortiGate auth timeout.
  2. Login session timeout.


The timer configured on FortiGate is as below

config user group
    edit <group name>
        set authtimeout <value>
end


Once gstatic packet comes to FortiGate, it redirects it to IDP, but before redirecting, it checks the firewall auth list, if user-IP mapping is present it evaluates the configured group-based policy.

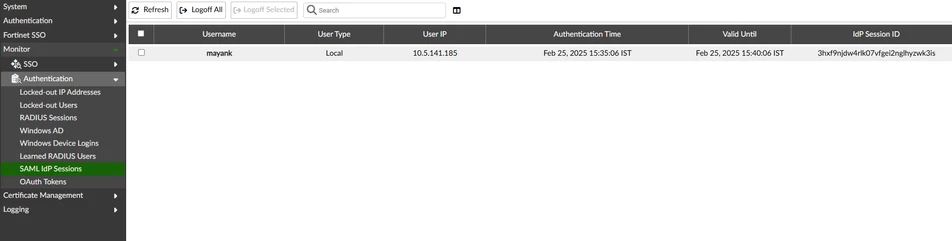
If user-ip mapping is not present it redirects to IDP. IDP keeps track of the IDP session ID if it is already present on Fortiauthenticator it will not trigger the authentication page and directly send an IDP response.

By default login session timeout on the FortiAuthenticator found under SAML Idp -> General settings page is 480 minutes and can be modified with a minimum value of 5 minutes.


If auth time out is set to 5 minutes on FortiGate this can be considered as a redirection time if there is no traffic for 5 minutes it will remove the entry from FortiGate and redirect if a new packet comes

IDP receives the request and checks the SAML IDP session if it is valid, the authentication page will not be triggered.


Verify the SAMA session under Authentication -> SAML IDP session.

image (4).png

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!