



Technical Tip: Setting user maximum number of failed login attempts and Lockout period for authentication
Description
This article describes how to set a maximum number of use attempts for firewall authentication before user lockout is triggered, and explains how to set a Lockout period for user authentication.
Scope
FortiGate.
Solution
When a user tries to log in for a captive portal, it is possible to set the maximum attempts for the user authentication and lock the user account for a particular time.
config user setting
set auth-lockout-threshold x <----- Max number of failed login attempts (range[1-10]).
set auth-lockout-duration yy <----- Lockout period in seconds (range[0-4294967295]).
end
For example:
FortiGate is configured with user 'test' and enabled with security-mode captive-portal.
config user group
edit "test_grp"
set member "test"
next
end
config system interface
edit "mgmt"
set security-mode captive-portal
set security-exempt-list "mgmt-exempt-list"
set security-groups "test_grp"
set device-identification enable
set role lan
set snmp-index 2
next
end
Maximum authentication attempts is set to 2 and 'auth-lockout-duration' as 100 seconds.
config user setting
set auth-lockout-threshold 2
set auth-lockout-duration 100
end
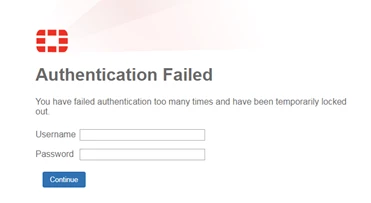
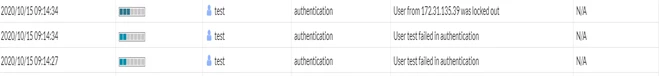
When a user enters wrong credentials for two attempts, the account will be locked for 100 seconds. On the third attempt, the user will see the following message.
By default, the number password retry attempts is set to three, allowing the administrator a maximum of three attempts at logging in to their account before they are locked out for a set amount of time (by default, 60 seconds). Upon setting the 'auth-lockout-duration' to 0, the user will be locked out for the default time period (60 seconds).
For more information, see Password retries and lockout time - FortiGate 6.2.16 cookbook.

