| Solution | Network Diagram. 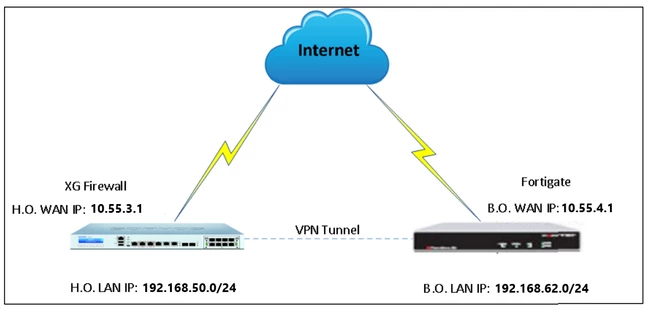
Configuration: FortiGate. Create IPsec phases and tunnels. - Go to VPN -> IPsec tunnels and select Create New.
- Under VPN Setup, enter a Name.
- Set the Template Type to Custom.
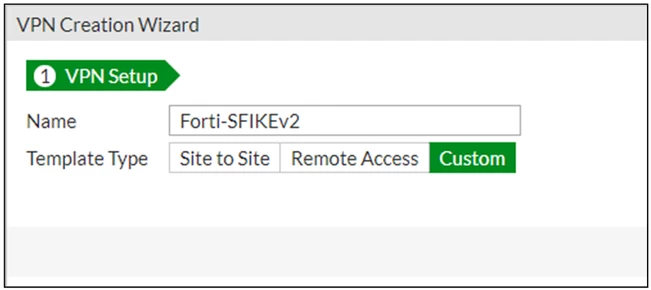
- Select Next.
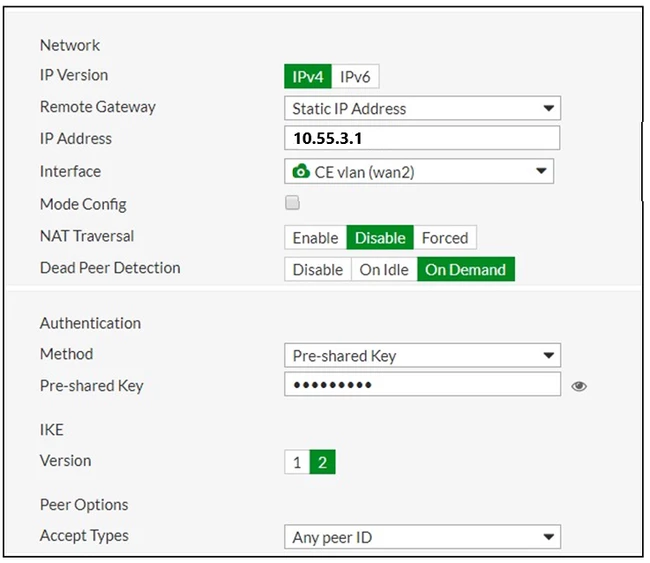
- Under Network, set IP Version to IPv4.
- Set Remote Gateway to Static IP Address.
- For IP Address, enter the WAN IP address of the Sophos Firewall (for example: 10.55.3.1).
- Set NAT Transversal to Disable (it can be enabled, but it must be the same on the other side.) and Dead Peer Detection to On Demand.
- Under Authentication, set Method to Pre-shared Key.
- Enter the Pre-shared Key.
- In IKE, set Version to 2.
- Under Peer Options, set Accept Types to Any peer ID.
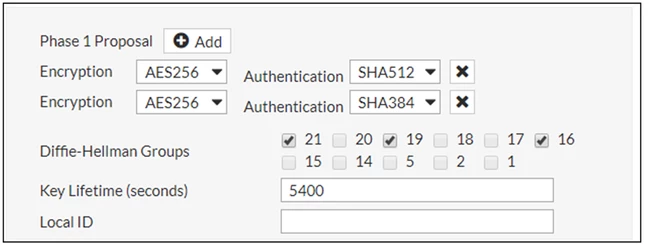
Configure Phase 1 Parameters. - Set Encryption to AES256 and Authentication to SHA512.
- Select Add and set Encryption to AES256 and Authentication to SHA384.
- For Diffie-Helman Groups, select 16, 19, and 21.
- For Key Lifetime, enter 5400 seconds.
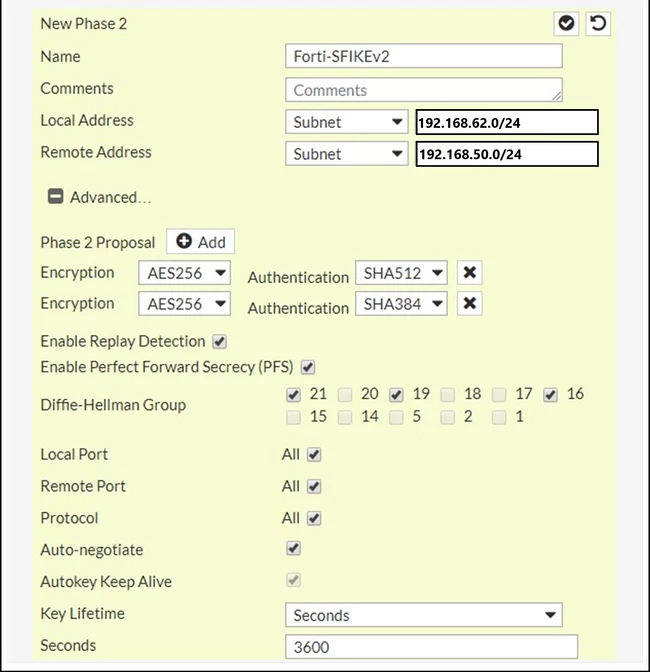
Configure Phase 2 Parameters: - Under Phase 2 Selectors, enter a Name.
- Set the Local Address to Subnet and enter the LAN IP address of the FortiGate appliance (for example 192.168.50.0/24).
- Set the Remote Address to Subnet and enter the LAN IP address of the XG Firewall (for example 192.168.62.0/24).
- Expand the Advanced section.
- Under Phase 2 Proposal, set Encryption to AES256 and Authentication to SHA512.
- Select Add and set Encryption to AES256 and Authentication to SHA384.
- Select Enable Replay Detection and Enable Perfect Forward Secrecy (PFS).
- For the Diffie-Hellman Group, select 16, 19, and 21.
- For Local Port, Remote Port, and Protocol, select All.
- Select Auto-negotiate.
- Set Key Lifetime to Seconds and enter 3600 in Seconds.
Select OK. Create a Static Route for the VPN Tunnel. Go to Network -> Static Routes and select Create New. 
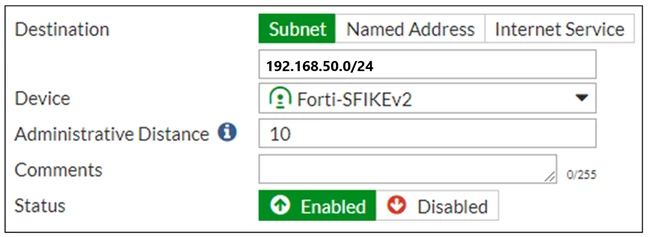
- For Destination, select Subnet and enter the LAN IP address of the XG Firewall (for example 192.168.50.0/24).
- Set the Device to the IPsec tunnel created previously (for example Forti-SFIKEv2.).
- For Administrative Distance, enter 10.
- Set Status to Enabled.
Select OK. Create Firewall Rules. - Go to Policy & Objects -> IPv4 Policy and select Create New.
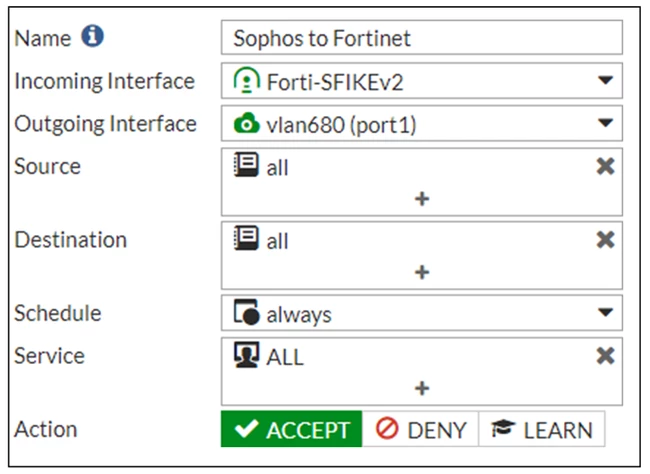
- Enter a Name.
- Set the Incoming Interface to the LAN interface of the FortiGate appliance (example: Forti-SFIKEv2).
- Set the Outgoing Interface to the IPsec tunnel created (example: vlan680 (port1)).
- For Source, Destination, and Service, select all.
- Set the Schedule to always.
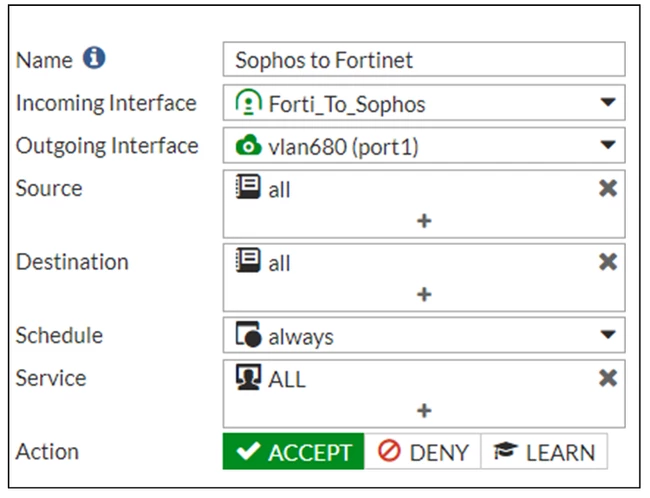
- Similarly, create another firewall policy for traffic from the XG Firewall to the FortiGate appliance.
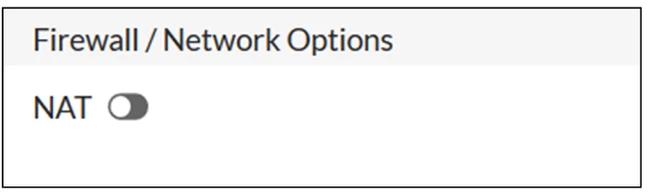
Note: Turn off NAT if NAT-T will not be used in the VPN Profile. Select OK.
Sophos XG Firewall. Create an IPsec Connection. - Go to Configure -> VPN -> IPsec Connections and select Add.
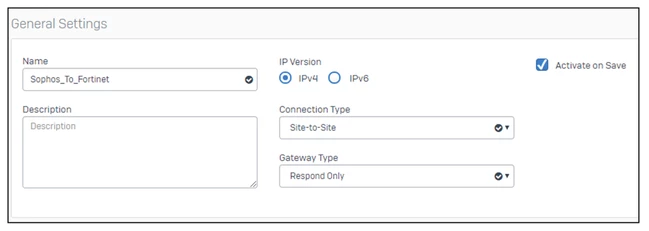
- Under General Settings, enter a Name.
- Set IP Version to IPv4, Connection Type to Site-to-Site, and Gateway Type to Respond Only.
- Select Activate on Save.
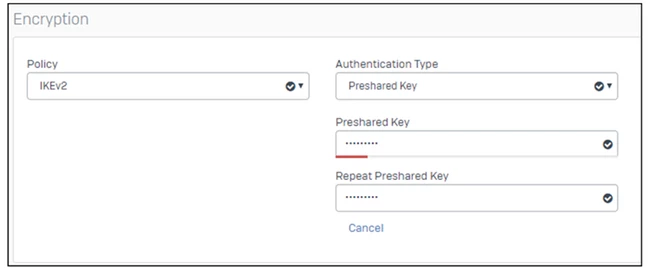
- Under Encryption, set Policy to IKEv2.
- Set the Authentication Type to Preshared Key, enter the Preshared Key, and Repeat Preshared Key.
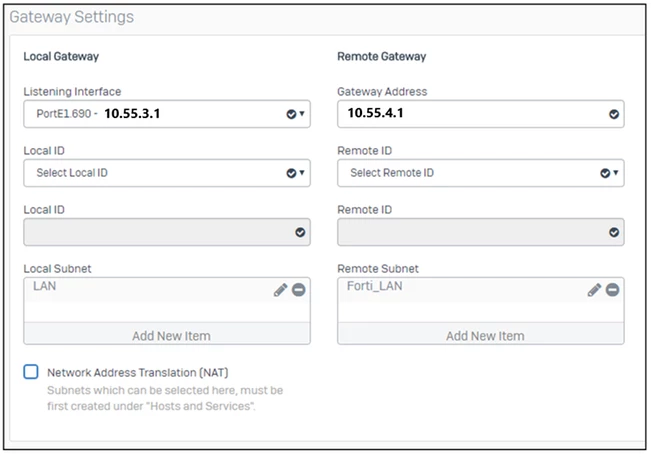
- Under Gateway Settings -> Local Gateway set Listening Interface to the WAN IP address of XG Firewall (for example: PortE1.690 - 10.55.3.1), and set Local Subnet to LAN.
- Under Gateway Settings -> Remote Gateway set Gateway Address to the WAN IP address of FortiGate appliance (for example: 10.55.4.1), and set Remote Subnet to Forti_LAN.
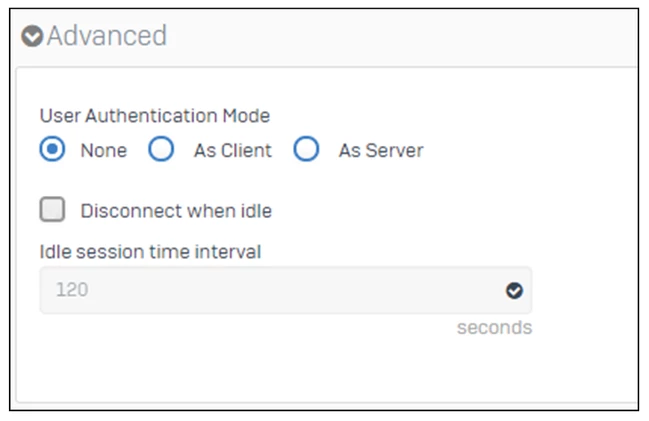
- Under Advanced, set User Authentication Mode to None.
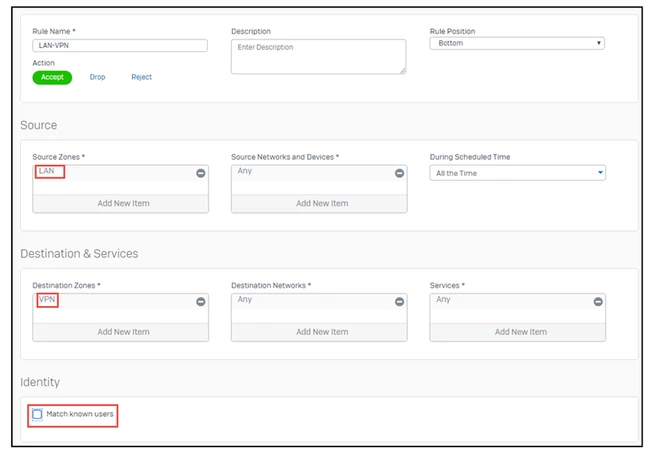
Create a Firewall Rule. - Go to Protect -> Firewall and select Add Firewall Rule.
- Enter a Rule Name.
- For Sources Zones, select LAN. For Destination Zones, select VPN.
- Under Identity, clear the Match known users check box.
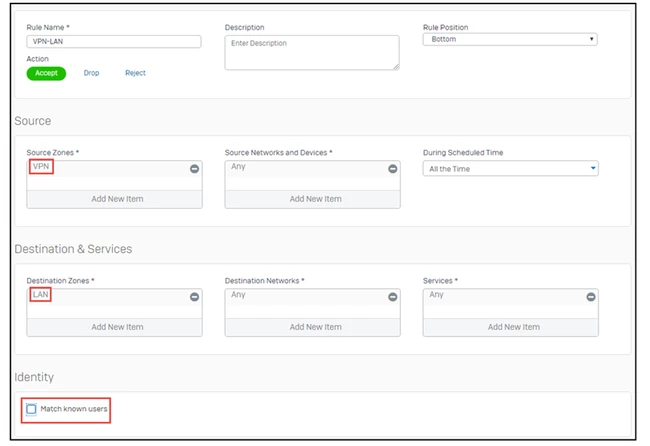
- Similarly, create a firewall rule for VPN to LAN traffic.
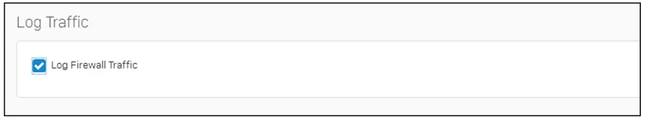
- Select Log Firewall Traffic.
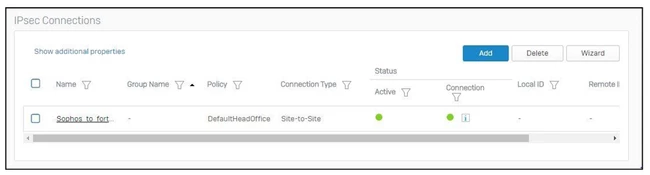
Select Save. Enable IPsec Connection. - Go to Configure -> VPN -> IPsec Connections.
- Under Status, select Active and Connection to activate the connection.
Verify VPN status on FortiGate. Go to Monitor -> IPsec Monitor. 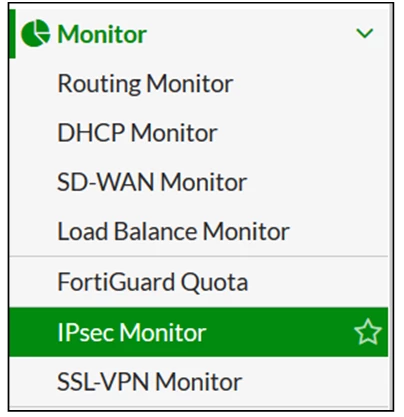
Tunnel details are displayed. If the status is Down, select the tunnel and select Bring Up to initiate the tunnel. 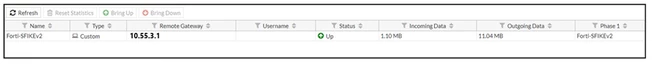
Related articles: Technical Tip: How to setup IPSEC VPN between FortiGate and Sophos when FortiGate is behind NAT
Technical Tip: How to configure a Site-to-Site IPsec tunnel between FortiGate and Sonicwall from GUI
Technical Tip: How to configure IKE version 1 or 2 in IPsec VPN FortiGate |





