Technical Tip: Set the FortiGate unit to bring up IPSec VPN tunnels automatically (Enable Auto-negotitation)
Description
By default, FortiGate will only negotiate and try to bring up Phase2 tunnel when 'interesting' traffic is matched to an IPSec policy.
In situations where an IPSec tunnel is needed to be up already before traffic passes through a policy, auto-negotiation must be enabled under phase2 settings of IPsec VPN tunnel.
Therefore, FortiGate will negotiate and try to bring up Phase2 tunnel automatically.
Scope
Solution
By default, FortiGate will only negotiate and try to bring up Phase2 tunnel when 'interesting' traffic is matched to an IPSec policy.
In situations where an IPSec tunnel is needed to be up already before traffic passes through a policy, auto-negotiation must be enabled under phase2 settings of IPsec VPN tunnel.
Therefore, FortiGate will negotiate and try to bring up Phase2 tunnel automatically.
Scope
FortiOS firmware version 4.00 MR3
FortiOS firmware version 5.0.x
Solution
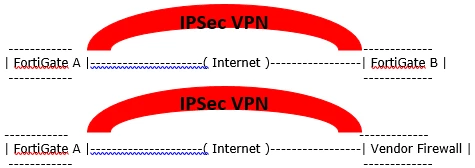
This is applicable for any site-to-site IPSec VPN between two FortiGates or another vendor.
Assuming an IPSec VPN connection to 'FortiGate B' or 'Vendor Firewall' has already been configured from 'FortiGate A'.If for any reason, the remote FortiGate/firewall unit is rebooted, an administrator may wish to have this IPSec tunnel come back up automatically, meaning before any traffic is initiated.
For this to happen, a CLI Phase 2 setting must be enabled in configuration of all those tunnels, which should automatically recover when necessary and be brought up immediately.
From CLI.
For route based IPSec:# config vpn ipsec phase2-interfaceFor policy based IPSec:
edit <name>
set auto-negotiate enable
end# config vpn ipsec phase2It is also possible to enable from GUI:
edit <name>
set auto-negotiate enable
end
GUI – VPN – IPsec Tunnels – VPN tunnel name – Phase2 selectors – Advanced – Auto-negotiate.
Related Articles
Technical Tip: How to configure VPN Site to Site between FortiGates (Using VPN Setup Wizard)