Technical Tip: Scheduled SSL VPN/Dial-up connectivity via Local-in-Policy
Description
The article describes how to use the schedule to restrict access of SSL-VPN/Dial-up IPsec VPN using Local-in-Policy.
With the default configuration, SSL VPNs/Dialup IPsec VPNs are always accessible to all public addresses on Internet.
Scope
FortiGate.
Solution
In this example, SSL VPN/Dial-up VPN will only be accessible from Monday to Friday from 09:00 AM to 06:00 PM every day and will be blocked during off-business hours.
- Configure two recurring schedules
One will be for weekdays, and another will be for weekends.
config firewall schedule recurring
edit "DENY-OFF-BH-MON-FRI"
set start 18:01
set end 08:59
set day Monday Tuesday Wednesday Thursday Friday
next
edit "DENY-OFF-BH-SAT-SUN"
set day Sunday Saturday
next
end
config firewall schedule group
edit "Schedule"
set member "DENY-OFF-BH-MON-FRI" "DENY-OFF-BH-SAT-SUN"
next
end
- Configure firewall address object for SSL VPN server IP/Dialup IPsec listening IP (i.e., Public IP configured on Firewall):
config firewall address
edit "PUBLIC-IP"
set allow-routing enable
set subnet x.x.x.x 255.255.255.255
next
end
-
Configure service for SSL VPN port and Dial-up VPN ports:
config firewall service custom
edit "SSLVPN"
set category "Network Services"
set tcp-portrange 10443
next
end
Service for Dial-Up VPN Ports exists in the 'Services (Under Policy and Object)'.
config firewall service custom
edit "IKE"
set category "Tunneling"
set udp-portrange 500 4500
next
end
-
Configure the SSL VPN following this document:
Configure the Dial-UP VPN following this article:
Technical Tip: How to configure a FortiGate as IPsec VPN Dial-Up client when FortiGate is not behind a NAT unit
-
Configure the firewall local-in-policy.
Note:
It is possible to have a GUI visibility of this feature when it is enabled under System -> Feature Visibility -> Additional Features -> Local In Policy.
While local-in policies can only be configured via the CLI in earlier versions, starting from v7.6.0, they can be configured directly through the GUI.
If there are other site to site VPN tunnel configured with the same 'PUBLIC-IP', make sure to create an address object for those trusted remote vpn peers' IPs and add them to the address group.
Create a local-in-policy with source as those trusted remote vpn peer IPs address group and set action as allow.
config firewall local-in-policy
edit 1
set intf "port1"
set srcaddr "Trustedvpnpeerip’s"
set dstaddr "PUBLIC-IP"
set service "IKE"
set schedule "always"
set action accept
next
end
CLI:
config firewall local-in-policy
edit 1
set intf "port2"
set srcaddr "all"
set dstaddr "PUBLIC-IP"
set service "SSLVPN"
set schedule " Schedule "
next
edit 2
set intf " port2"
set srcaddr "all"
set dstaddr "PUBLIC-IP"
set service "IKE"
set schedule "Schedule"
next
end
GUI:
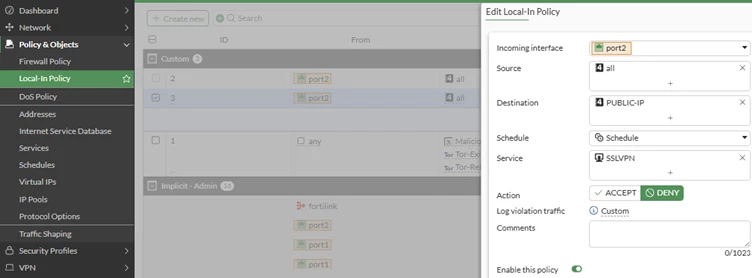
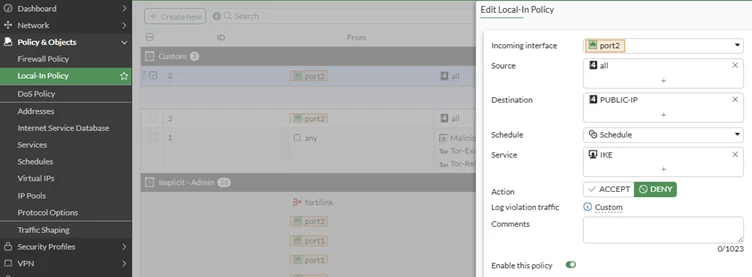
Result:
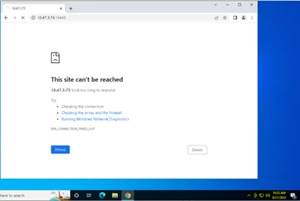
SSL VPN service will not be available during off-business hours.