Technical Tip: SAML for SSL VPN Tunnel mode (FortiClient) with FortiAuthenticator IDP
Description
This article describes how to setup both FortiAuthenticator (IDP) and FortiGate (SP) for SAML SSO SSL VPN.
Scope
FortiClient, FortiGate.
Solution
In the below example, FortiAuthenticator is configured as a IDP which authenticates the user login and FortiGate as a SP.
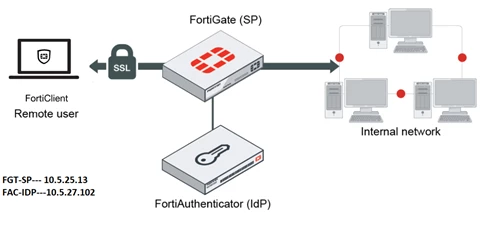
To configure FortiAuthenticator as the IDP.
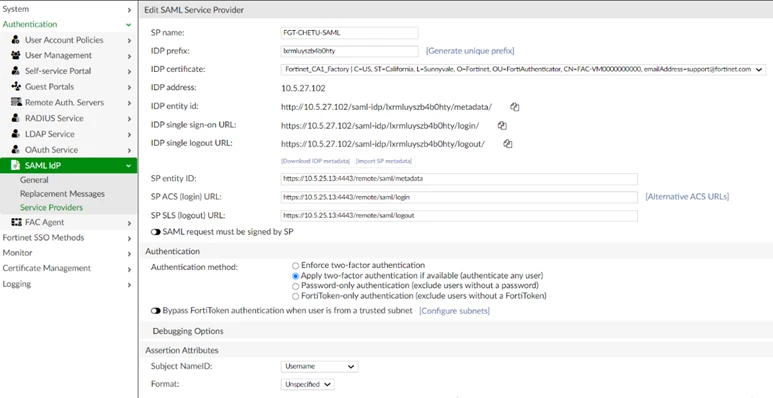
1) In FortiAuthenticator, go to Authentication -> SAML IdP -> Service Providers.
2) Select 'Create New'.
3) Configure as desired, then select 'OK'.
2) Select 'Create New'.
3) Configure as desired, then select 'OK'.
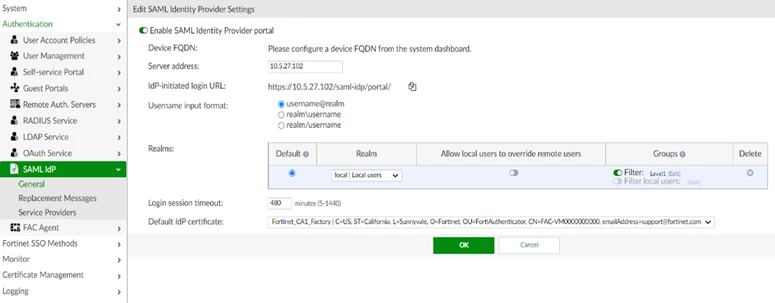
4) To add a local user, go to Authentication -> User Management -> Local User, then select 'Create New'. Configure the local user as desired.
5) To add a local user, go to SAML IdP -> General .
5) To add a local user, go to SAML IdP -> General .
To configure FortiGate as the SP.
1) Upload the FAC certificate as a 'remote certificate' on FortiGate.
2) Setup SAML as below:
4) Configure the SSL VPN and add the group to respective SSL portal.
1) Upload the FAC certificate as a 'remote certificate' on FortiGate.
2) Setup SAML as below:
FGT-Chetu (facsmal) # show3) Configure the Group and add as a member.
# config user saml
edit "facsmal"
set cert "Fortinet_Factory"
set entity-id "https://10.5.25.13:4443/remote/saml/metadata"
set single-sign-on-url "https://10.5.25.13:4443/remote/saml/login"
set single-logout-url "https://10.5.25.13:4443/remote/saml/logout"
set idp-entity-id "http://10.5.27.102/saml-idp/lxrmluyszb4b0hty/metadata/"
set idp-single-sign-on-url "https://10.5.27.102/saml-idp/lxrmluyszb4b0hty/login/"
set idp-single-logout-url "https://10.5.27.102/saml-idp/lxrmluyszb4b0hty/logout/"
set idp-cert "REMOTE_Cert_2"
set user-name "Username"
set group-name "Groups"
set digest-method sha1
next
end
4) Configure the SSL VPN and add the group to respective SSL portal.
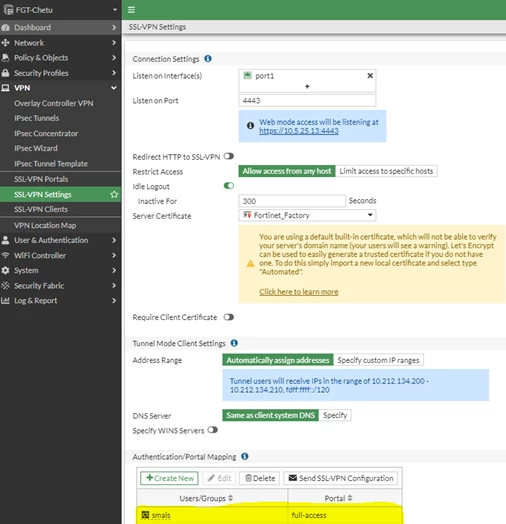
5) Set up a policy on the FortiGate from the SSL tunnel interface (ssl.root for example) to whatever destination users should be able to access via the SSLVPN tunnel. Add the above created group as source.
Important:
- If no SSLVPN policy is configured, SSLVPN will not work at all. FortiGate will provide a warning on the SSL VPN Settings page if no policy is created.
- If the SAML user group is not included in an SSLVPN policy, FortiGate will not be able to redirect login attempts to the SAML IdP. Only groups/users that are referenced in SSLVPN policies are considered for SSLVPN authentication.
- If there is no other group in authentication portal then SAML group, then authentication window will not appear and the user will be automatically redirected to the SAML provider page
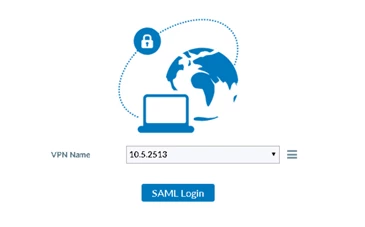
6) Now, connect the FortiClient and select 'Enable SSO for VPN tunnel' option and save.
Once saved, it will be possible to see SAML login icon.
Select and login.
Once saved, it will be possible to see SAML login icon.
Select and login.
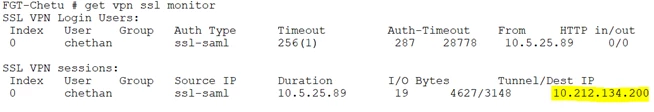
Verification