Shashwati
Staff
Staff
August 30, 2023

Technical Tip: Route-based IPsec site to site redundant VPN failover using BGP

  • August 30, 2023
  • 0 replies
  • 7554 views
Description This article discusses Route-based IPsec site-to-site redundant VPN failover using BGP.
Scope

 FortiGate v6.X and v7.X

Solution
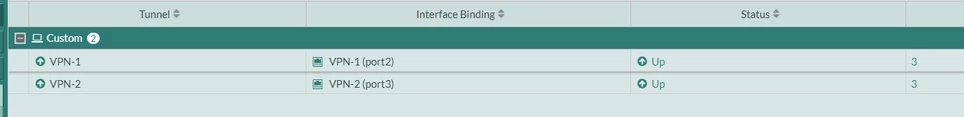
  • Configure IPSec Site to Site VPN redundant tunnel for both sites:


1329.PNG


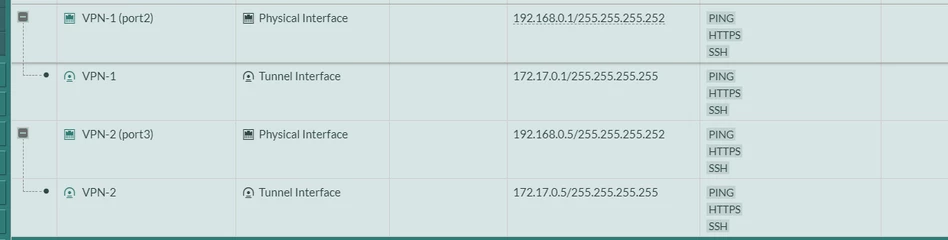
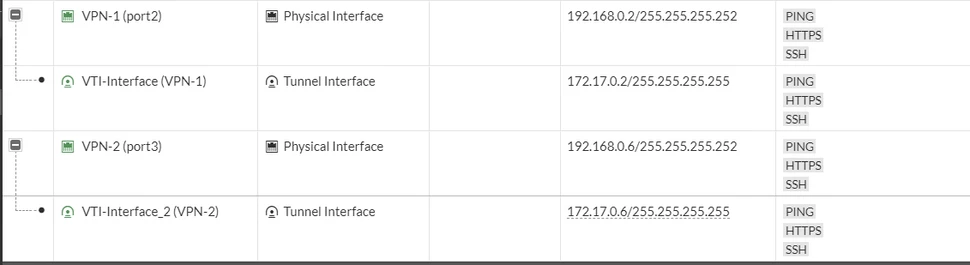
  • Assign Tunnel Interface IP for both Sites Tunnel.


Site-1:


329.PNG


Site-2:


429.PNG


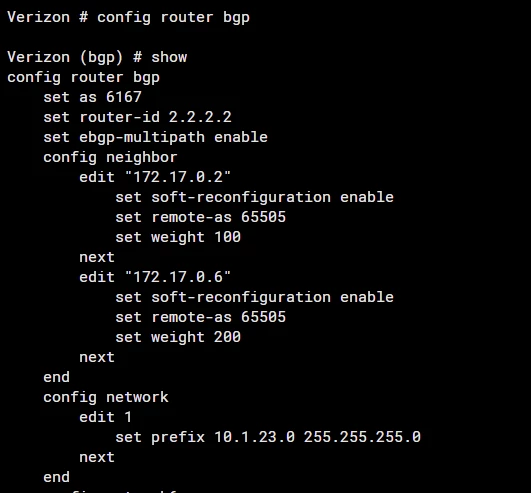
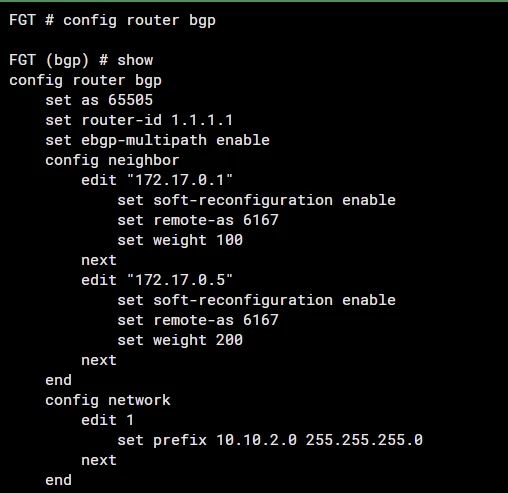
  • Configure BGP on both Sites.
  • Set weight for neighbors as required. 

Site-1:


529.PNG


Site-2:


629.PNG


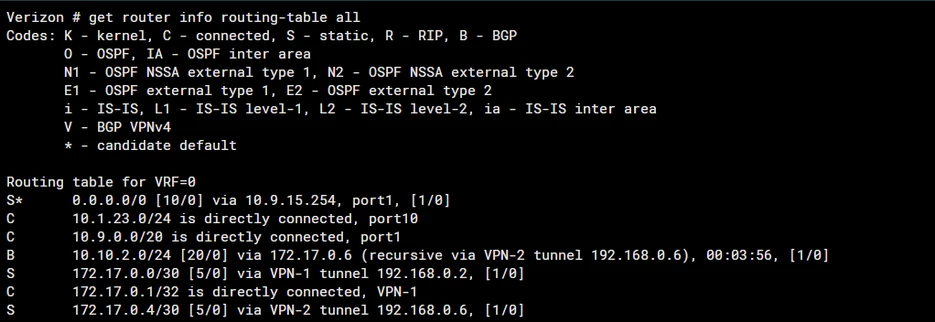
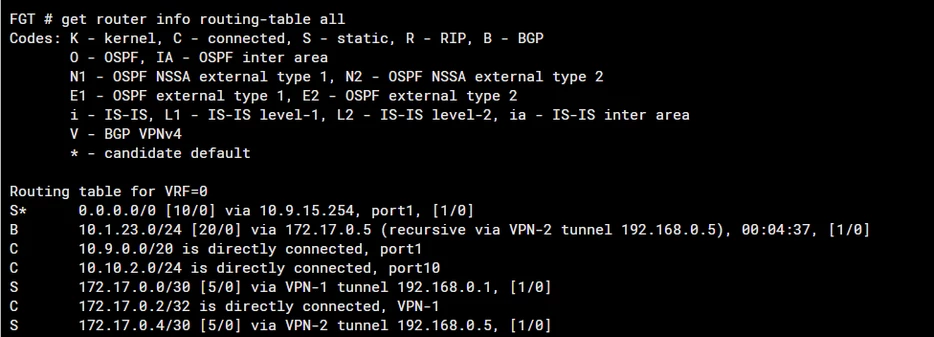
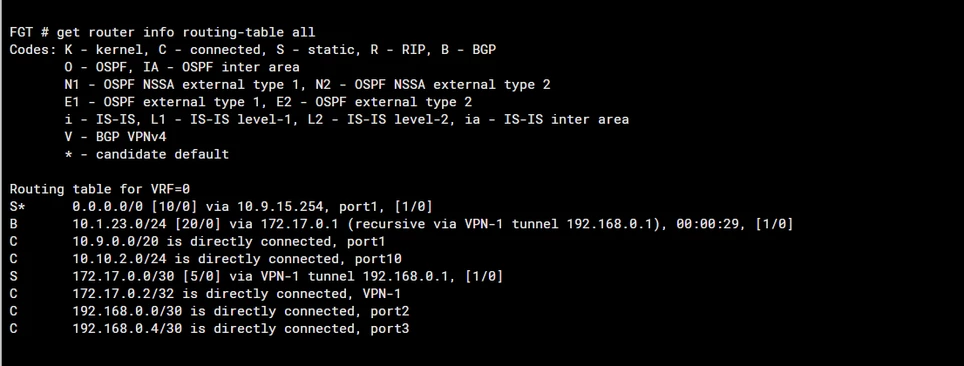
  • Check the routing table. VPN Tunnel with higher weight BGP neighbor will get priority.


Site-1:

  • VPN-2 is active in the routing table as the neighbor weight is higher:


729.PNG


Site-2:


829.PNG


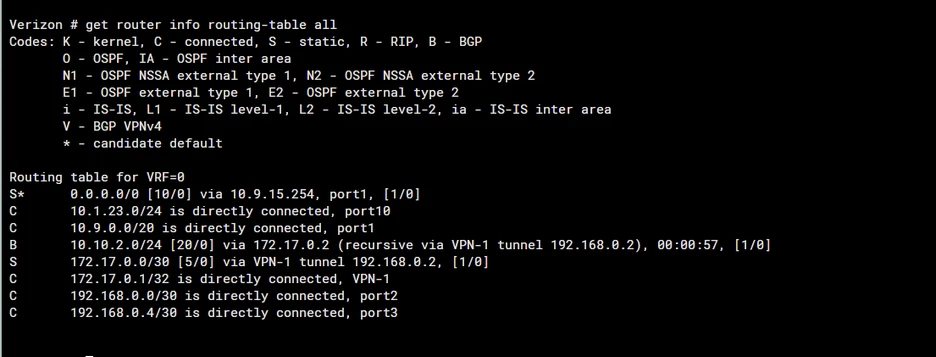
  • When Tunnel VPN-2 goes down traffic will be forwarded using Tunnel VPN-1.


Site-1:


Capture1.PNG


Site-2:


Capture2.PNG


Related article:

https://community.fortinet.com/t5/FortiGate/Technical-Tip-How-to-fix-the-random-load-balancing-traffic-issue/ta-p/259496

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!