apFortinet
Staff
Staff
August 24, 2024

Technical Tip: Restricting Source port of the traffic for specific service

  • August 24, 2024
  • 0 replies
  • 2112 views
Description

This article describes how to restrict traffic using a firewall policy when there is a need to allow traffic from only a specific source port or source port range for a specific service.

Scope FortiGate.
Solution

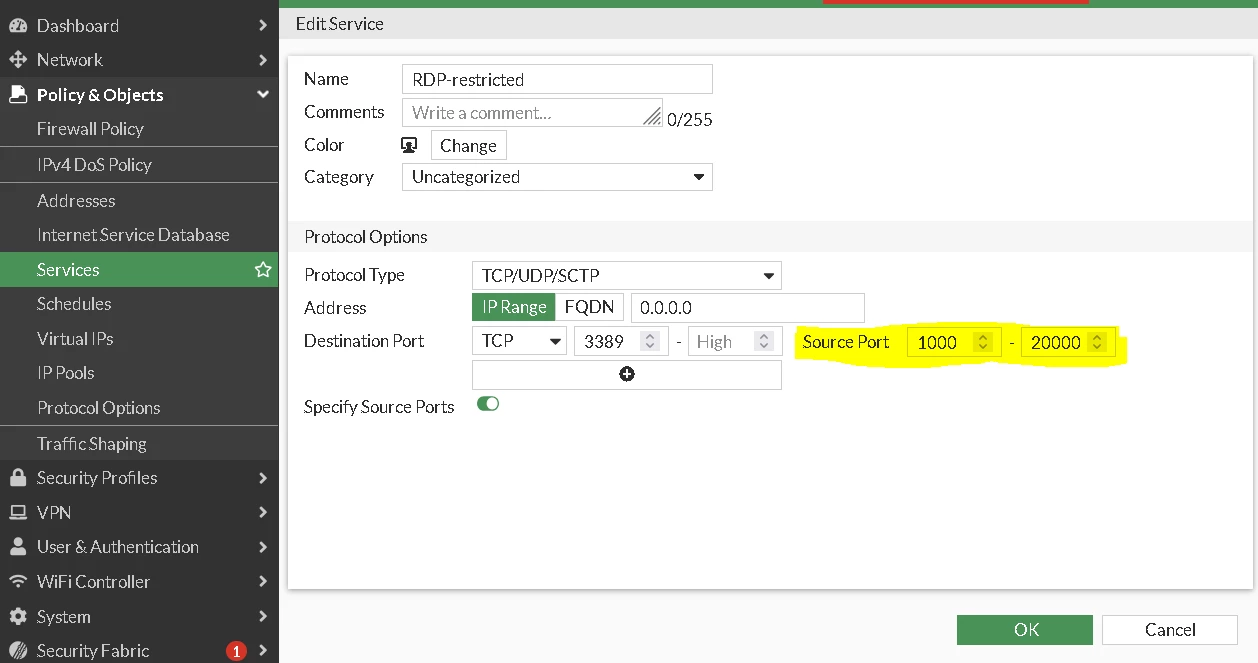
This article has restricted RDP communication to specific source port ranges 1000 to 20000 for example.

  • It is necessary to restrict the source port/source port range within the existing service/by creating a new custom service. It is recommended to create a new custom service instead of changing source port information within the default available services
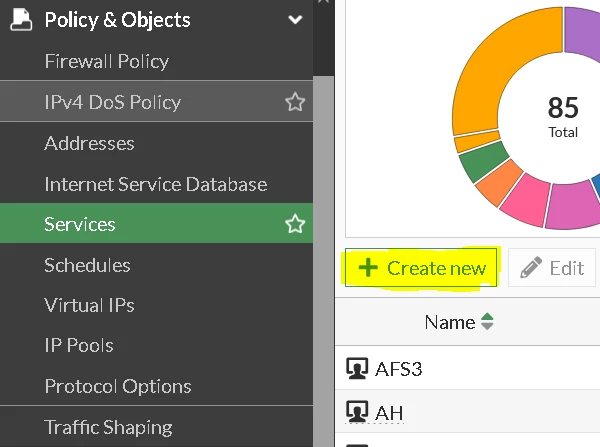
  • It has been created an 'RDP-restricted' custom service by following Policy & Objects -> Services -> Create New:


pic7.PNG


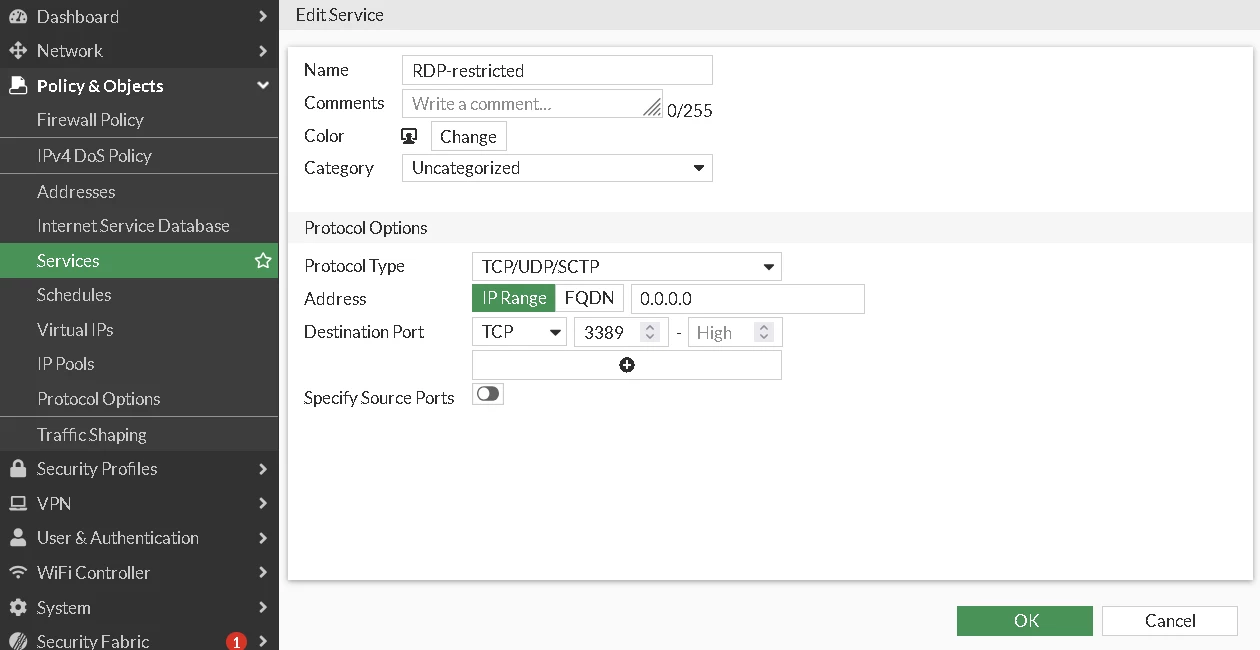
  • Select the Protocol Type and Specify the destination port as required. It has been specified TCP protocol and destination port 3389 for RDP. It is possible to specify this same port number in the Low and High boxes if it is a single port. If it is a range of ports, it is possible to specify lower and upper numbers of range accordingly.
     

pic1.PNG


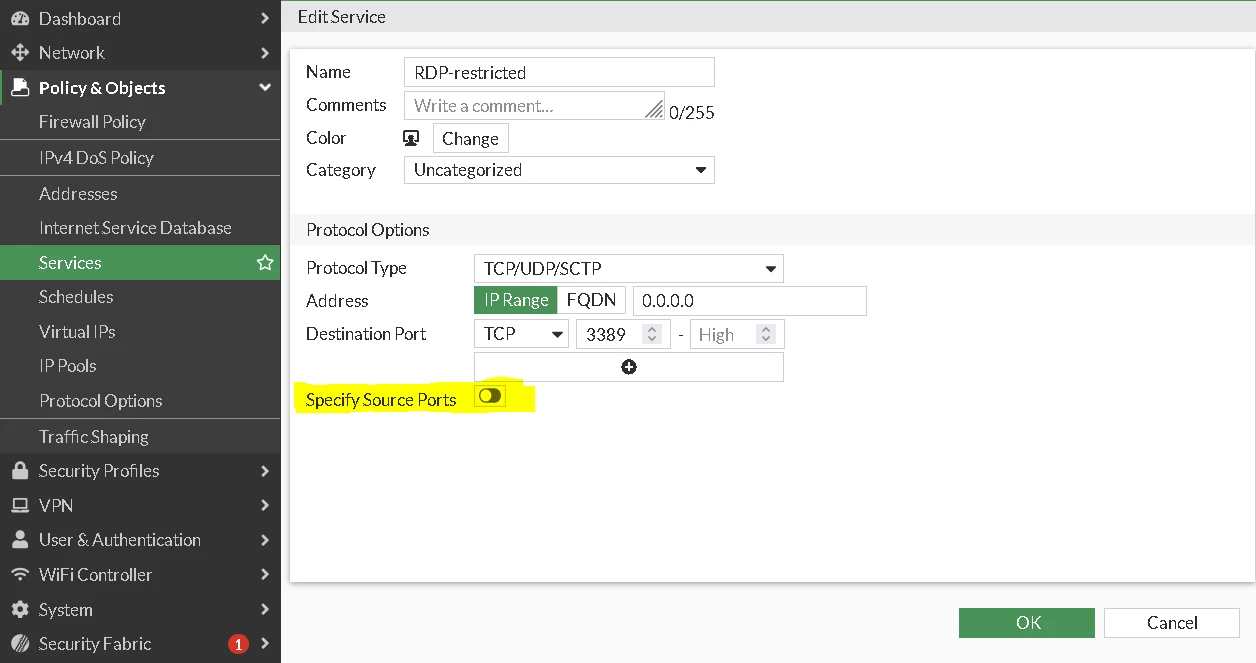
  • After that, it is possible to enable the 'Specify Source Ports' switch and specify the lower and upper range of ports.

pic2.PNG


pic3.PNG


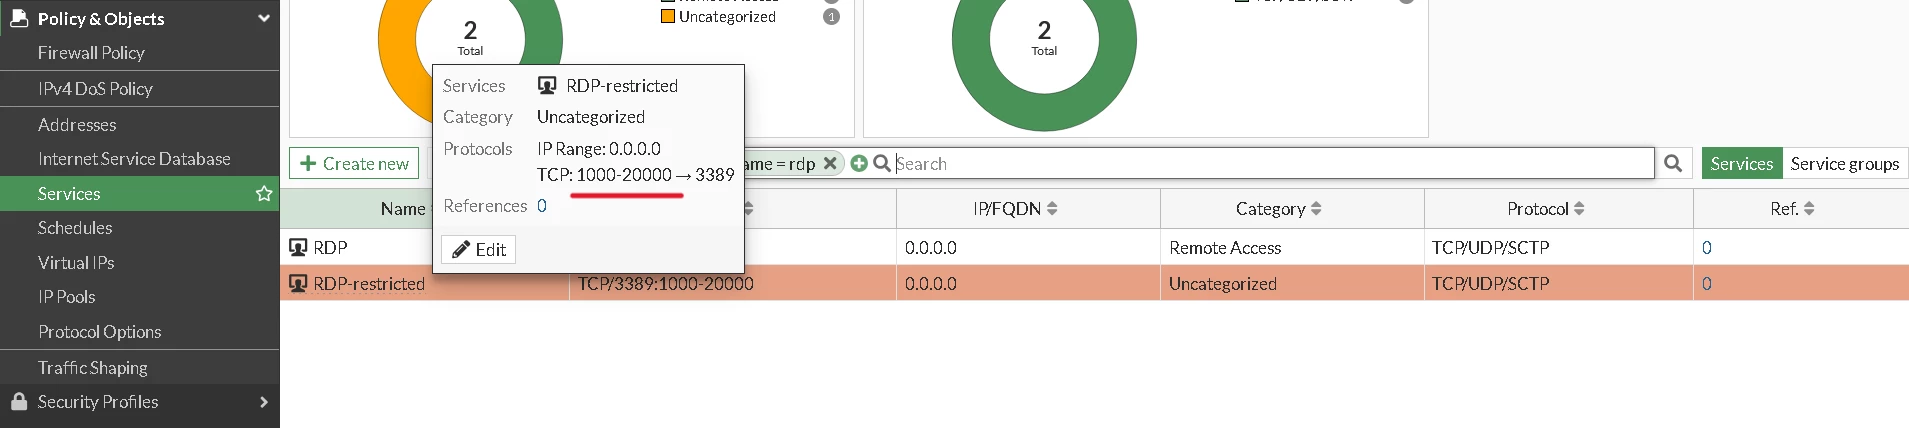
  • Once it is configured, it is possible to hover over the newly configured service 'RDP-restricted' and confirm that the source port range is changed to 1000-20000.


pic6.png


Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!