


Technical Tip: Restricting services through a FortiGate
Description
Solution
Controlling Firewall Services is part of policy creation. By default, a Firewall policy has the 'ANY' service group chosen as the group of services in a policy.
In this scenario, an administrator will group three services to allow.
Create a new Firewall policy under Firewall -> Policy -> Create New.
As part of this step, users will select which service to allow, deny, or send through a VPN tunnel. With no new service groups created, only the default services are available.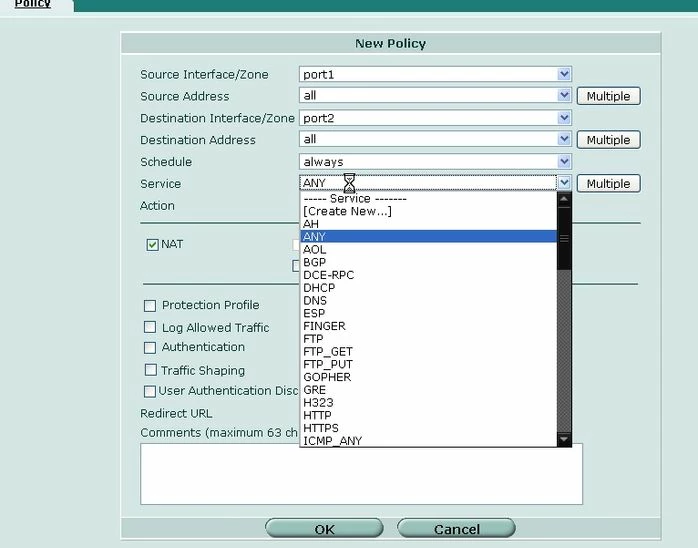
Administrators have all the FortiGate 'Predefined' services to choose from by default. These can be seen in the Firewall -> Service menu.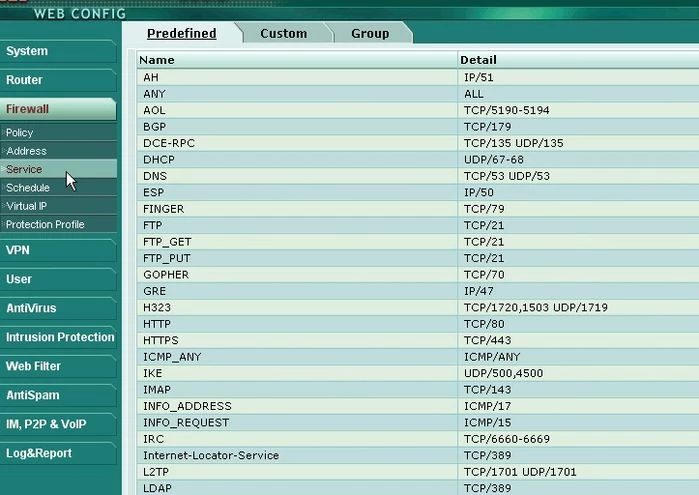
In the Firewall Service menu, users can create a new group. This is done by selecting Create New under Firewall -> Service -> Group tab.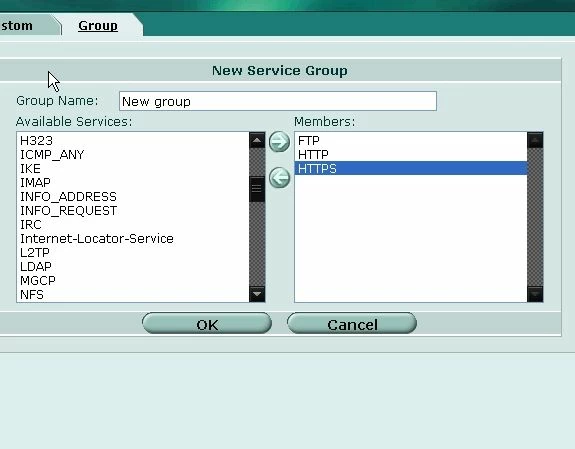
With member services grouped in a new group, this group can be used in a policy of any action type.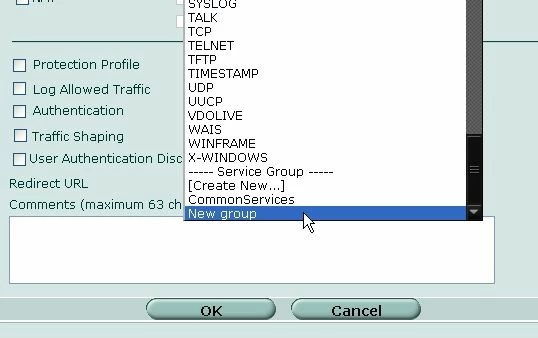
These steps can be applied to an Accept, IPSec, Deny, or SSL VPN policy. By default, the policy list is followed by an implicit deny. This means that if a policy has not been created to allow a service, then it will not be allowed through the FortiGate.
Note:
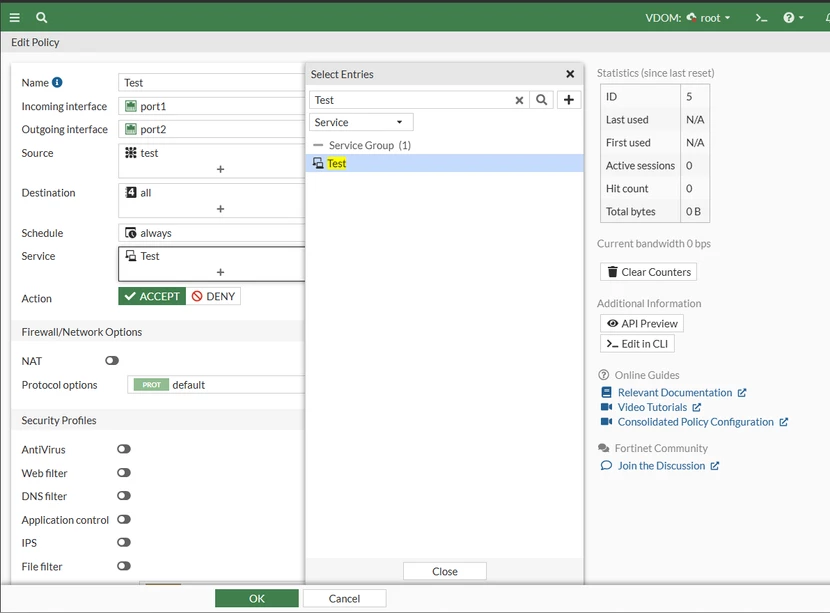
On the newer versions of the FortiOS, in this case, the branches v7.4.x, v7.6.x, a Service Group can still be configured and used on the firewall policy, but the view will be different, as seen below:
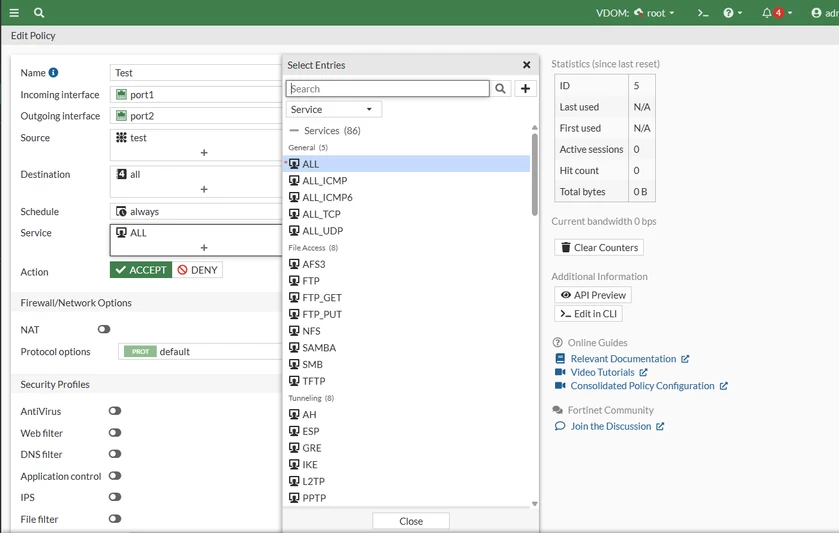
The Service entries:
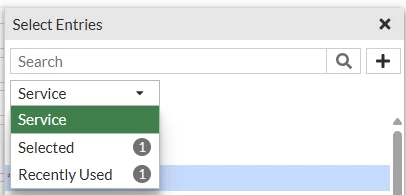
To create a Group, select the + icon:
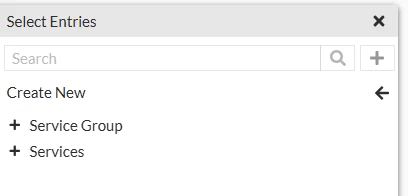
Add Services:
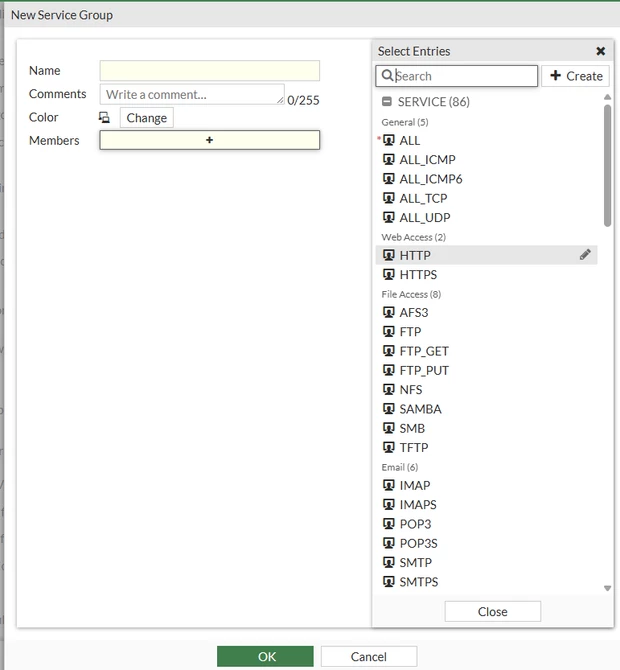
Add the new entry to the Firewall Policy:
Note: Starting in version 7.4, the behavior of how traffic logs display when a service group is used in a firewall policy has changed. The application name column now shows the service group name instead of listing the individual matching service. In earlier versions, even when a service group was used in the policy, the application name column displayed the names of the individual services.

