
Technical Tip: Restrict connection IP in SDP header for SIP traffic with HNAT enabled
Description
This article describes how to configure the FortiGate to maintain the same contact (c) IP in the SDP header.
This article applies when HNAT is enabled.
When HNAT is enabled, FortiGate will replace the contact IP in the SDP header with the incoming ISP IP. This is the desired HNAT behavior.
Technical Tip: FortiGate Hosted NAT Traversal for SIP
Scope
FortiOS.
Solution
When an audio issue is faced, it is possible to check whether the connection IP (which will be used for RTP if no other RTP server is specified) is correct or not, after the traffic passes the FortiGate.
For example, given the following network topology:
VOIP ISP (10.11.12.13) <-------> VOIP GW (LAN: 172.20.1.6) <--------> (MZ-V0700) FortiGate (DMZ-UAT-WEB) <-------> SIP Server (172.16.40.201)
MZ-V0700 <- Incoming interface.
DMZ-UAT-WEB <- Outgoing interface.
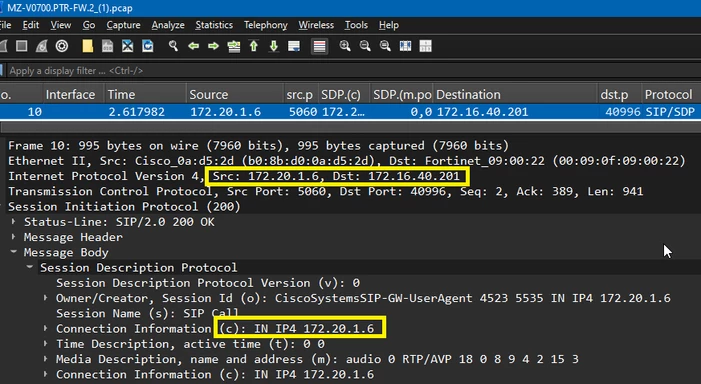
When the traffic comes to interface MZ-V0700:
(IP header) src IP: 172.20.1.6
(IP header) dst IP: 172.16.40.201
(SDP header) connection IP: 172.20.1.6
But when the traffic is passing through the FortiGate out of interface DMZ-UAT-WEB:
(IP header) src IP: 172.20.1.6
(IP header) dst IP: 172.16.40.201
(SDP header) connection IP: 10.11.12.13 (ISP IP)
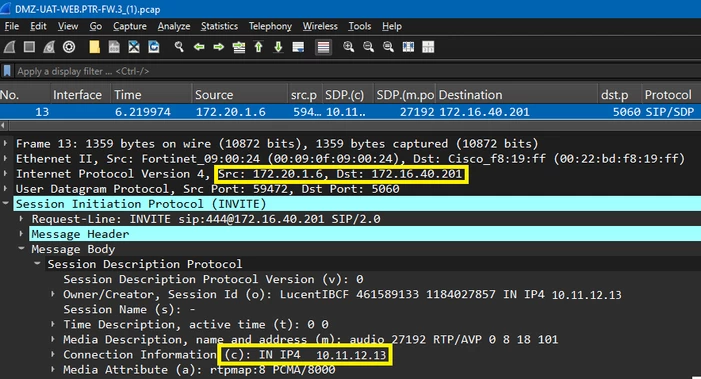
The correct connection IP should be 172.20.1.6 however, when the traffic is leaving FortiGate, the (c) IP is changed to 10.11.12.13
To fix this behavior, SIP ALG must be enabled:
config system settings
    set default-voip-alg-mode proxy-based
end
FortiGate SIP ALG (even in proxy mode):
Does not rebuild SDP bodies completely
Does not enforce RFC 4566 precedence rules when forwarding SDP
Does not strip conflicting session-level
c=lines
And further, to disable this change performed by HNAT and restrict the connection IP to be the same as the source IP:
config voip profile
    edit VoIP_HNT  <- Use this profile in the firewall policy.
        config sip
             set hosted-nat-traversal enable
             set hnt-restrict-source-ip enable
             set nat-port-range
             set strict-register
         end
end
Note:
None of these influence SDP normalization logic
Clear the sessions for port 5060 to restart existing sessions and apply the change to the new ones.
diagnose sys session filter clear
diagnose sys session filter dport 5060
diagnose sys session clear
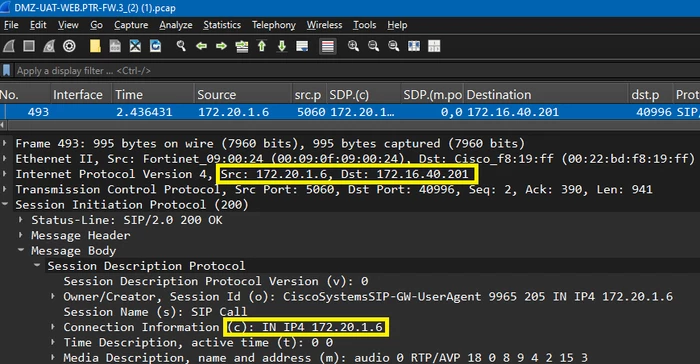
Now, when the traffic is leaving from the FortiGate, the contact IP will be the same as the source IP: