Create FQDN address objects for the Claude and Anthropic domains. These address objects are used by the Web Proxy profile so that the HTTP header is injected only for Claude-related traffic.
config firewall address
    edit "claude.ai"
        set uuid 1e25cc0c-8043-51f1-c344-cf02ffe07812
        set type fqdn
        set color 9
        set fqdn "claude.ai"
    next
    edit "api.anthropic.com"
        set uuid 25df68fe-8043-51f1-8adb-d40183e05817
        set type fqdn
        set color 9
        set fqdn "api.anthropic.com"
    next
    edit "claude.com"
        set uuid 2c5f10da-8043-51f1-f087-270cca9f904e
        set type fqdn
        set fqdn "claude.com"
    next
    edit "anthropic.com"
        set uuid 324679ca-8043-51f1-5c31-ef052d3ed019
        set type fqdn
        set fqdn "anthropic.com"
    next
end
Configure the Web Proxy profile.
Configure a Web Proxy profile to inject the HTTP header 'anthropic-allowed-org-ids' into requests destined for Claude.
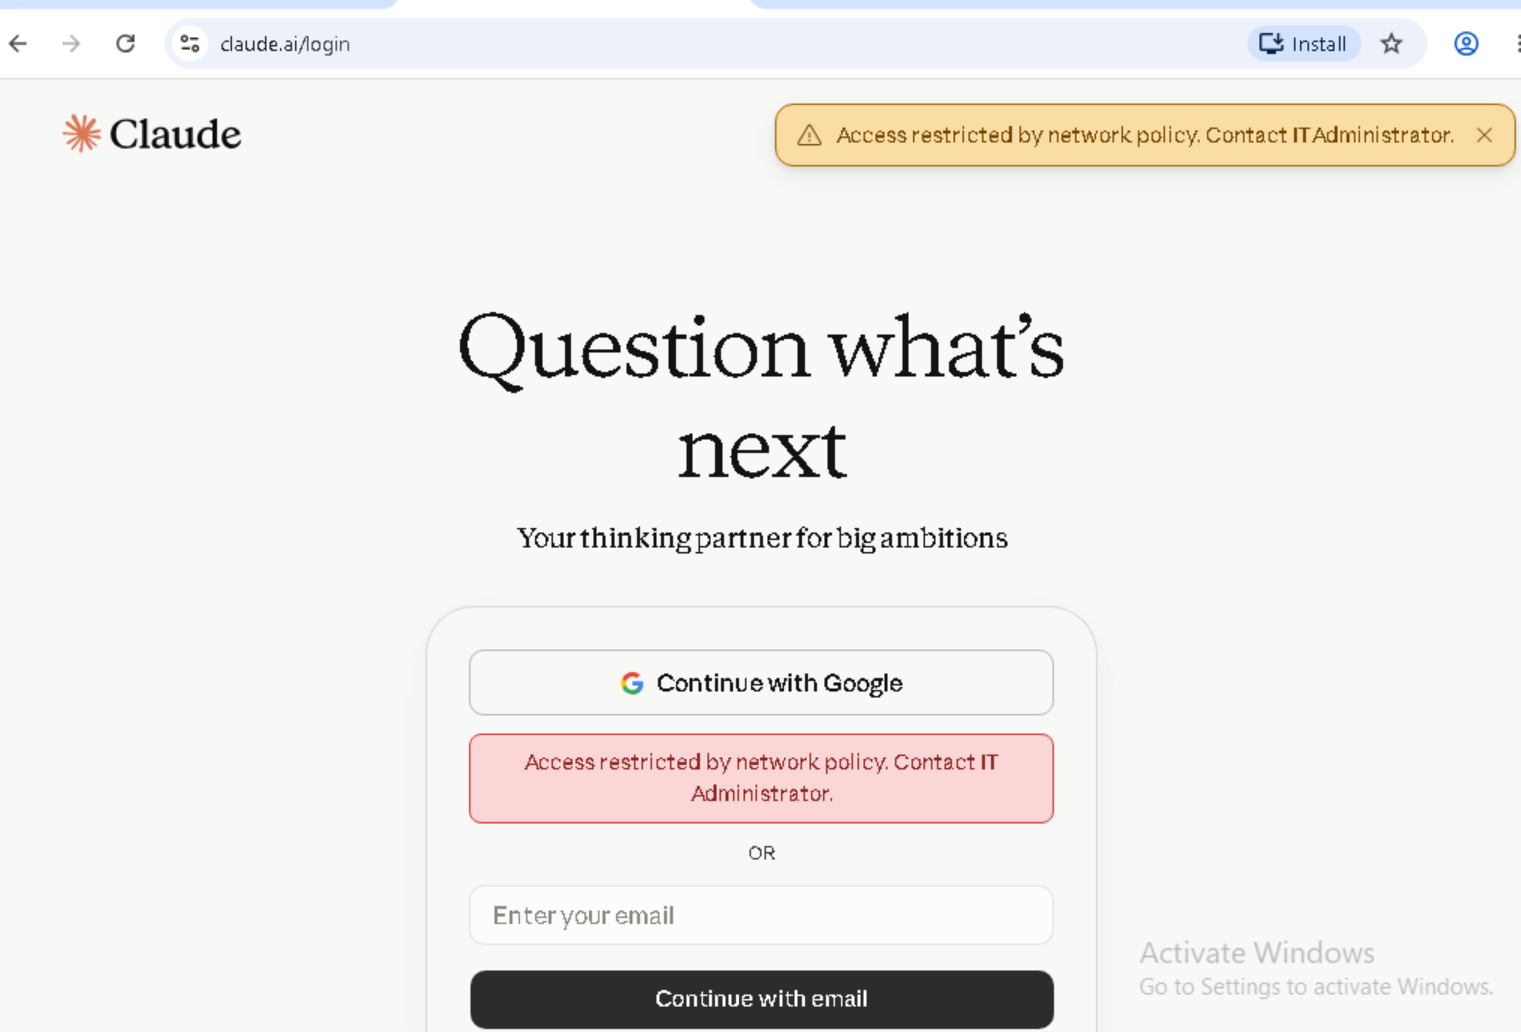
When users access Claude, FortiGate adds this header to the request. Claude verifies the Organization ID contained in the header and permits authentication only if the user's account belongs to one of the specified organizations.
For more information, see Restricted SaaS access.
Note: To use the web-proxy profile, the Firewall policy should be in Proxy mode. Deep inspection must be enabled on the Firewall policy.
config web-proxy profile
    edit "Claude-Tenant-Restriction"
        config headers
            edit 1
                set name "anthropic-allowed-org-ids"
                set dstaddr "claude.ai" "api.anthropic.com" "claude.com" "anthropic.com"
                set content <org-uuid-1>
            next
        end
    next
end
Replace <organization-uuid> with the Claude Organization ID.
To locate the Claude Organization ID:
Members of Claude Enterprise can find the Organization ID in either of the following locations.
To add multiple organization UUIDs, specify multiple Organization IDs separated by commas.
Example:
config web-proxy profile
    edit "Claude-Tenant-Restriction"
        config headers
            edit 1
                set content "<org-uuid-1>,<org-uuid-2>"
            next
        end
Webproxy profile needs to be enabled on the Firewall policy through the CLI:
config firewall policy
    edit 1
        set webproxy-profile "Claude-Tenant-Restriction"
    next
end
Add the Webproxy profile and deep inspection to the Firewall Policy.
config firewall policy
    edit 1
        set name "Claude test"
        set uuid 1c598240-7f46-51f1-315c-0ba2895ee154
        set srcintf "port4"
        set dstintf "port1"
        set action accept
        set srcaddr "all"
        set dstaddr "all"
        set schedule "always"
        set service "ALL"
        set utm-status enable
        set inspection-mode proxy
        set webproxy-profile "Claude-Tenant-Restriction"
        set ssl-ssh-profile "deep-inspection"
        set webfilter-profile "default"
        set logtraffic all
        set nat enable
    next
end
After the configuration is complete:
Users belonging to one of the configured Claude organizations can sign in successfully. Users attempting to sign in with a personal Claude account or an organization that is not included in the allow list are denied access.
 | 





