




Technical Tip: Resolving IP address conflicts when FortiGate is the DHCP Server
Description
This article describes one method to avoid IP address conflicts on a FortiGate unit.
Scope
FortiGate is being used as a DHCP server.
Solution
Background:
IP address assignments to end devices should be unique.
Most devices will only hold a single ARP entry for a given IP address. If two or more devices are configured to use the same IP address on the network, this is called an IP address conflict and results in intermittent connectivity issues.
Common Causes:
Typically, IP conflicts are caused when either:
2 devices were accidentally configured with the same static IP address.
A device was accidentally configured with a static IP address that belongs to the DHCP pool.
2 DHCP servers accidentally have pools in the same range of IP addresses, and are each independently assigning their clients the same IPs.
DHCP conflict detection in FortiOS:
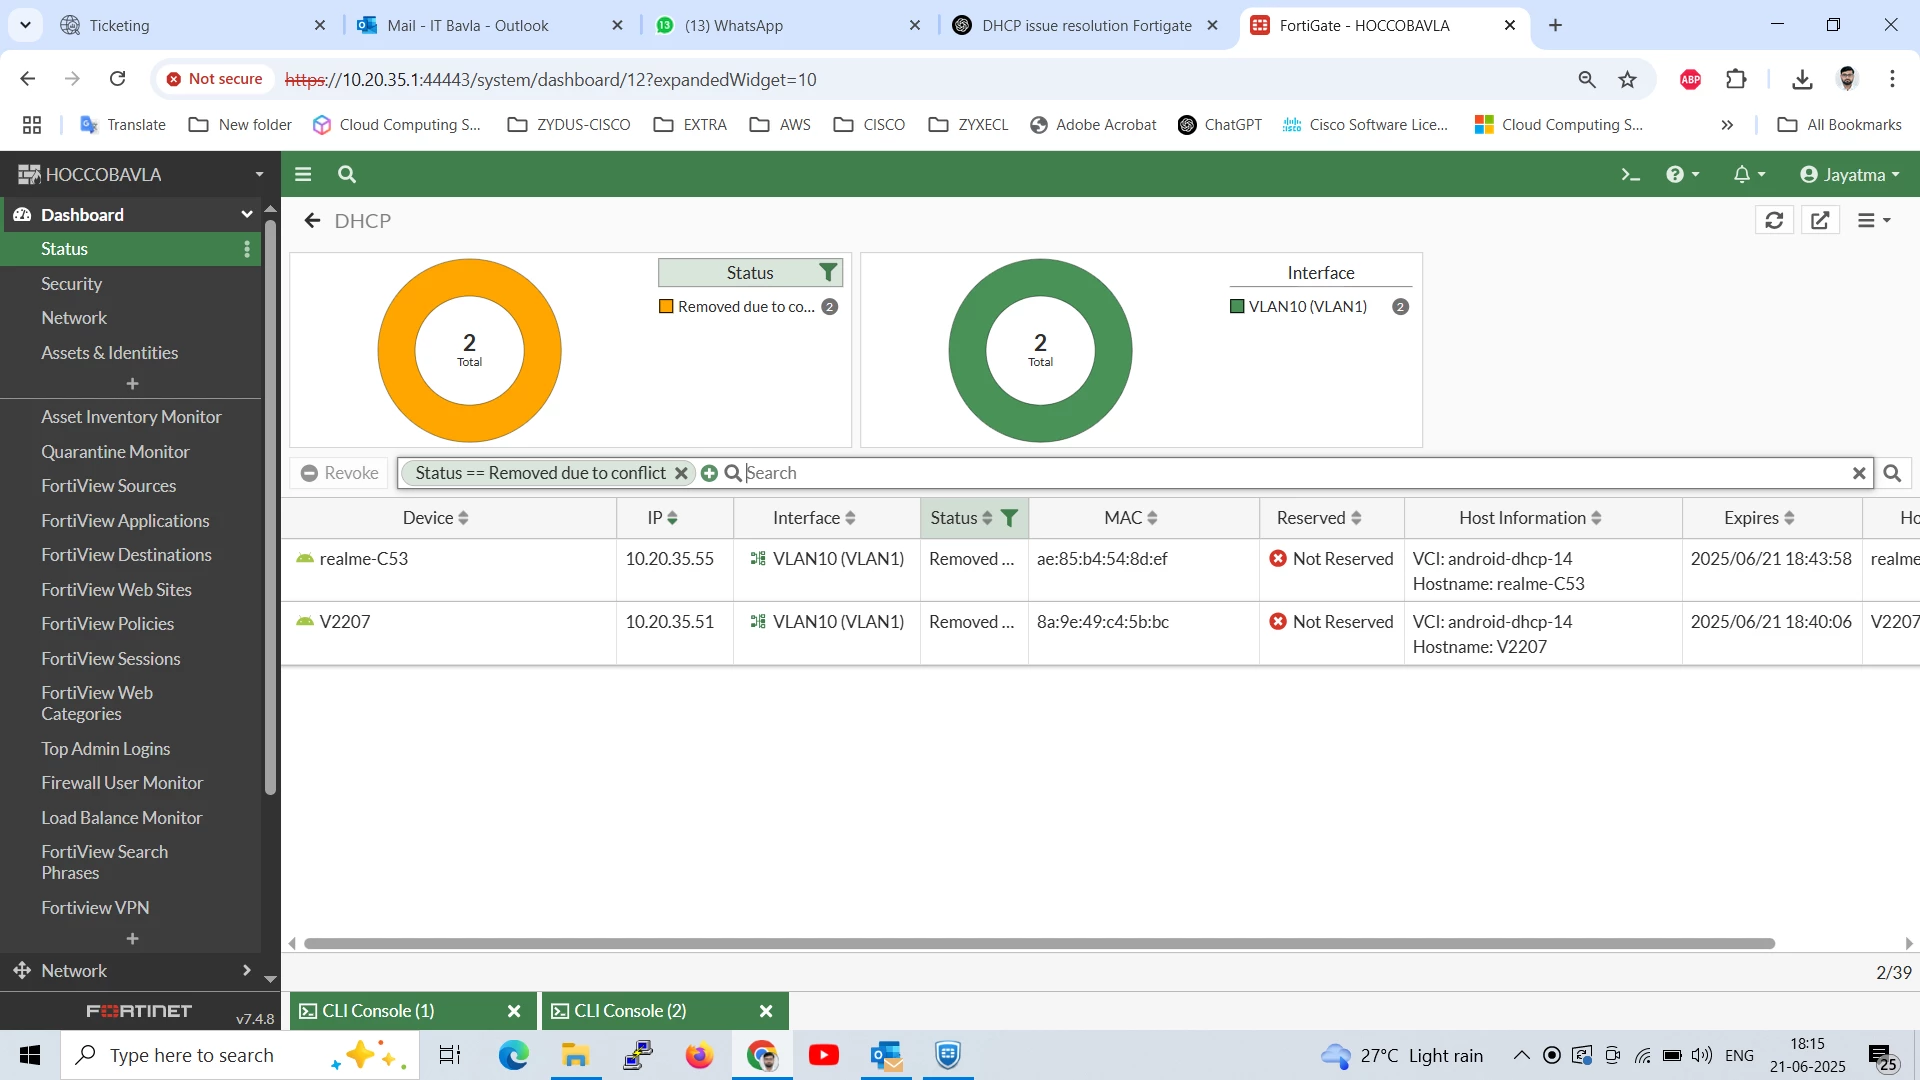
FortiGates unit has a DHCP conflict monitor available.
Adjust the timeout under any DHCP server entry.
config  system dhcp server
    edit <DHCP server>
        set conflicted-ip-timeout <60 ~ 8640000 seconds (1 minute ~ 100 days)>
    next
end
Possible Actions:
Check if there is a device that is causing conflict if the IP is detected on the 'get system arp' but not listed on the 'execute dhcp lease-list.'.
If there is an entry for the IP that is not leased by FortiGate, it means that it is either statically assigned or leased by another DHCP server.Get the MAC address shown on the 'get sys arp' and use a MAC address finder to know the device type to narrow down the conflict source.
In some cases, this is caused by a VM set with a static IP that is running on a computer.Use a device scanner to check devices that are connected to the network. There also might be a rogue router that is leasing a DHCP IP.
Starting version v7.6, a new feature called 'ip-conflict-detect' has been introduced:
config system global
set ip-conflict-detection enable
end
If an IP conflict is detected, the FortiGate will generate a log at Log&Report -> System Events -> General System Events.
This feature allows the FortiGate to monitor the network continuously via ARP (IPv4) and NDP (IPv6) to identify any device, not just DHCP clients, that might be 'stealing' or duplicating an IP address already assigned to an interface.
