| Consider the following important requirements before implementing this solution: - In earlier versions before v5.6.0, FortiOS will report the client’s public IP address instead of the assigned tunnel IP address in the 'Framed-IP-Address' attribute value in the Access-Request packet:
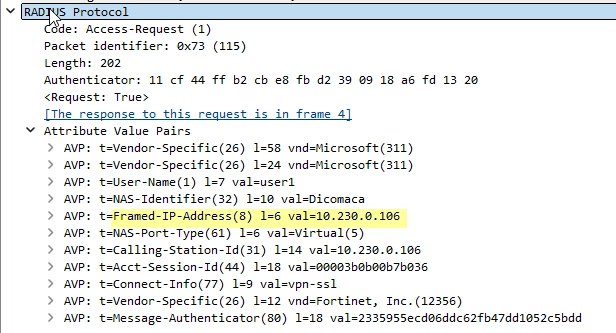
- The attribute 'Framed-IP-Address' will be included in the RADIUS Accounting-Request Start message if the remote RADIUS server assigns an IP address to the user in the Authentication Accept message. Otherwise, it will be included only in Interim-Updates and the Accounting Stop message.
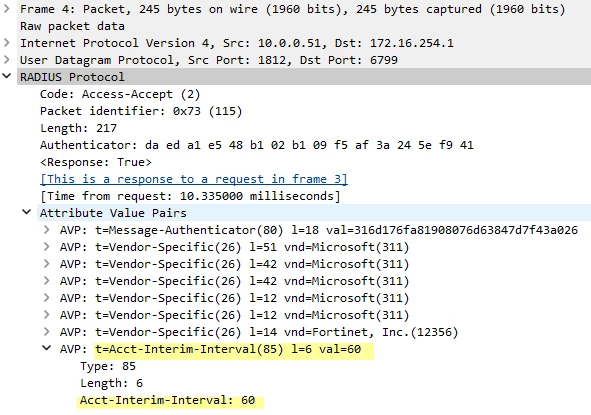
- The Interim Accounting-Request will not be sent unless the radius server sends AVP: 'Acct-Interim-Interval' in the 'Access-Accept' message. The Interim-Updates feature must be enabled on FortiGate under the RADIUS profile.
- The minimum update interval for interim accounting messages is 600 seconds. For versions 7.0.0 or newer, this can be set from 60 to 86400 seconds.
There are two steps to complete this configuration:
- Configure SSL VPN access for RADIUS users. More information in the following document:
SSL VPN with RADIUS and FortiToken mobile push on FortiAuthenticator
- Configure FortiGate to send RADIUS Accounting:
config user radius
edit <RADIUS_PROFILE_NAME>
set acct-interim-interval 60 <----- Enable sending of Interim Accounting config accounting-server
edit 1
set status enable <----- Enable sending of RADIUS Accounting message.
set server <Radius_Server_IP> <----- Specify the IP address of the server.
set secret <password> <----- Secret used to authenticate with the server.
next
end
next
end
- Ensure the RADIUS server is configured to send AVP 'Acct-Interim-Interval:60' in the Access-Accept message.
Example:
Verification of Configuration:
The following packet captures show the effect of the above configuration in action. 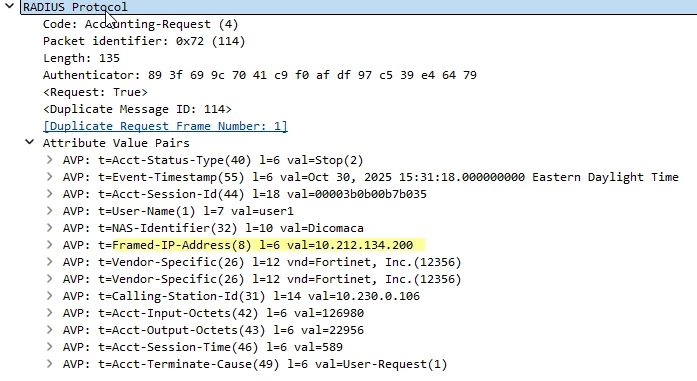 The RADIUS server will receive the IP address assigned to the VPN SSL user connection. |