



Technical Tip: Protocol Port Mapping in SSL/SSH deep-inspection profile
Description
This article describes that Firewall policies have two modes of operation: proxy or flow based, both modes support deep-inspection. It is important to ensure that the SSL/SSH inspection profile is configured correctly for each mode, else it may not work as expected.
Scope
FortiGate.
Solution
In SSL/SSH inspection profile, once the inspection method is configured for 'Full SSL Inspection', there will be an option to 'Inspect All Ports' or to only inspect certain commonly known SSL ports such as HTTPS, SMTPS, POP3s under the 'Protocol Port Mapping' option.
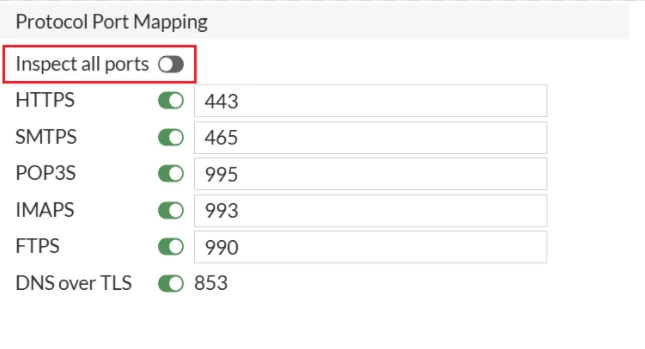
CLI configuration:
config firewall ssl-ssh-profile
edit "test
config https
set ports 443
set status deep-inspection
set quic inspect
end
config ftps
set ports 990
set status deep-inspection
end
config imaps
set ports 993
set status deep-inspection
end
config pop3s
set ports 995
set status deep-inspection
end
:
:
:
end
Firewall policy in proxy mode:
When the firewall policy is in proxy-mode used, either the option 'Inspect all ports' or only inspect certain ports can be used. When firewall policy is in proxy-mode FortiGate listens to the ports that are configured in the SSL/SSH profile.
For example: by default, it listens to HTTPS port 443.
FortiGate will ignore other ports if there is no special port identified.
For example:
If a virus file needs to be blocked through port 8443, there are two ways:
- Configure port 8443 under https in the SSL/SSH profile.
- Configure inspect-all in SSL/SSH profile.
Firewall policy in flow mode:
When firewall policy is in flow mode, FortiGate scans all ports. FortiGate does not check the ports configured in the SSL/SSH profile.
For example, with the default SSL profile which only identifies port 443 under HTTPS, but if a virus file is downloaded, FortiGate can still block the virus file.

