mricardez
Staff
Staff
February 22, 2022

Technical Tip: Preventing certificate warnings using captive portal

  • February 22, 2022
  • 0 replies
  • 33621 views

Description

This article describes how to configure certificates in FortiGate to avoid certificate warnings using a captive portal in the firewall policy.

Scope

FortiGate v6.0, v6.2 and earlier.

Solution

When the authentication LDAP is enabled in the Firewall Policy, the FortiGate will trigger the Captive Portal authentication for users to get their user/passwords and validate them against the LDAP server.


By default, FortiGate will use port 1000 to authenticate HTTP and 1003 to HTTPS traffic.

 config system global
    set auth-http-port 1000
    set auth-https-port 1003 


When FortiGate received traffic from an unauthenticated user IP, the FortiGate proxied the connection and sent an HTTP redirect to the user's browser, in order to connect to FortiGate's internal IP to port 1000/1003 to authenticate.


For example, the unit debian-fortinet (192.168.81.101) does not belong to the AD domain, but using LDAP authentication, the device will authenticate against the LDAP server.
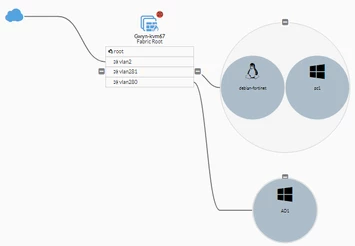
 

mricardez_0-1645462306815.png


When the user in Debian-Fortinet browses to a site with HTTPS (i.e 'https://www.google.com'), the browser will show the following error, since the FortiGate will intercept the connection and use the Fortinet_CA_SSL certificate to sign the certificate on the fly to Google, so the browser will identify it as invalid since it is not a public CA.


The FortiGate needs to intercept the HTTPS connections and impersonate the end site because it needs to inject the HTTP messages to redirect the connection to 'https://fortigate_ip:1003' to authenticate the user.
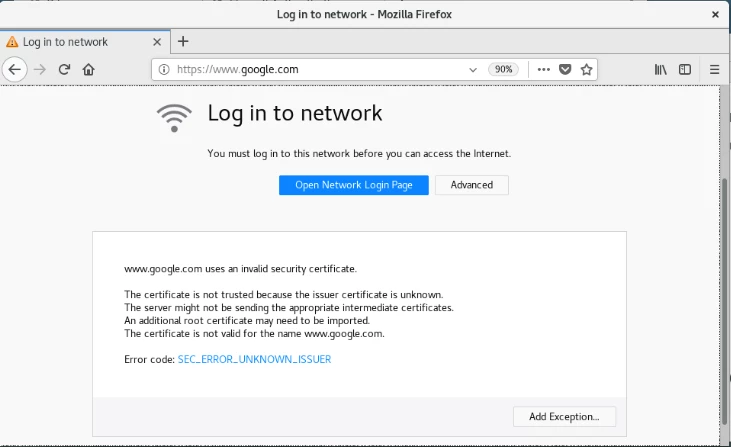
 

mricardez_0-1645465495256.png


To avoid a certificate warning in the browser during the captive portal authentication, it is possible to apply the following procedure:
 

  1. A DNS record is needed for fortigate_ip because a valid certificate for that IP address will be necessary. The fortigate_ip is the internal IP address of FortiGate, usually the default_gateway  of the LAN's  PC.


nslookup captiveportal.markoz.local
Server: UnKnown
Address: 192.168.80.1
Name: captiveportal.markoz.local
Address: 192.168.81.254


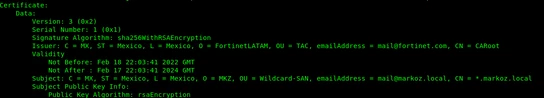
  1. A valid certificate with an SAN issued by a public CA, a wildcard certificate (*.markoz.local) has been used for lab purposes.


mricardez_1-1645469614668.png


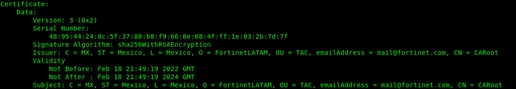
  1. In the LAB environment no access to sign the certificate with a Public CA, so a private CARoot has been created to sign the certificate of 2).


mricardez_2-1645469718574.png


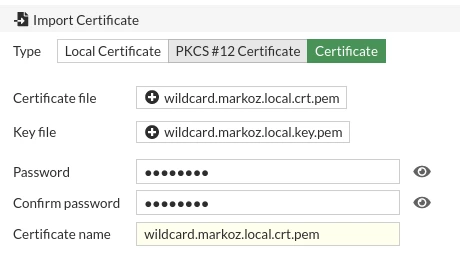
  1. Import the wildcard certificate to FortiGate. The CRT and Private Key have been imported since the CSR and CRT were created external to FortiGate. If the CSR in FortiGate is created through the GUI, it is only necessary to import the CRT received from the CA Public.


mricardez_3-1645469851637.png


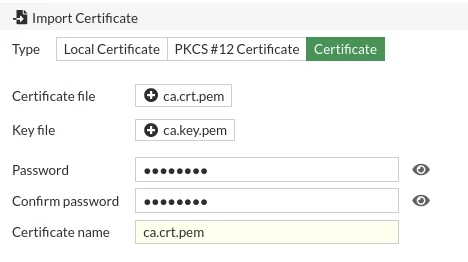
  1. Import the CARoot Private to FortiGate.


mricardez_0-1645470204061.png


Note:

If the wildcard certificate was issued by a Public CA, this step can be skipped. However, the issuer of that wildcard certificate [sometimes an intermediate certificate] should be added as 'Remote CA' in the FortiGate if not already there.


To check for existing Root CA certificates, follow this article: Technical Tip: How to View the Default Trusted CA Certificates on FortiGate. To verify the certificate chain, follow this article: Technical Tip: How to avoid certificate error message by chaining Root CA and Intermediate CA certificates on FortiGate.


In addition, sometimes the WIFI client may fail to obtain the complete chain of this certificate signed by the public CA and still receive the certificate warning. That could be because the client's browser failed to download the CA cert from the Internet, as the Internet access was still not available. The solution for this situation can be found in the following article:

Troubleshooting Tip: Prevent certificate warning when using public CA signed certificate for captive portal


  1. Configure the FortiGate to use the following URL as captive portal.


config firewall auth-portal
    set portal-addr "captiveportal.markoz.local"
end


  1. Configure the certificates as follows: the wildcard will be used when the browser connects to captiveportal.markoz.local, and the ca.crt.pem will be the CAPrivate certificate used to impersonate the first URL attempted in the browser URL.

 config user setting
    set auth-cert "wildcard.markoz.local.crt.pem"
    set auth-ca-cert "ca.crt.pem"
    set auth-secure-http enable
end


Optionally, in the auth-ca-cert, it is possible to use the default CAPrivate Fortinet_CA_SSL.


The Fortinet_CA_SSL is the certificate used on the deep-inspection profile of SSL/SSH Inspection since all browsers in the LAN must have it installed to avoid warning certificates during regular browsing when deep-inspection has been enabled on firewall policies.


The next time a user tries to browse to an HTTPS site, the FortiGate will intercept the connection and will redirect to 'https://captiveportal.markoz.local:1003' to authenticate the user without a certificate warning.
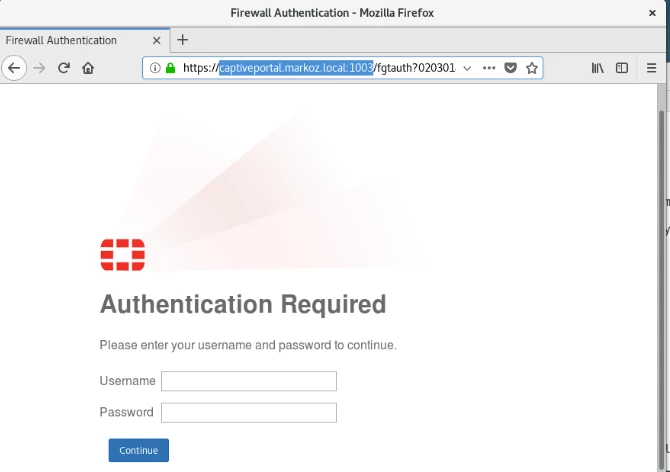
  

mricardez_0-1645471296623.png


Related articles:

Technical Tip: Using secure authentication (HTTPS) on a FortiGate and redirecting the authentication page

Technical Tip: How to change the Captive Portal certificate

Technical Tip: Change the captive portal port

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!