



Technical Tip: Prevent FortiGate DNS being overwritten by mobile provider DNS from FortiExtender connection
Description
This article describes the situation when utilizing a FortiExtender interface for SD-WAN and the mobile ISP DNS is overriding the FortiGate system DNS.
This can be a problem as often DNS servers provided by the mobile carrier only allow connections for carrier clients.
In this case, DNS traffic across all other SD-WAN member interfaces will fail.
This behavior is caused by the ‘set dns-server-override‘ being enabled by default on interface settings and the fact that often a mobile ISP provides services via DHCP.
Scope
FortiGate.
Solution
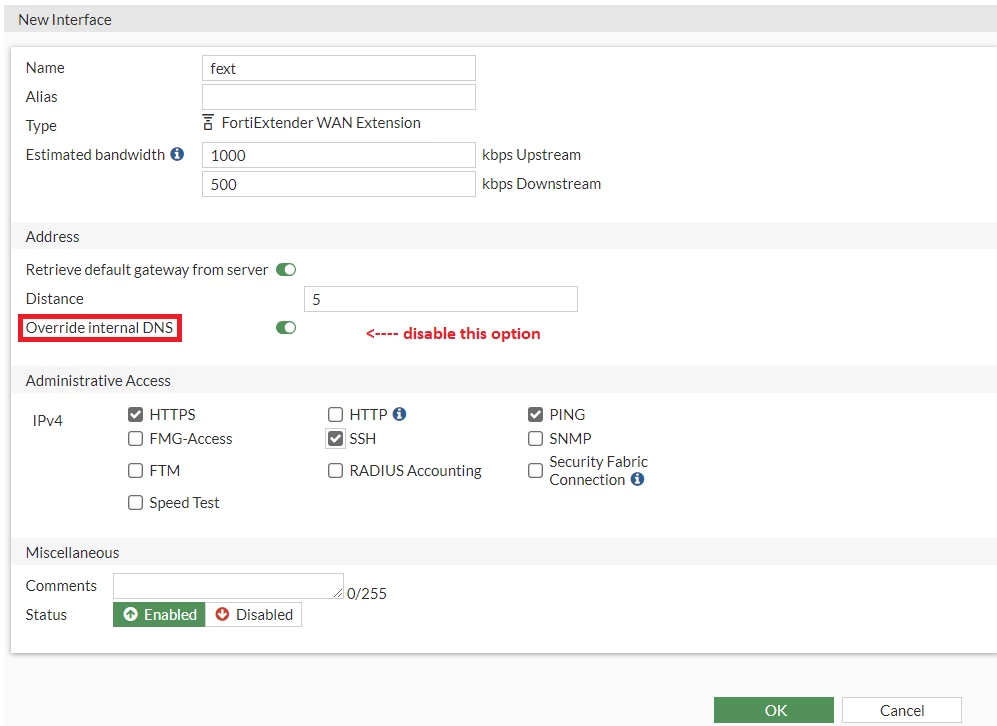
To correct it, disable this setting under the FortiExtender virtual interface on the FortiGate.
Disabling this prevents the interface from using a DNS server acquired via DHCP or PPPoE.
config system interface
edit <name of your FortiExtender interface>
set dns-server-override disable
end
Note:
This is also applicable for other internet providers or LTE modems that utilize DHCP. The 'Override internal DNS' option is also available under another interface such as WAN1 or WAN2.

