Technical Tip: Policy Lookup Utility on FortiGate fails with the error 'Unable to find the matching policy given the provided information' for UDP Traffic and FQDN Destination Address Objects
| Description | This article addresses an issue where a policy lookup fails with the error 'Unable to find the matching policy given the provided information' when UDP traffic and FQDN objects are used as the destination address in the tool. |
| Scope | FortiGate v7.4.5, v7.6.2. |
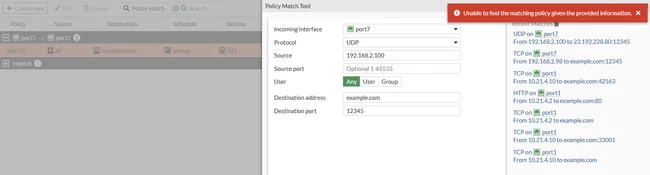
| Solution | When using an FQDN as the destination object, the policy lookup tool for UDP traffic fails but works fine for TCP traffic. Sample config:
config firewall policy
diagnose firewall fqdn list-ip | grep -A 10 example.com GUI lookup for UDP traffic:
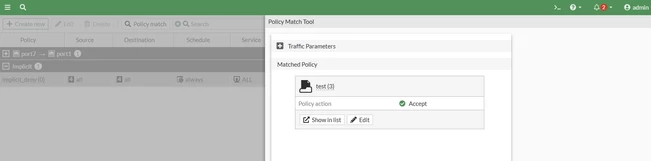
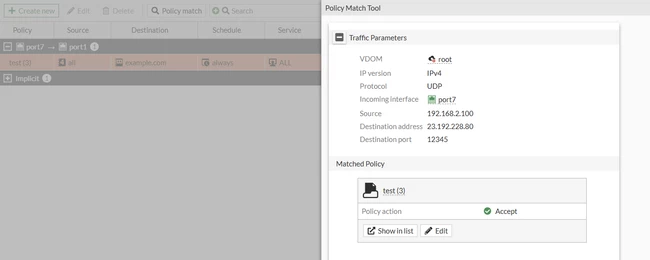
diagnose firewall iprope lookup 192.168.2.98 1234 example.com 12345 17 port7 policy protocol has to be 6(tcp) for HTTP URL! GUI Lookup for TCP traffic:
CLI lookup for TCP traffic:
However, policy lookup works fine with the IP address for the UDP protocol.
Workaround: |