



Technical Tip: Moving an Interface that has existing references to SD-WAN zone using Integrate Interface feature
Description | This article describes how to use the integrated interface feature to move the interface that has references to the SD-WAN zone. |
Scope | FortiGate v7.x. |
Solution | Before FortiGate v7.x:
After FortiGate v7.x (using port1 as an example):
Prerequisite : Enable the SD-WAN feature on the firewall before migrating to the default SD-WAN zone.
From CLI: 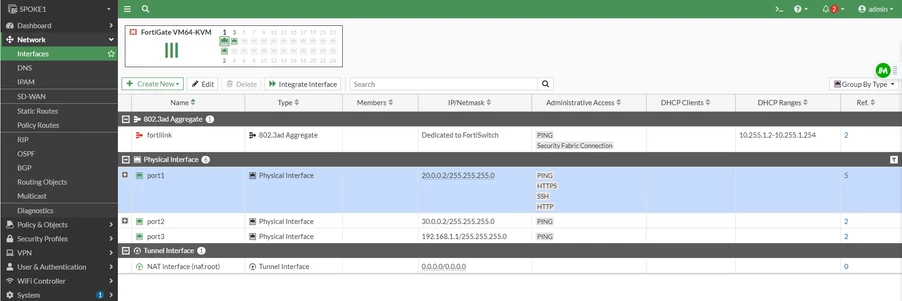
To move the interface to SD-WAN:
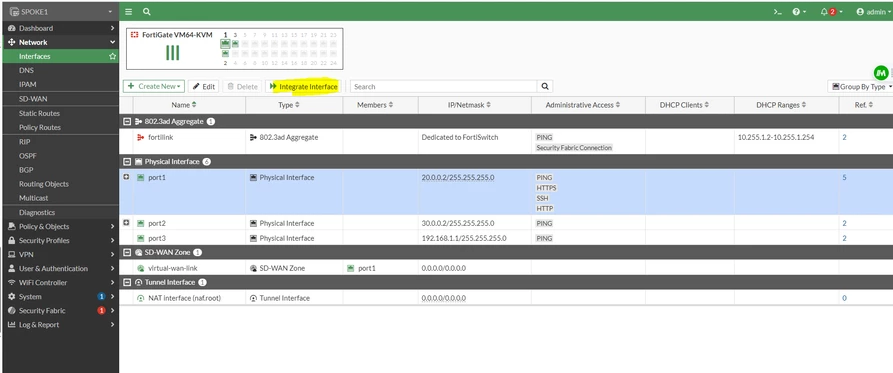
In FortiOS v7.6.x, 'right-click' on the interface and select 'Integrate Interface'. 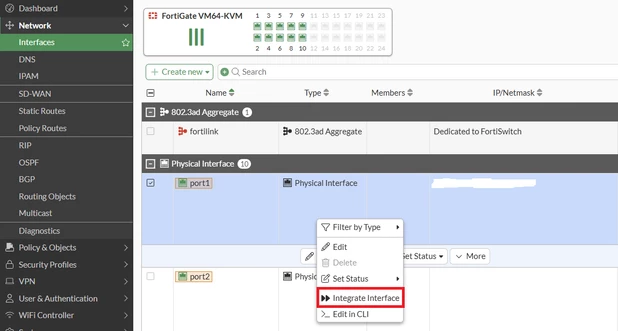
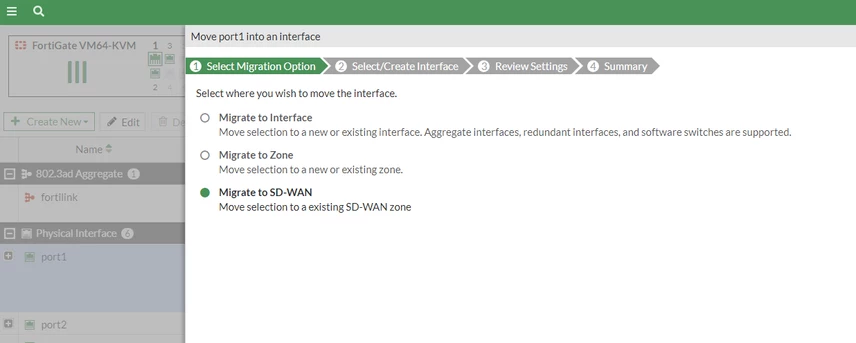
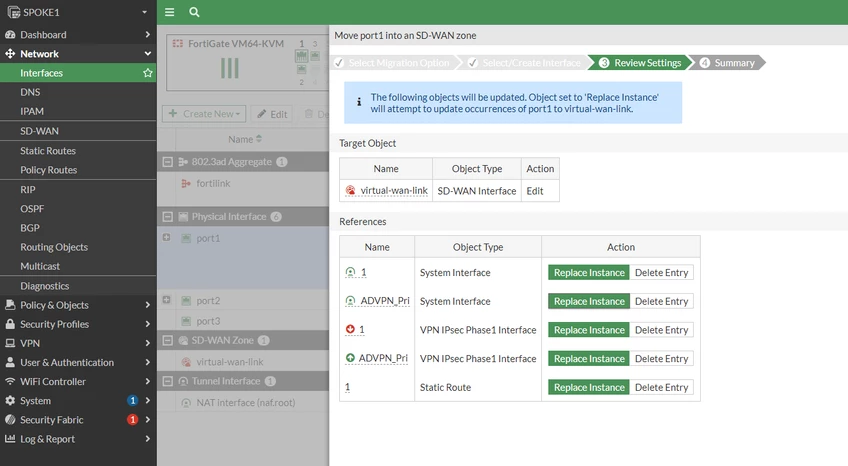
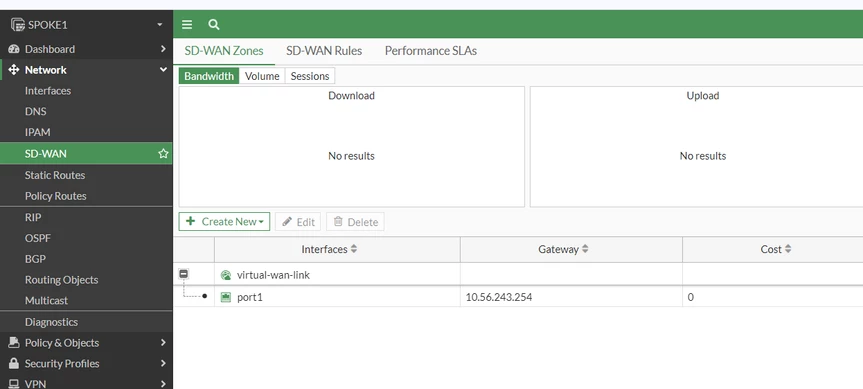
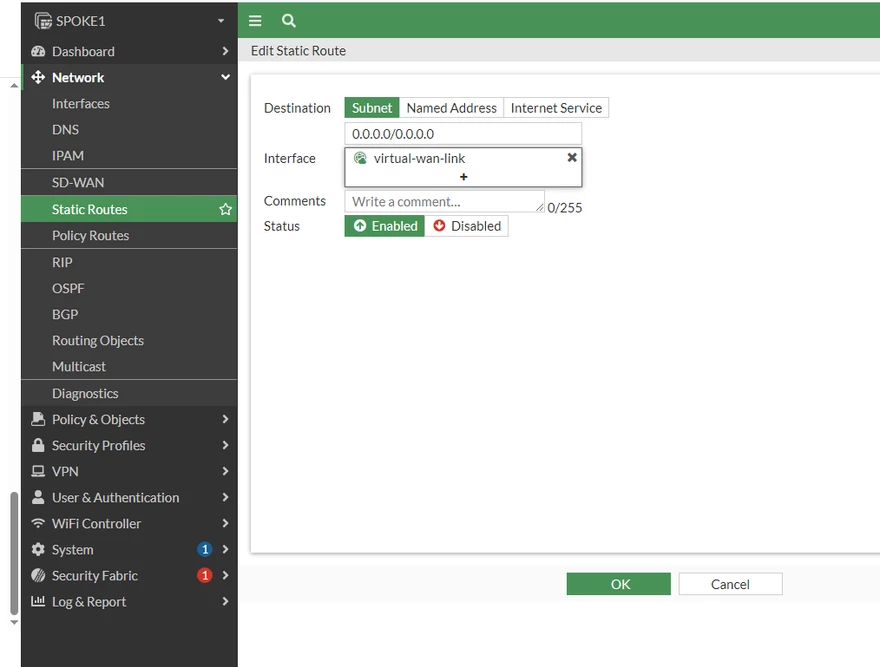
Note: Migration is not supported if the physical or VLAN interface is used in a tunnel configuration (IPsec or SSL VPN). Instead of deleting and reconfiguring the IPSec tunnel again, change the tunnel binding interface to an unused port. This can be reverted to the original interface after successfully integrating into SD-WAN. |

