Technical Tip: Limiting management access to a dedicated management interface by IP
| Description | This article describes how to limit access to the FortiGate dedicated management interface using trust-ip. |
| Scope | FortiGate. |
| Solution | When 'dedicated-to management' is configured, it is possible to limit access using trust-ip. This is similar to what is available with Trusted-Host under 'System Admin'.
Below is the interface port10 that has been set 'dedicated-to management'.
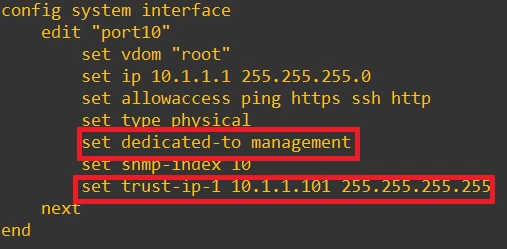
In this example, only 10.1.1.101/32 is allowed access to FortiGate management through this port10 interface. Other IPs would be denied.
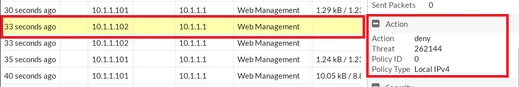
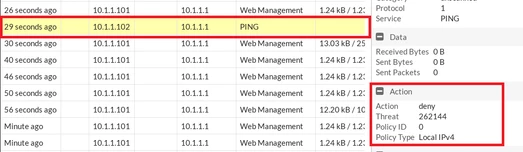
The logs below show denied IPs:
It is possible to add up to 3 IPv4 and 3 IPv6 trust-ips.
Note:
For IPv6 the command is:
edit <interface> next end
Note: Another way to allow only specific IP(s) is by configuring local-in policies to restrict access.
Related documents: |