Technical Tip: limitation of fnsysctl commands in FIPS-CC mode
| Description | This article provides information regarding the limitations on the fnsysctl command when FIPS-CC mode is enabled on a FortiGate. |
| Scope | FortiGate. |
| Solution | When a FortiGate runs in FIPS-CC mode for security compliance, the FortiOS CLI applies strict rules to make sure the device stays within the FIPS security standards.
A good example of this limitation is the fnsysctl limited shell command. It is used for advanced troubleshooting or accessing system tools on a FortiGate. When the device is in FIPS-CC mode, the fnsysctl command is not available because the system prevents access to non-compliant shell operations.
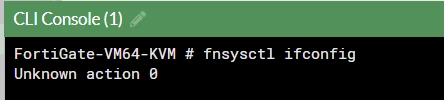
When attempting to run the fnsysctl command, the CLI will return with an error 'unknown action 0' as shown in the example below:
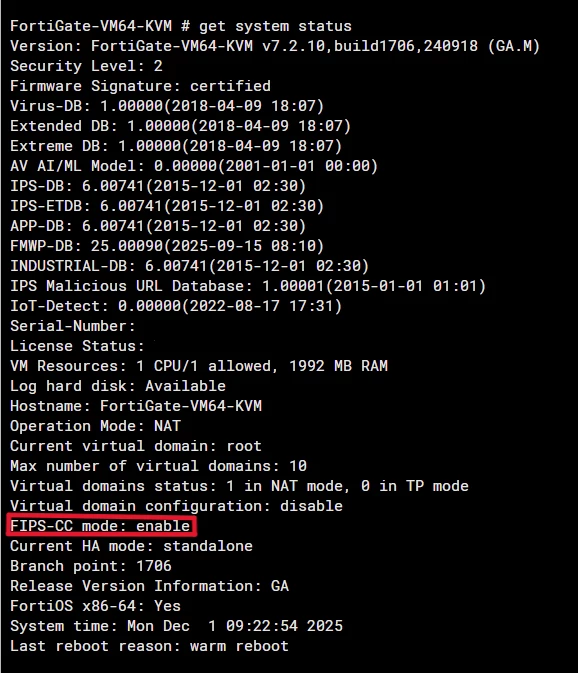
To verify if FIPS-CC is enabled, use the command 'get system status', as shown in the example image below.
Related article: Technical Tip: Usage of 'fnsysctl' command with examples and requirements |