ychia
Staff
Staff
October 6, 2023

Technical Tip: LDAP connection status 'Strong(er) authentication required'

  • October 6, 2023
  • 1 reply
  • 33367 views
Description

This article describes how to fix the LDAP connection status 'Strong(er) authentication required'.


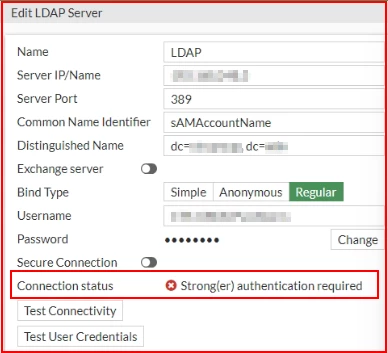
Under Users & Authentication -> LDAP Servers, 'double-click' on the LDAP server name, and the connection status is shown below:


ldap-error.png


Based on the fnbamd debug logs:


2023-08-14 16:06:10 [987] fnbamd_ldap_parse_response-Got one MESSAGE. ID:1, type:bind
2023-08-14 16:06:10 [1009] fnbamd_ldap_parse_response-Error 8(00002028: LdapErr: DS
ID-0C090276, comment: The server requires binds to turn on integrity checking if SSL\TLS are not already active on the connection, data 0, v2580) ---> Error sent by LDAP Server
2023-08-14 16:06:10 [1023] fnbamd_ldap_parse_response-ret=8
2023-08-14 16:06:10 [785] __ldap_done-svr 'Forti-LDAP'
2023-08-14 16:06:10 [755] __ldap_destroy-
2023-08-14 16:06:10 [724] __ldap_stop-Conn with 192.168.xxx.xxx destroyed.
2023-08-14 16:06:10 [216] fnbamd_comm_send_result-Sending result 1 (nid 0) for req1885254761, len=2148
2023-08-14 16:06:10 [789] destroy_auth_session-delete session 1885254761
2023-08-14 16:06:10 [755] __ldap_destroy-
authenticate 'it-administrator' against 'Forti-LDAP' failed!

Scope FortiGate.
Solution

It is required to change the value of the parameter 'ldapserverintegrity' on the LDAP server, which must be equal to '0' or '1' when Secure Connection is disabled in the FortiGate


  1. Locate and then select the following registry subkey: HKEY_LOCAL_MACHINE\SYSTEM\CurrentControlSet\Services\NTDS\Parameters.
  2. 'Right-click' the LDAPServerIntegrity registry entry, and then select 'Modify'.
  3. Change Value data to 0 or 1 (default is 2 depends on Windows OS)
  4. Select 'OK'.

The registry entry has the following possible values:

  • 0: Signing is disabled.
  • 1: Signing is negotiated if supported by both Client and Server.
  • 2: Signing is mandatory.


This is a change on the domain controller unrelated to FortiGate. This change would fix the error message sent by the domain controller.


Since the domain controller, in its role as a server, sends the message to the FortiGate in its role as a requesting client, the reason for the response the server sends must be looked at on the server, not the FortiGate.


Contact the server team handling the domain controller or LDAP server with the recommendation above. There may be a reason that the registry setting is set to what it is. If so, another solution must be found by the team.
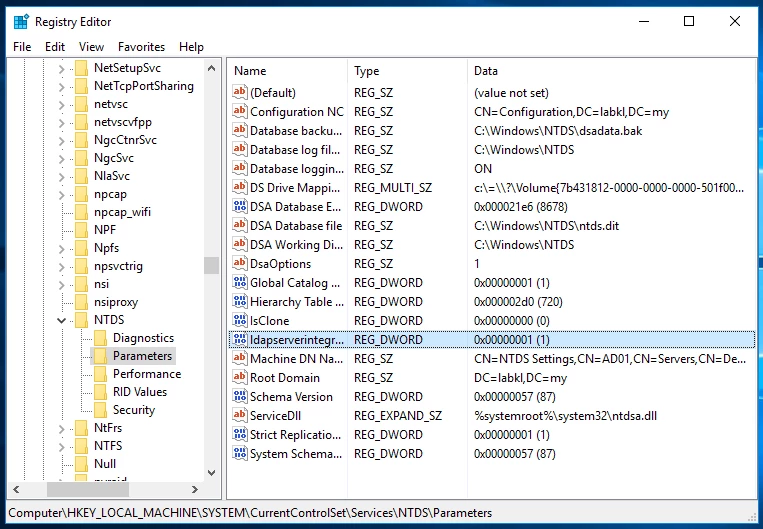
 

Capture.PNG


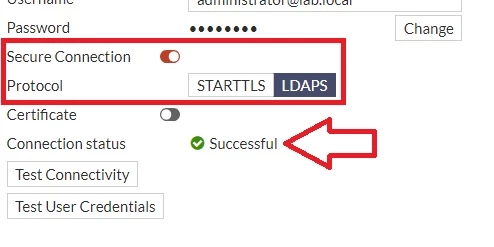
In case of the requirement to have this parameter active, as Microsoft Document advises, it is required to have Secure Connection enabled and LDAPS configured:


image.jpg


Related documents:

Microsoft: 2020, 2023, and 2024 LDAP channel binding and LDAP signing requirements for Windows (KB4520412)

How to create LDAPs: Technical Tip: Configuring LDAP over SSL (LDAPS)

V7.4.4 enhances the security standards for LDAPS by requiring that the server certificate be trusted by FortiOS during the TLS handshake. To comply with this requirement, the CA certificate of the LDAP server must be imported into the FortiGate.: Technical Tip: LDAPS connections no longer work after update to v7.4.4

Troubleshooting Tip: LDAP connection failed with error 'Strong(er) authentication required' 

Troubleshooting Tip: FortiGate LDAP troubleshooting and debug logs created by fnbamd

1 reply

New Member
June 10, 2026

Additionally, GPO policies can also override what's discussed in the KB. Therefore, you need to check HKLM\SYSTEM\CurrentControlSet\Services\NTDS\Parameters\ldapserverintegrity showed a value of 1
Although the registry key HKLM\SYSTEM\CurrentControlSet\Services\NTDS\Parameters\ldapserverintegrity showed a value of 1, in my case the DC was still rejecting connections because Windows Server 2025 introduces a second policy called Domain controller: LDAP server signing requirements Enforcement that overrides the default behavior.
On the DC, gpmc.msc was opened and the Default Domain Controllers Policy was located. Inside the GPO editor, the following path was followed: Computer Configuration -> Windows Settings -> Security Settings -> Local Policies -> Security Options. Two policies were modified: Domain controller: LDAP server signing requirements was set to None, and Domain controller: LDAP server signing requirements Enforcement was set to Disabled.
The command gpupdate /force was then executed to apply the changes immediately.

Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!