



Technical Tip: IPv6 Manual Configuration of a Link-Local Address
Description
This article describes how to manually configure an IPv6 link-local address.
Scope
FortiGate and FortiOS.
Solution
By default, FortiOS uses the EUI-64 method to assign link-local addresses to its IPv6 enabled interfaces:
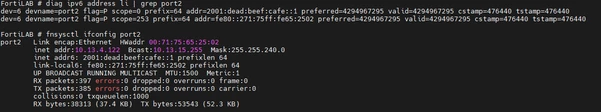
This address is used for on-link communication and for traffic generated by the device, such as Neighbor Discovery Protocol and Dynamic Routing Protocol updates.
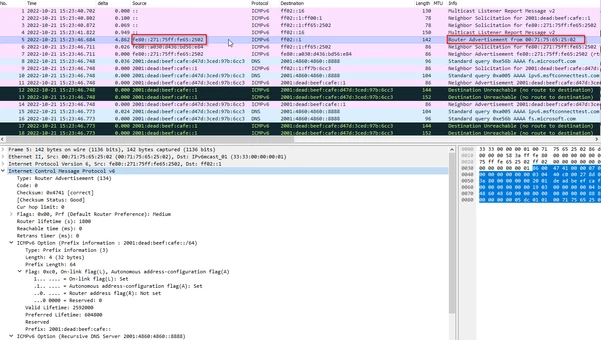
The FortiGate in the above example is configured to send on-link Router Advertisements, including ICMPv6 Options with Prefix Information, on-link flag, and autonomous address-configuration flag. It's therefore possible to connect a host to this port and use SLAAC for host IPv6 configuration.
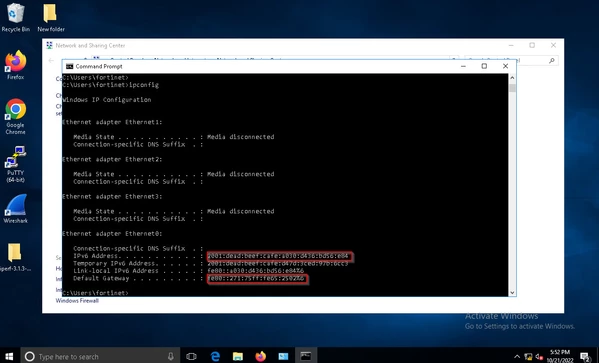
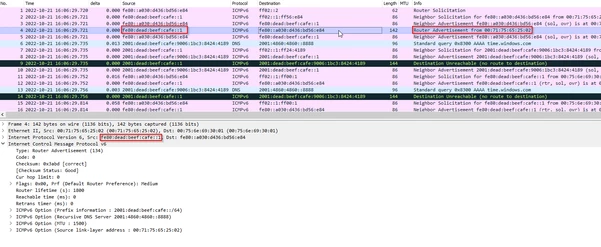
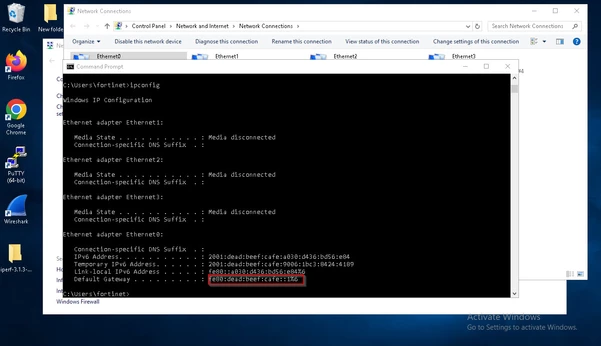
Upon connecting a Windows host to this link and doing a packet capture, it becomes clear that the Advertisements are sent using the EUI-64 generated link-local address of the FortiGate. The Windows host uses SLAAC to generate an IPv6 GUA address based on the /64 prefix and uses the link local address of the FortiGate as a default Gateway:
Manually specifying the link-local address for IPv6-enabled interfaces on FortiOS allows for quick identification of traffic generated by the device. The address can be similar to the GUA for that particular interface.
It is possible to use the same IPv6 link-local address for every enabled IPv6 interface on a single device. Because the link local address has a local scope, it is cannot be routed and it does not pass through the link. Using the same address for every link makes it easier to quickly identify traffic sent by the device within a network.
The example in this article will manually specify the IPv6 link-local address using the config ip6-extra-addr command.
Here, the same GUA is used, and the first hextet is replaced with fe80 (from 2001):
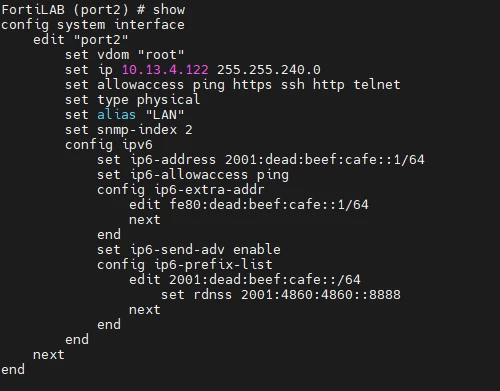
After applying this change, there are two link-local addresses for this interface, but only the one specified will be used:

In pcap and the Windows host:
Starting FortiOS v8.0.0, it is possible to configure ip6-link-local directly on IPv6 interface settings. If ip6-extra-addr is configured, a conflict error will display:
Lab-FGT # config system interface
Lab-FGT (interface) # edit mgmt1
Lab-FGT (mgmt1) # config ipv6
Lab-FGT (ipv6) # config ip6-extra-addr
Lab-FGT (ip6-extra-addr) # edit fe80:beee:ceee:deee::1/64
new entry 'fe80:beee:ceee:deee::1/64' added

Lab-FGT (fe80:beee:ceee:deee::1/64) # next
Lab-FGT (ip6-extra-addr) # end
Lab-FGT (ipv6) # set ip6-link-local fe80::dad/64
Lab-FGT (ipv6) # end

Address conflicts with Extra-address link-local address 'fe80:beee:ceee:deee::1'
attribute set operator error, -255, discard the setting
Command fail. Return code -255

Lab-FGT (mgmt1) #
After deleting the link-local Extra-address is deleted, it will be possible to configure the ip6-link-local directly in the interface:
Lab-FGT (mgmt1) # config ipv6
Lab-FGT (ipv6) # config ip6-extra-addr
Lab-FGT (ip6-extra-addr) # purge
This operation will clear all table!
Do you want to continue? (y/n)y
Lab-FGT (ip6-extra-addr) # end
Lab-FGT (ipv6) # set ip6-link-local fe80::dad/64
Lab-FGT (ipv6) # next
Lab-FGT (ipv6) # end
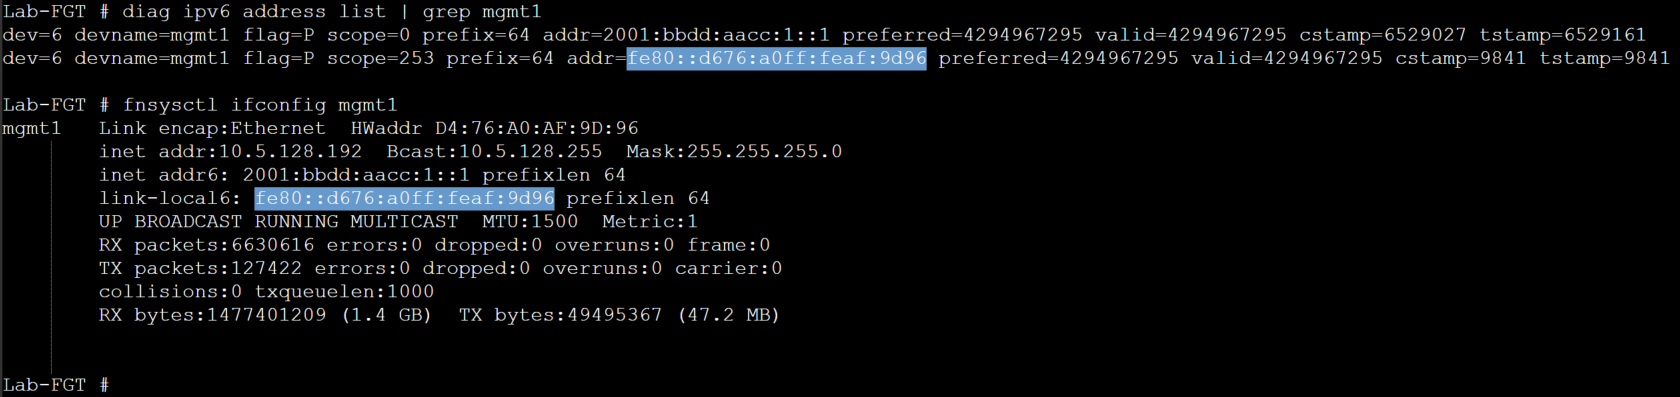
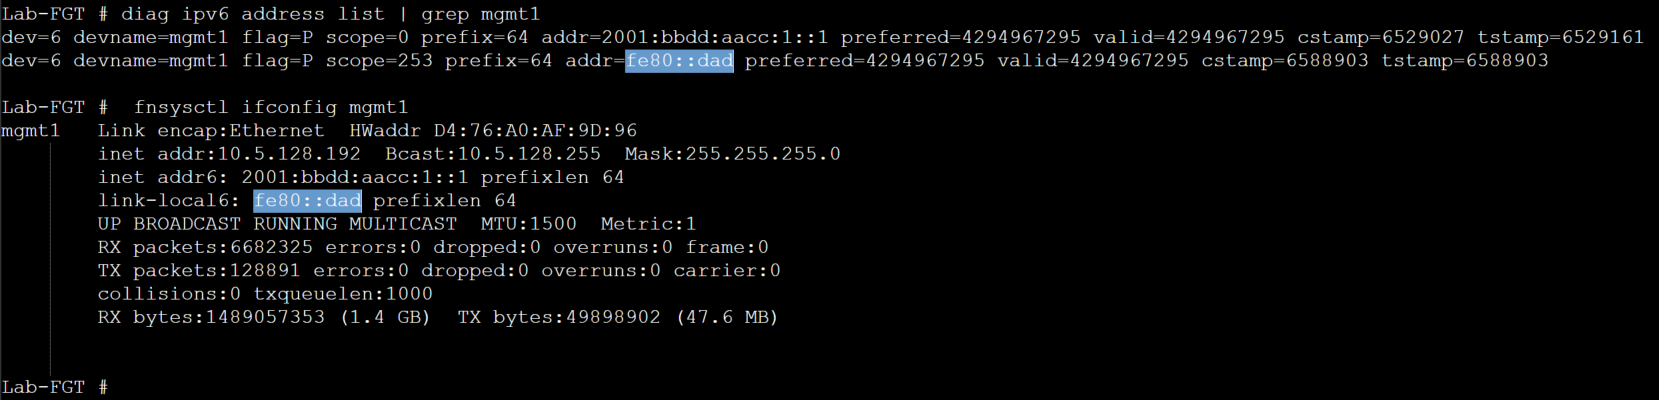
The configured ip6-link-local will replace the default auto-generated IPv6 link-local address:
Before:
After:
Note:
The link-local address used in this example is for demonstration purposes only and does not follow the standard defined in RFC 4291 section 2.5.6, where the first 10 bits are 1111111010, followed by 54 zero bits, so that the first 64 bits are always FE80. Not following the RFC standard may lead to unexpected results with some Operating Systems.
