Staff
December 16, 2025

Technical Tip: IPsec tunnels not connecting after upgrade to v7.6.5 or above

  • December 16, 2025
  • 0 replies
  • 7034 views
Description This article describes issues with IPsec tunnels after upgrading to v7.6.5 or above from any of the older versions.
Scope FortiOS v7.6.5 or above.
Solution

After upgrading to version 7.6.5 or above from any of the older versions, users with IPsec tunnels may experience issues with establishing these tunnels.

Before the upgrade, everything was running smoothly, and after the upgrade to v7.6.5 or above, the tunnels are completely down and will not come up.


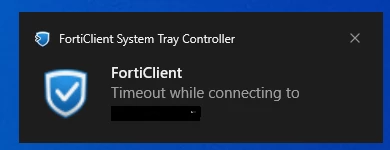
In FortiClient, it will be showing below error while connecting:


timeout.png


When running the IKE debug on one of the impacted tunnels, and if the following error message is seen:


2025-12-15 17:11:09.447240 ike V=root: Negotiate ISAKMP SA Error:
2025-12-15 17:11:09.447285 ike V=root:0:XXXXXXXXXXXXX/0000000000000000:142: no SA proposal chosen


If the protocol used is IKEv2, the following error message is seen:


ike V=root:0:XXXXXXXXXXXXX/0000000000000000:109: no proposal chosen
ike V=root:XXXXXXXXXXXXX/0000000000000000 Negotiate SA Error: peer SA proposal not match local policy
ike V=root:0:XXXXXXXXXXXXX/0000000000000000:109: no proposal chosen, send error response


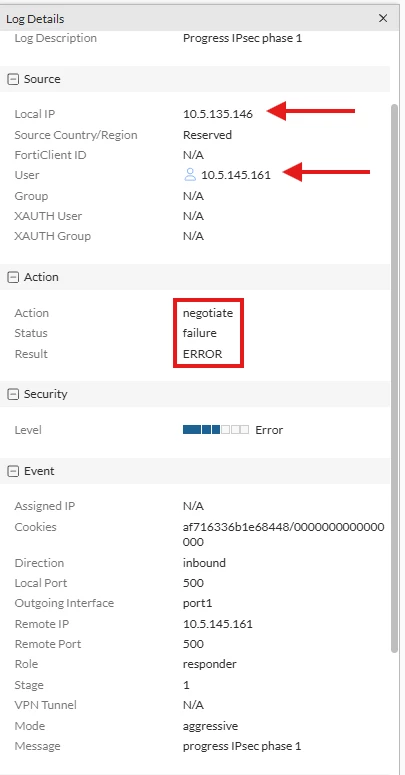
In FortiGate VPN event logs, the following logs will be seen:


Failed.png


date=2026-02-25 time=17:06:22 eventtime=1772019381483532813 tz="+0530" logid="0101037128" type="event" subtype="vpn" level="error" vd="root" logdesc="Progress IPsec phase 1" msg="progress IPsec phase 1" action="negotiate" remip=10.5.145.161 locip=10.5.135.146 remport=500 locport=500 outintf="port1" srccountry="Reserved" cookies="af716336b1e68448/0000000000000000" user="10.5.145.161" group="N/A" useralt="N/A" xauthuser="N/A" xauthgroup="N/A" assignip=N/A vpntunnel="N/A" status="failure" init="remote" mode="aggressive" dir="inbound" stage=1 role="responder" result="ERROR" fctuid="N/A" advpnsc=0


In this scenario, check the DH group values under the Phase 1 and Phase 2 configurations and ensure they match.


In FortiOS v7.6.5 and above, the default DH groups have been set for both Phase 1 and Phase 2 of IPsec VPNs to improve cryptographic strength, where:

  1. Existing tunnels using legacy default DH groups 14 and 5 will be updated to use DH groups 14, 20, and 21 after the upgrade.
  2. Update the legacy default DH groups in both IPsec Phase 1 and Phase 2 configurations from DH groups 14 and 5 to DH groups 20 and 21 when configured from the CLI.


This change can affect tunnels negotiated with peers on older FortiOS versions that are still using legacy defaults (DH group 14 and 5).


After manually setting matching DH groups on both peers, the tunnels should resume connectivity.
For more information, refer to FortiOS v7.6.5's release notes on the changes to default behavior (id 1107163):
Changes in default behavior.


Notes: 

  • The message 'no SA proposal chosen' indicates a mismatch in the IKE proposals during VPN negotiation, often caused by configuration discrepancies.
  • To troubleshoot, verify that both VPN peers have identical Phase 1 and Phase 2 proposal settings, including encryption, hash algorithms, and DH groups.
  • Peer IDs and the preshared key would need to be checked, as sometimes the IKE debug is not accurate regarding the issue.


diagnose vpn ike log filter rem-addr4 <Remote_Peer_IP>
diagnose debug application ike -1
diagnose debug console timestamp enable
diagnose debug enable


To stop the debugging:


diagnose debug disable
diagnose debug reset


  • Review detailed logs on both devices to identify differences in the proposals sent and received.
  • Additionally, capturing the IKE negotiation packets with Wireshark can provide insight into the specific proposals exchanged and help pinpoint where the mismatch occurs, facilitating precise adjustments to align the configurations.


diagnose sniffer packet any "host <Remote_Peer_IP> and port (500 or 4500)" 4 0 l


Press Ctrl + C to stop the sniffer.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!