Solution | It is often necessary to implement a deep inspection of the environment. In the deep inspection profile, there is always a requirement to select a certificate.
Most of the time, the certificate used here is simply a Local certificate, which contains the private and public keys that are often installed for the SSL VPN.
However, this certificate will not be able to be used for the deep inspections. It will not even be possible to see the option to select those certificates.
The reason for this is that this is not the correct type of certificate needed for the deep inspection.
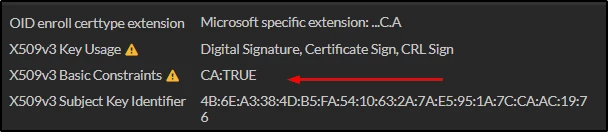
To use a certificate for deep inspection, the certificate must be a CA certificate that is allowed to issue (sign) other certificates. This means the certificate must have the X.509v3 Basic Constraints set to CA: TRUE. In the FortiGate, this can be seen in the following section:
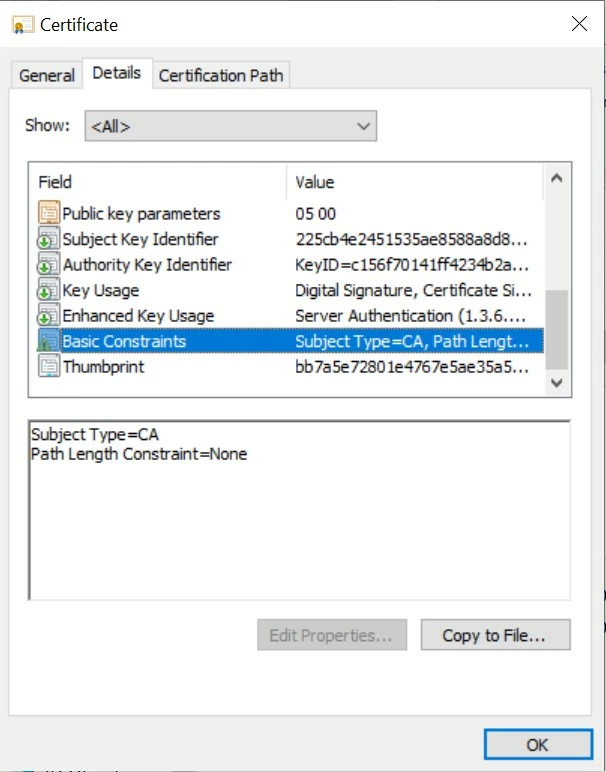
The same info can be found under the details of the certificate by opening the certificate on the PC before uploading it. The subject type under basic constraints should be 'CA', as shown in the following example:
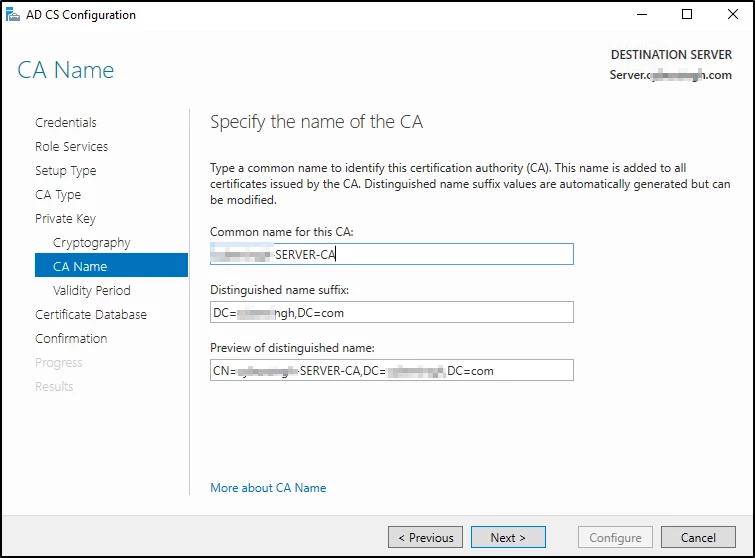
 To not use the Fortinet_CA_SSL certificate, it is possible to install the own Private_CA certificate for the internal network: On the domain controller, it is possible to install the Windows Certificate Authority. Follow the following document: Install the Certification Authority. After the installation, it is possible to create a certificate authority. A certificate authority has been created for this domain.
 Afterwards, it is possible to import this certificate from the domain controller from the Manage Computer Certificate -> Personal Certificate and select the certificate.
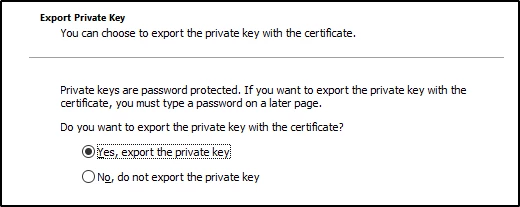
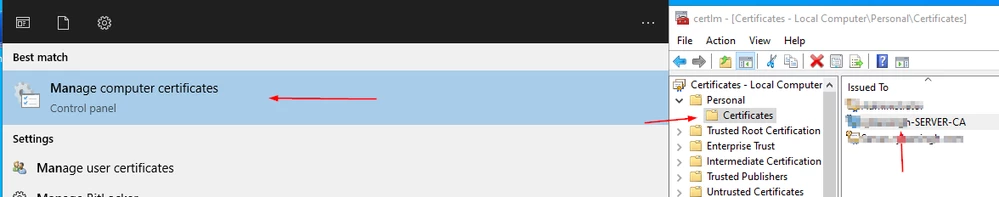 Export this certificate with the private key. It will require a password. Enter the password and export this.
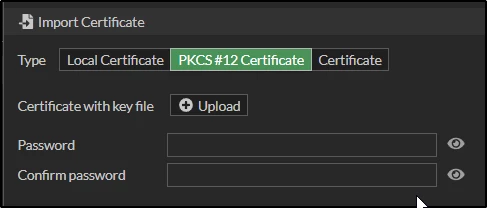
 After this, log in to FortiGate, go to System -> Certificate, and then choose the type 'PKCS#12'. Import the certificate and use the password used for export.
 After the import, the certificate will be visible under the Local CA Certificate.
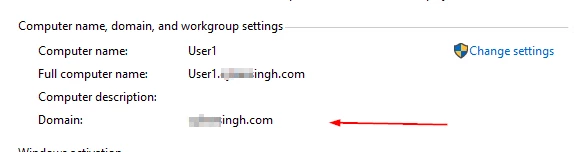
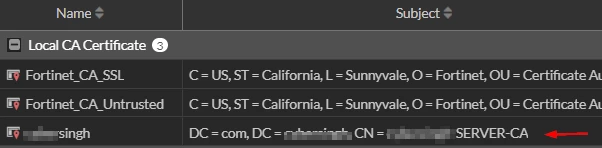 It will then be possible to use this certificate for the Deep Inspection Profile. If the PC is part of the domain, the certificate warning will not be visible. For instance, in this example, the PC is part of the domain.
 When the Fortinet_CA_SSL certificate is used for the deep inspection, the certificate warning is visible because that certificate is issued by FortiGate.
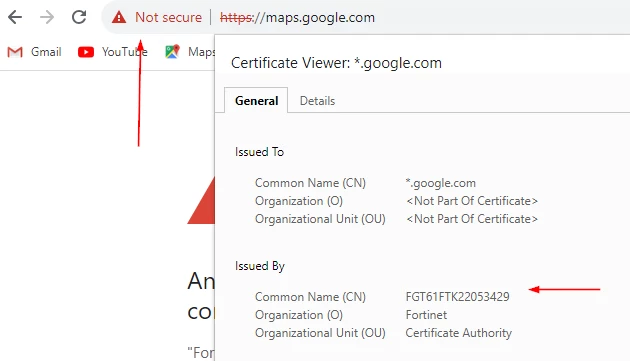 However, when the internal certificate was used for deep inspection, no warning was received because this certificate was signed by the Private CA.
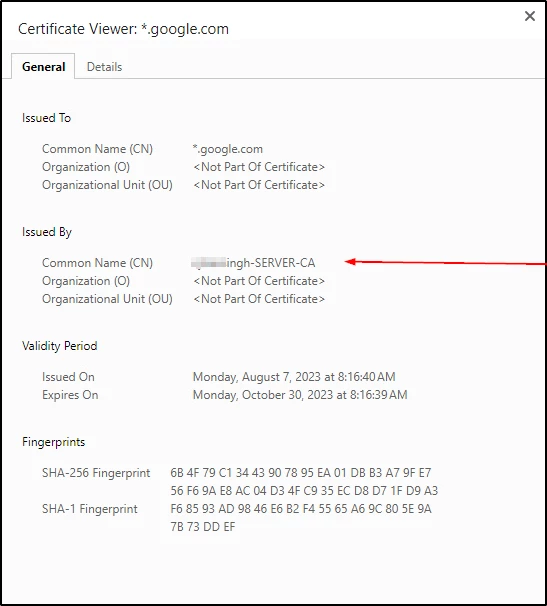 For more information about deep inspection, refer to Deep inspection.
Note: The CA certificate used for SSL Deep Inspection must be issued by a private/internal CA and trusted by all machines within the network. Public CAs are not suitable, as they will not issue certificates for domains outside their ownership. Make sure to apply UTM security profiles in the matching policy for the SSL deep inspection to work, and replace the web server certificate with the CA certificate on the end user machine. The FortiGate includes default certificates, such as Fortinet_CA_SSL, which are generated the first time the FortiGate boots up or when the license is installed.
In certain circumstances, these certificates may need to be regenerated, such as when they are approaching their expiration date, if the private key has been compromised, or, in some cases, as a result of an upgrade.
If any issues are experienced, feel free to contact the TAC team.
Related article:
Technical Tip: Creating and installing a private CA certificate for deep inspection using OpenSSL commands |






