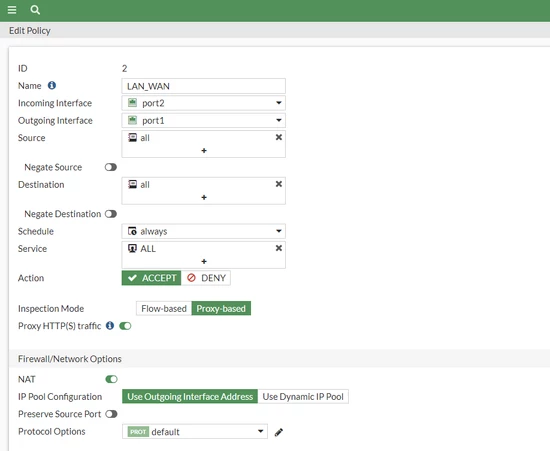

Technical Tip: Inspection mode option is not visible under Firewall Policy
| Description | This article describes that, in FortiGate firewalls operating in NGFW Profile-Based mode, the option to select Flow-based or Proxy-based inspection may not be visible in the GUI under Firewall Policies. |
| Scope | NGFW mode: Profile-Based.
|
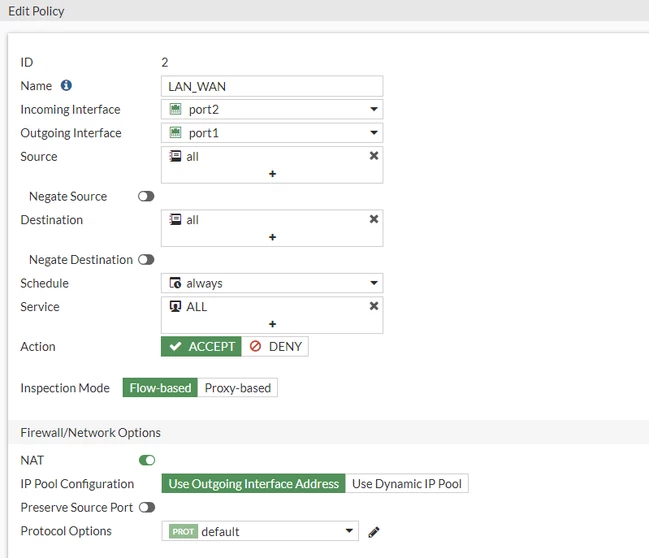
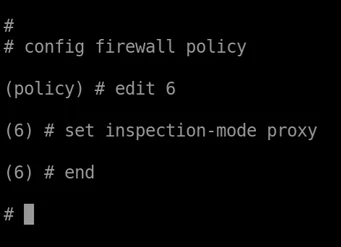
| Solution | It is necessary to change the inspection mode from Flow to Proxy in the policy from the CLI. Once the inspection mode is changed to Proxy, the option to toggle the inspection mode will be available in the GUI.
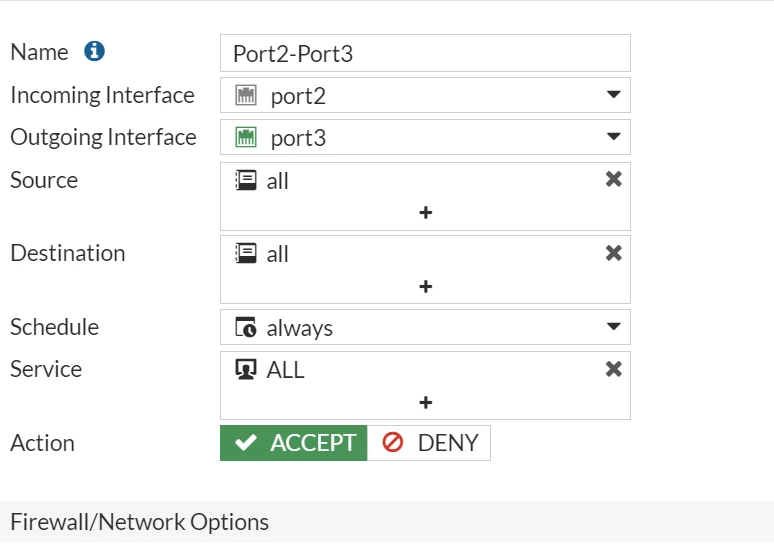
To change the inspection mode from CLI: Step 1:
config system global
end
Step 2:
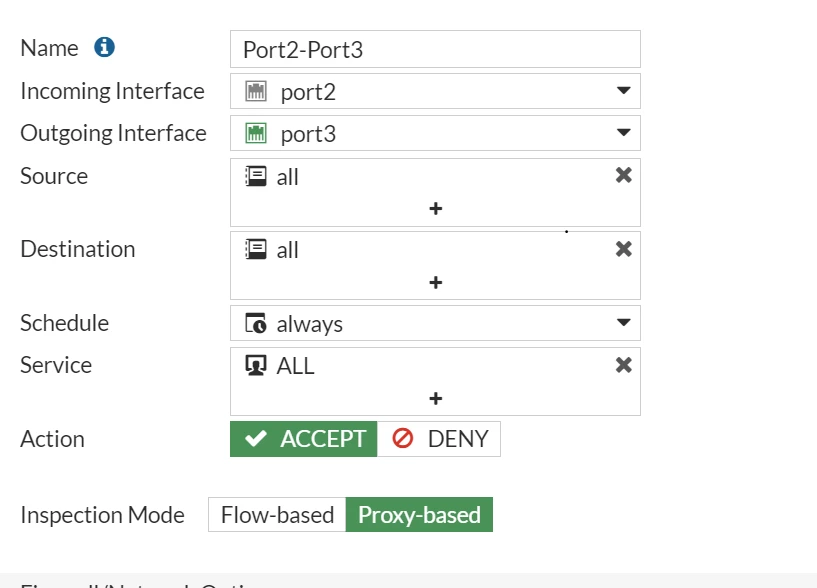
Inspection mode is visible in the GUI now:
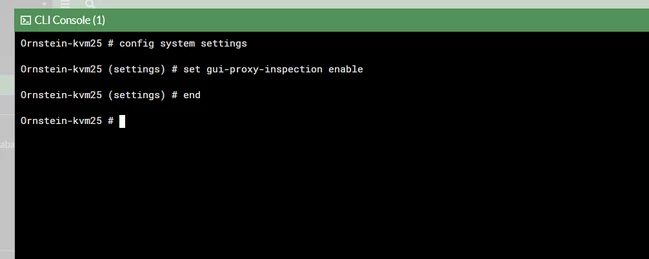
Enable the GUI Inspection option from the CLI:
Inspection mode is visible in the GUI now:
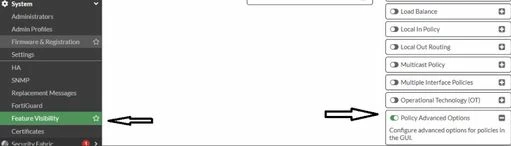
Note: If the inspection mode is still not visible in the GUI, try the following steps:
Now, changing the inspection mode is available in the GUI:
Note: Starting from FortiGate v7.4.4, Proxy-related features are not supported in FortiGate models with 2GB RAM or less. Refer to this document for more information: 2 GB RAM FortiGate models no longer support FortiOS proxy-related features. |