



Technical Tip: Information about 'Count' field in anomaly log
Description
This article describes the anomaly logs and count field in the logs.
Scope
FortiGate.
Solution
In the below dos policy setting 'icmp_flood' DoS attack threshold is set to 2 ICMP packet for testing.
If FortiGate receives more than 2 ICMP packets per second on the port1 interface, it is going to drop any packet after the 2nd ICMP packet.
config firewall DoS-policy
edit 1
set name "test"
set interface "port1"
set srcaddr "all"
set dstaddr "all"
set service "ALL"
config anomaly
edit "icmp_flood"
set status enable
set log enable <-
set action block
set threshold 2 <-
next
end
next
end
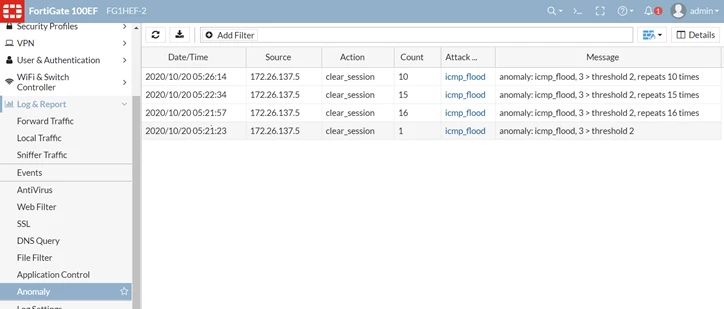
At 2020/10/20 05:21:23, the DoS policy blocked the traffic and so the count shows as 1. This means FortiGate has blocked the ICMP traffic from srcip=172.26.137.5 to dstip=10.5.20.125 once, which is represented by the count value.
date=2020-10-20 time=05:21:23 eventtype="anomaly" level="alert" vd="root" srcip=172.26.137.5 dstip=10.5.20.125 srcintf="port1"
srcintfrole="undefined" sessionid=0 action="clear_session" proto=1 service="PING" count=1 attack="icmp_flood" policyid=1
policytype="DoS-policy" ref="http://www.fortinet.com/ids/VID16777316" msg="anomaly: icmp_flood, 3 > threshold 2" crscore=50 craction=4096 crlevel="critical"
Since this is a continued attack on the FortiGate IP: when the next DoS-policy log is generated (@date=2020-10-20 time=05:21:57), the total number of times FortiGate blocked the ICMP traffic from srcip=172.26.137.5 to dstip=10.5.20.125 is 16 times, which is represented by the count value.
date=2020-10-20 time=05:21:57 eventtype="anomaly" level="alert" vd="root" srcip=172.26.137.5 dstip=10.5.20.125 srcintf="port1"
srcintfrole="undefined" sessionid=0 action="clear_session" proto=1 service="PING" count=16 attack="icmp_flood" policyid=1
policytype="DoS-policy" ref="http://www.fortinet.com/ids/VID16777316" msg="anomaly: icmp_flood, 3 > threshold 2, repeats 16 times" crscore=50
Related articles:


