

Technical Tip: Impact of using cloned 'no-inspection' SSL/SSH Profiles on UTM Policies
Description
This article describes FortiGate's behaviour when a cloned version of the default no-inspection SSL/SSH profile is applied to a policy with UTM features enabled.
Scope
FortiGate devices with UTM features enabled (e.g., Application Control, Web Filtering, Antivirus, etc.).
Solution
When a cloned version of the default no-inspection profile is applied to a policy with UTM profiles (such as Web Filter, AV, or Application Control), all UTM inspection functions will effectively be bypassed, regardless of UTM being enabled in the policy.
- No warning is displayed when applying the cloned profile.
- This is expected behavior in FortiOS.
- Even though UTM features appear enabled, traffic is not inspected if SSL/SSH inspection is fully disabled.
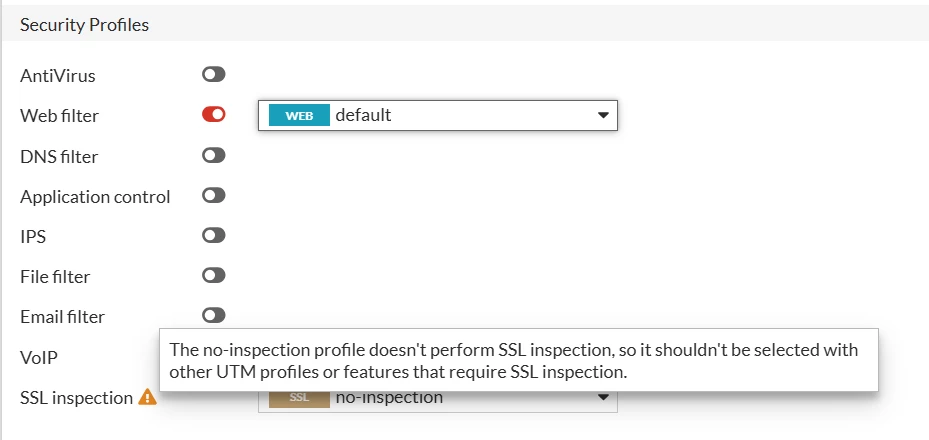
The Warning is shown on the default read-only No-Inspection.
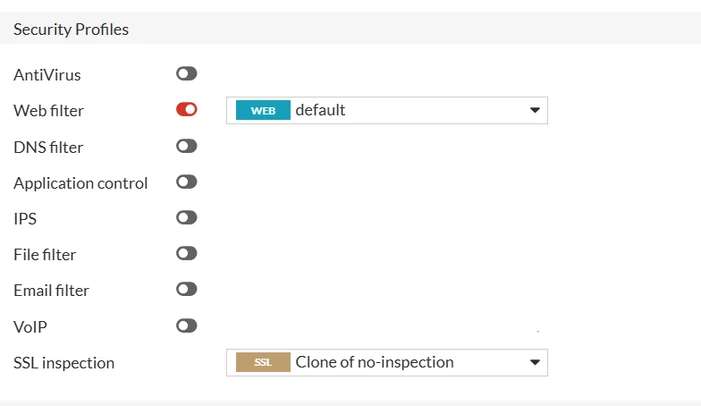
Why this matters:
- Security inspection relies on SSL/SSH profile settings to inspect encrypted traffic.
- If the inspection is set to 'no-inspection' or if all port inspection is disabled, encrypted traffic will pass through without being inspected by UTM features.
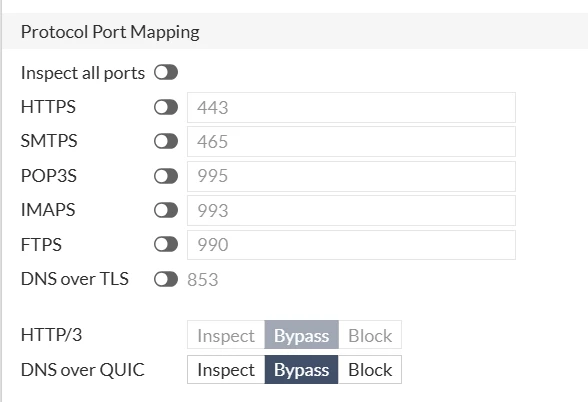
- This can create a false sense of protection where UTM appears active but is functionally ineffective.
Recommendations:
- Avoid using clones of the 'no-inspection' profile on UTM policies unless intentionally bypassing inspection.
- Proactively verify that the SSL/SSH profile assigned to any UTM policy has port inspection enabled where required.
- Review SSL/SSH profiles underSecurity Profiles -> SSL/SSH Inspection.
- Confirm that inspection mode is set to either certificate-inspection or deep-inspection, and that port inspection is not disabled.


