


Technical Tip: IKEv2 Dial-up IPsec tunnel with RADIUS and FortiToken MFA
Description
This article describes how to configure a dial-up IPsec VPN using IKEv2 and Multifactor authentication with FortiToken.
Scope
FortiGate, FortiToken, RADIUS, and Active Directory.
Solution
The XAuth method is only available for IKEv1. The authentication framework supported for IKEv2 is EAP. To select a user group, EAP must be enabled, which requires a RADIUS server. The remote RADIUS server must support EAP-MSCHAPv2 because, for IKEV2, FortiClient will use EAP-MSCHAPv2 by default.
Considering Microsoft NPS is popular, the configuration example below is performed with NPS as a RADIUS server.
Configuration Steps for Microsoft NPS.
Note: This configuration assumes the NPS server role has been installed and registered to Active Directory.
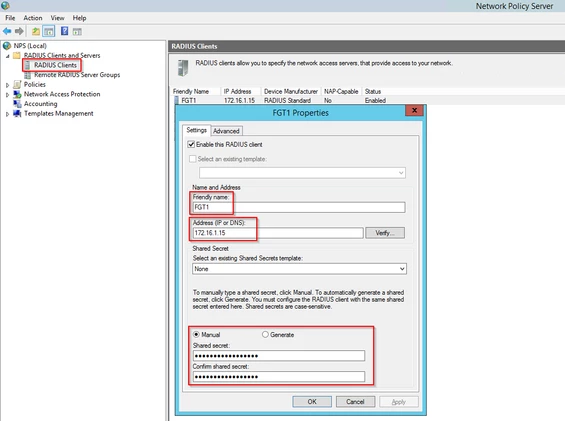
Create a RADIUS Client for the FortiGate IP address and the Shared Secret to be configured in FortiGate:
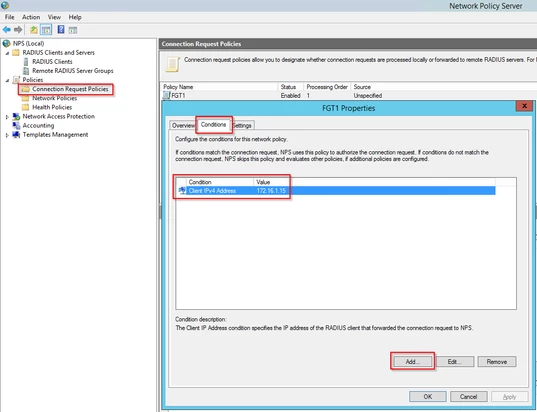
Create a Connection Request Policy with the condition for FortiGate's IP Address and keep other settings as default:
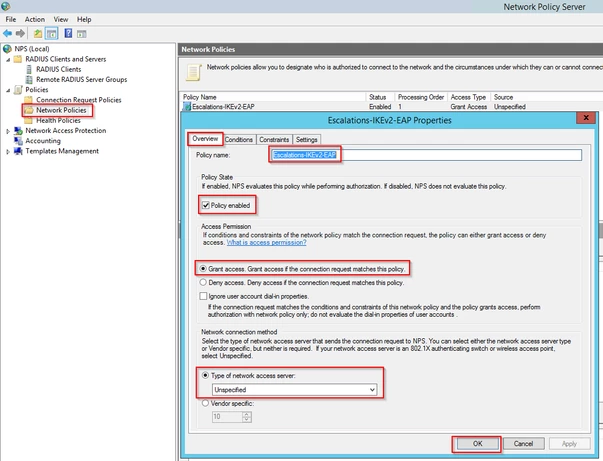
Create a Network Policy. Make sure it is enabled and 'Grant access' is selected.
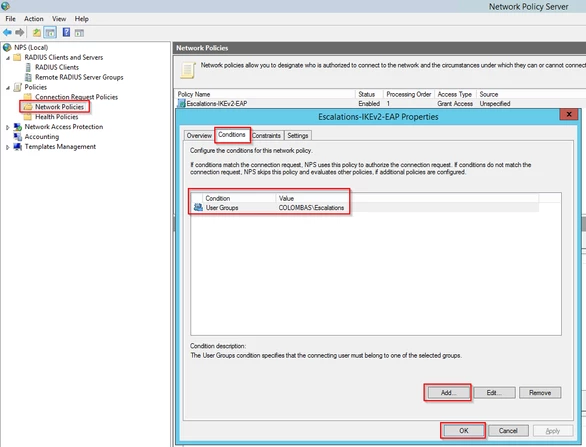
Add a condition to match a specific Active Directory group:
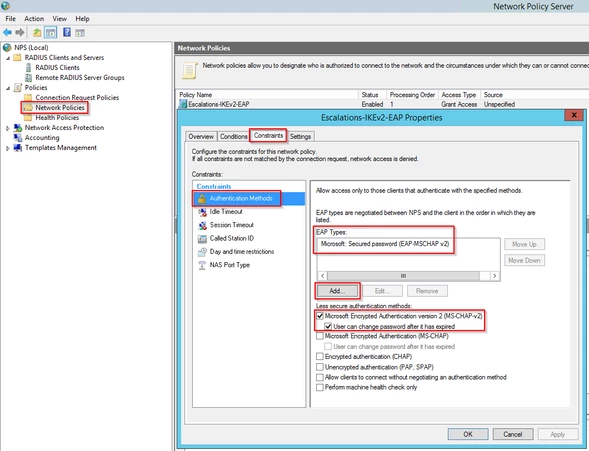
Configure the constraints tab as below. Make sure MSCHAPv2 is also selected for FortiToken to work, and add 'Microsoft: Secured password (EAP-MSCHAP v2)'.
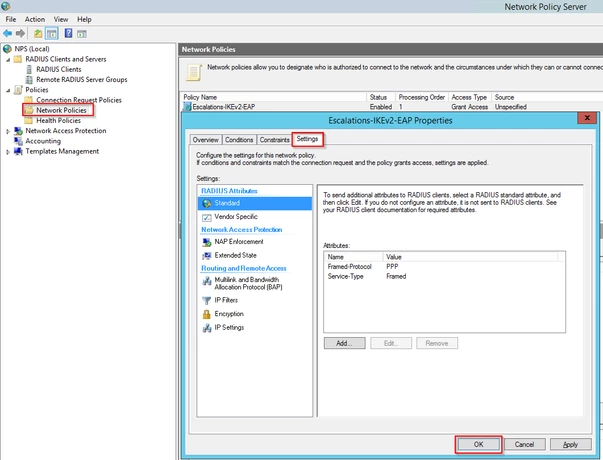
Keep the 'Settings' tab with default options, and select 'OK':
Configuration steps for FortiGate:
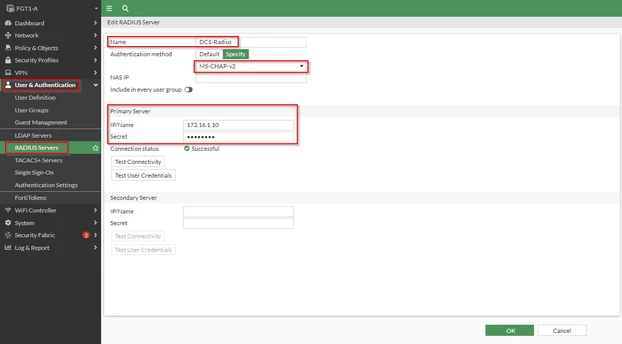
Create a RADIUS server entry if there is not one already. This is the IP address of the NPS:
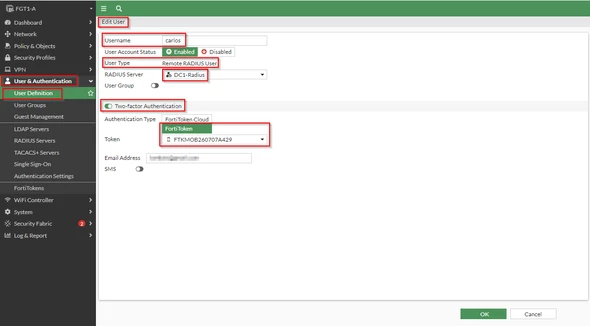
Create a remote RADIUS user or modify the existing one as below:
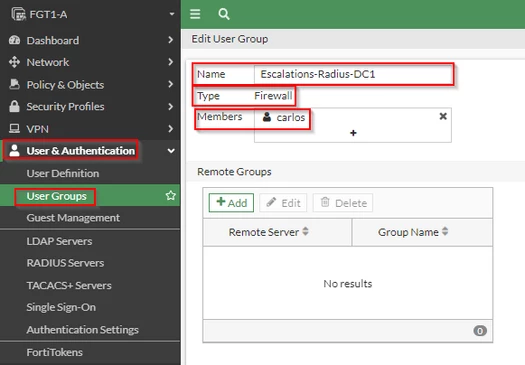
Create or modify a firewall group and add the user to it:
Create the dial-up IPsec tunnel as shown below. This can be done from the 'VPN Creation Wizard' to simplify firewall policy and object creation. EAP options must be configured from the CLI.
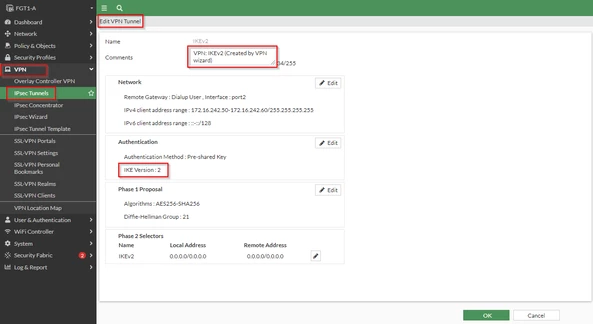
config vpn ipsec phase1-interface
    edit "IKEv2"
        set type dynamic
        set interface "port2"
        set ike-version 2
        set peertype any
        set net-device disable
        set mode-cfg enable
        set ipv4-dns-server1 172.16.1.10
        set proposal aes256-sha256
        set comments "VPN: IKEv2 (Created by VPN wizard)"
        set dhgrp 21
        set eap enable
        set eap-identity send-request
        set authusrgrp "Escalations-Radius-DC1"
        set ipv4-start-ip 172.16.242.50
        set ipv4-end-ip 172.16.242.60
        set ipv4-split-include "LAN1"
        set psksecret ENC
    next
end
config vpn ipsec phase2-interface
edit "IKEv2"
set phase1name "IKEv2"
set proposal aes256-sha256
set dhgrp 21
set comments "VPN: IKEv2 (Created by VPN wizard)"
next
end
Note: EAP configuration can only be done from the CLI.
config vpn ipsec phase1-interface
    edit "IKEv2"
        set eap enable
        set eap-identity send-request
        set authusrgrp "Escalations-Radius-DC1"
    next
end
Troubleshooting.
The following debugs are useful when troubleshooting issues with the configuration above.
CLI 1:
diagnose sniffer packet any “ port <Radius port> and host <Radius-Server-IP>” 6 0 l
CLI 2:
diagnose debug reset
diagnose debug console timestamp enable
diagnose debug application ike -1
diagnose debug application fnbamd -1
diagnose debug application eap_proxy -1
diagnose debug enable
The stop debug:
diagnose debug disable
diagnose debug reset
FortiOS 8.0.1 and above enhances tunnel-down logging by providing clearer, more detailed log information to help administrators identify and troubleshoot IPsec tunnel failures faster. Refer to the following document for detailed information: Logging enhancements for tunnel down.
Third-party MFA:
If the MFA solution is provided by the remote RADIUS server, a longer RADIUS timeout should be set to allow the user sufficient time to complete MFA.
config system global
    set remoteauthtimeout <seconds>
end
config user radius
edit <server name>
set timeout <seconds>
next
end
When two-factor authentication is used for a dial-up tunnel, extending the IPsec negotiation timeout beyond the default 30 seconds may be necessary. This adjustment can prevent connection failures if additional time is required to enter the one-time password (OTP).
For 'set negotiate-timeout', enter an integer value from <1> to <300> <-- Default = <30>.
config vpn ipsec phase1-interface
    edit Dialup_IKEv2
        set negotiate-timeout 50
end
Refer to this article: Technical Tip: IKEv2 dial-up IPsec tunnel with RADIUS server authentication and FortiClient.
Considering DUO is widely used as a remote authentication and MFA solution, keep in mind the limitations highlighted in: Does the Duo Authentication Proxy support MS-CHAPv2 or EAP-MSCHAPv2?.
Notes:
FortiToken push notification over dial-up is supported starting with the following minimum versions:
FortiOS v7.2.8, v7.4.4, v7.6.0 (recommended FortiOS v7.4.8, v7.6.5 to allow manual code entry as a backup if push fails)
FortiAuthenticator v6.5.6, v6.6.1, v8.0.0. (recommended v6.6.4, v8.0.0.)
v7.2.4 and above for Windows.
v7.2.5 and above for MAC.
v7.2.5 and above for Linux.
See this article: Technical Tip: Required firmware/software versions for using FortiToken Mobile or OTP MFA with FortiGate IKEv2 dial-up IPsec.
If FortiGate must authenticate users against an LDAP server rather than a RADIUS server, EAP-TTLS and supported versions must be used, see Technical Tip: Multi-Factor Authentication support for Windows FortiClient with LDAP (EAP-TTLS).
An IPsec dial-up connection with an IOS device will fail to connect if using RADIUS and FortiToken MFA, as it will not receive the token push. As a workaround, include the token in the password field while connecting:
Password: p@ssw0rd.
Token Code: 345678.
The user will enter p@ssw0rd345678 when prompted for the password.
Related documents:


