



Technical Tip: How to verify the block ICMP timestamp on FortiGate interface
Description | This article describes how to usethe built-in sniffer packet tool to make sure the block ICMP timestamp is effective on the FortiGate Interface. |
Scope | FortiGate. |
Solution | By default, FortiGate will respond to the ICMP Timestamp reply if the ICMP Timestamp is received. The images below demonstrate the Nmap ICMP Timestamp sent to FortiGate's Interface and found 1 host up. 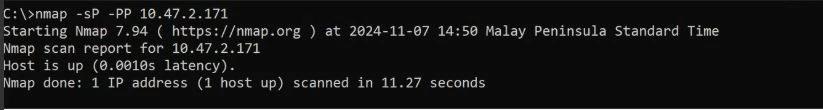
The FortiGate built-in sniffer packet results show the ICMP Timestamp request packet comes in, and FortiGate returns the ICMP Timestamp reply.

Once the Block ICMP Timestamps. The built-in sniffer packet result shows FortiGate will stop responding to ICMP Timestamp reply.
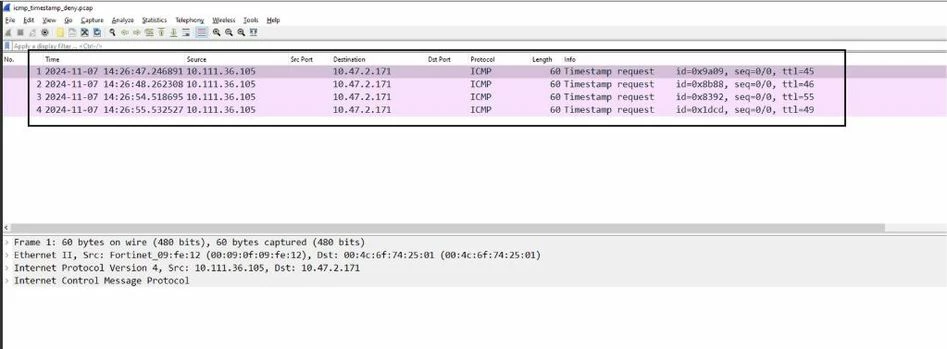
Once Block ICMP Timestamps is enabled, the FortiGate drops incoming ICMP Timestamp requests instead of processing them. Therefore, it does not generate an ICMP Timestamp Reply. This prevents remote devices from obtaining the FortiGate’s system-time information and reduces potential device fingerprinting/information disclosure. |

