



Technical Tip: How to verify that traffic shaping is being applied for traffic
Description
This article describes how to verify if the traffic shaping is being applied for specific traffic or not, using various options.
Scope
FortiGate.
Solution
The following steps can be followed to verify if the traffic shaping is working as expected:
Option 1:
Check if the drop counter is being increased on the shaper that has been configured:
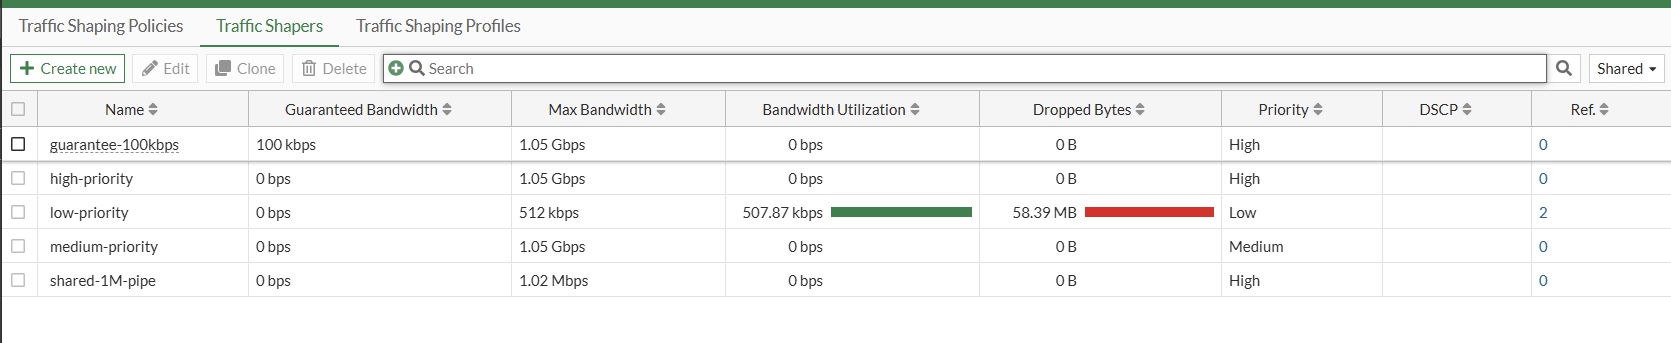
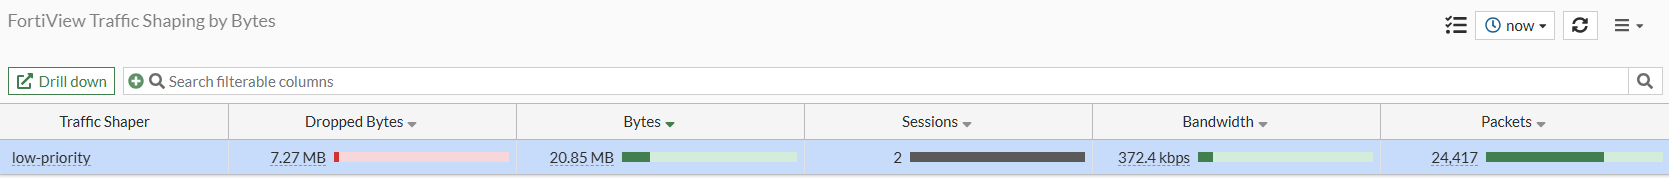
Option 2: Check FortiView Traffic Shaping dashboard:
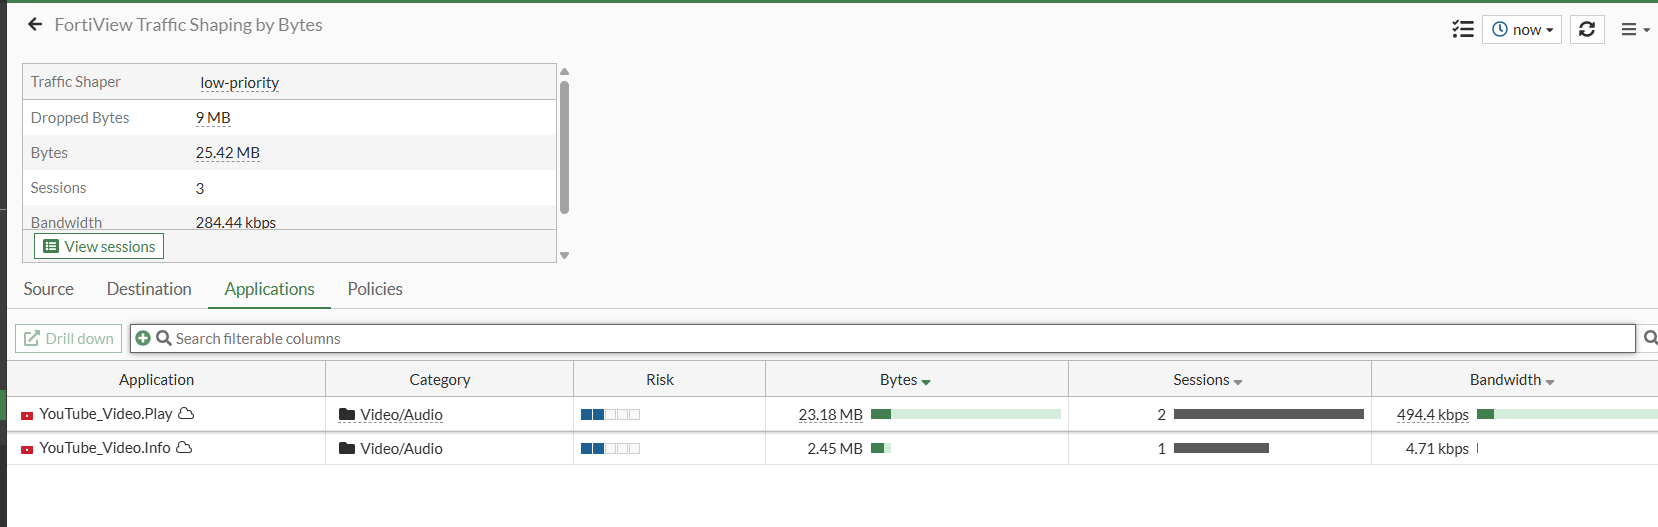
To know more about the source, destination and applications of a particular shaper, double-click on any of them:
Option 3:
Verify from the session details:
Filter the session using the source and destination using the commands below:
diagnose sys session filter src <SRC IP>
diagnose sys session filter dst <DST IP>
diagnose sys session list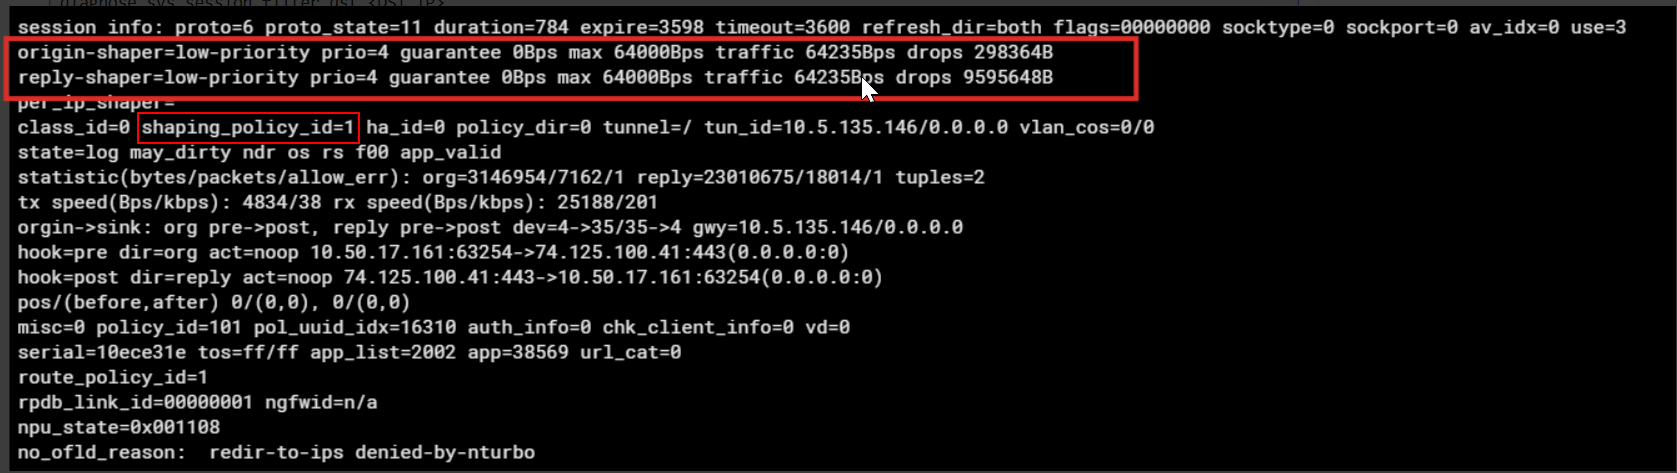
The session details show the shapers that have been applied for this session. The 'shaping_policy_id' can also be referenced to determine which specific traffic shaping policy the traffic is matching.
To check information about Shared and per-IP traffic shapers:
For shared policy:
Execute the following command to check information about shared policy traffic, such as max, guaranteed, and current bandwidth, including priorities and packets, and bytes dropped.
diagnose firewall shaper traffic-shaper list
For per-IP policy:
Run the equivalent command for per-IP shared policy:
diagnose firewall shaper per-ip-shaper list
This provides information about shared policy traffic and max, guaranteed, and current bandwidth, including priorities and packet and byte dropped.
Additionally, to see traffic shaper statistics (combined) from CLI:
diagnose firewall shaper traffic-shaper stats
