



Technical Tip: How to verify Security Events logs on the FortiGate GUI
Description
This article describes how to generate test logs and verify the Security Events logs under Log & Report -> Security Events section of the FortiGate GUI, after enabling 'Security Events' in the Firewall Policy Logging Options.
Scope
FortiGate.
Solution
- Open a Putty session on your FortiGate and run the command #diagnose log test. The following logs will be generated:
generating a system event message with level - warning
generating an infected virus message with level - warning
generating a blocked virus message with level - warning
generating a URL block message with level - warning
generating a DLP message with level - warning
generating an IPS log message
generating an application control IM message with level - information
generating an IPv6 application control IM message with level - information
generating deep application control logs with level - information
generating an antispam message with level - notification
generating an allowed traffic message with level - notice
generating a multicast traffic message with level - notice
generating a ipv6 traffic message with level - notice
generating a wanopt traffic log message with level - notification
generating a HA event message with level - warning
generating a VOIP event message with level - information
generating a DNS event message with level - information
generating authentication event messages
generating a Forticlient message with level - information
generating a URL block message with level - warning
-
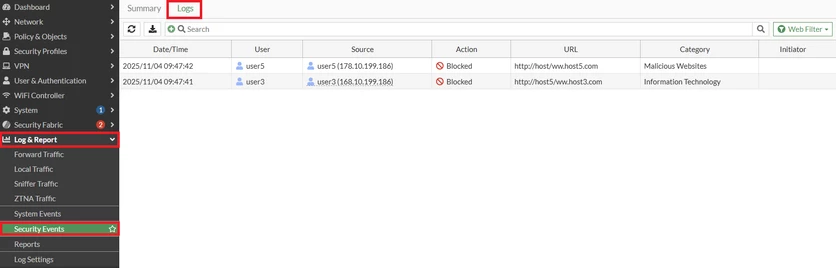
Verify the Security Events under Log & Report -> Security Events -> Logs:
Related articles:

