FortiGate DNS server configuration.
config system dns
    set primary 96.45.45.45
    set secondary 96.45.46.46
end
Run the following commands on the FortiGate:
diagnose debug application dnsproxy -1
diagnose debug console timestamp enable
diagnose debug enable
After enabling the debug processes, initiate a DNS lookup from the FortiGate. For example:
execute ping example.com
Debug Output:
FortiGate sends a query to the first available DNS server.
Note the following annotated log output:
2026-09-07 11:49:15 [worker 0] dns_find_best_server()-602: found server: 96.45.45.45 (vfid=0 vrf=0)     <- DNS server the FortiGate selected

2026-09-07 11:49:15 [worker 0] dns_udp_forward_request()-1078: vdom=root req_type=1 domain=example.com oif=0

2026-09-07 11:49:15 [worker 0] dns_udp_forward_request()-1206: Send 29B to
[96.45.45.45]:53 via fd=20 request:1

<- FortiGate is forwarding a DNS query for example.com to FortiGuard server.

2026-09-07 11:49:15 [worker 0] __udp_receive_response()-3533: vd-0: len=212, addr=96.45.45.45:53, rating=0

<- FortiGate received a response

2026-09-07 11:49:15 [worker 0] dns_query_handle_response()-2871: vfid=0 real_vfid=0 vrf=0 id=0x006b domain=example.com pktlen=212
2026-09-07 11:49:15 [worker 0] dns_query_save_response()-2795: domain=example.com pktlen=212
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-211: QR: example.com
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-219: Offset of 1st RR: 29 Number of RR's: 10
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 300, RR type: 1 <- Type 1 represents an A record

2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 300, RR type: 1 <-Type 1 represents an A record

2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 172177, RR type: 2
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 172177, RR type: 2
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 85091, RR type: 1
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 85091, RR type: 1
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 85091, RR type: 1
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 84850, RR type: 1
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 84850, RR type: 1
2026-09-07 11:49:15 [worker 0] dns_set_min_ttl()-239: RR TTL: 84850, RR type: 1
2026-09-07 11:49:15 [worker 0] dns_cache_response()-360: Min ttl = 300
2026-09-07 11:49:15 [worker 0] dns_secure_forward_response()-1681: category=255 profile=none
hostname_entry_insert()-292: af=2 domain=example.com
2026-09-07 11:49:15 [worker 0] hostname_entry_insert()-292: af=2 domain=example.com
2026-09-07 11:49:15 [worker 0] dns_send_response()-1645: domain=example.com reslen=212
2026-09-07 11:49:15 [worker 0] __dns_udp_forward_response()-1522
2026-09-07 11:49:15 [worker 0] __dns_udp_forward_response()-1534: vd-0 Send 212B via fd=8, family=1
Once the required output has been captured, disable the debug:
diagnose debug disable
DNS Type 1 represents an A record.
DNS Type 2 represents an NS (Name Server) record.
The packet capture below confirms the complete DNS transaction between the FortiGate and the FortiGuard DNS server. The capture shows the DNS query sent by the FortiGate and the corresponding DNS response received from the FortiGuard DNS server. The DNS response contains multiple resource records, including A (Type 1) records and NS (Type 2) records, confirming that the DNS server successfully responded to the query.
To reproduce this packet capture, run the following sniffer command on the FortiGate:
diagnose sniffer packet any 'host 96.45.45.45 and udp port 53' 6 0 l
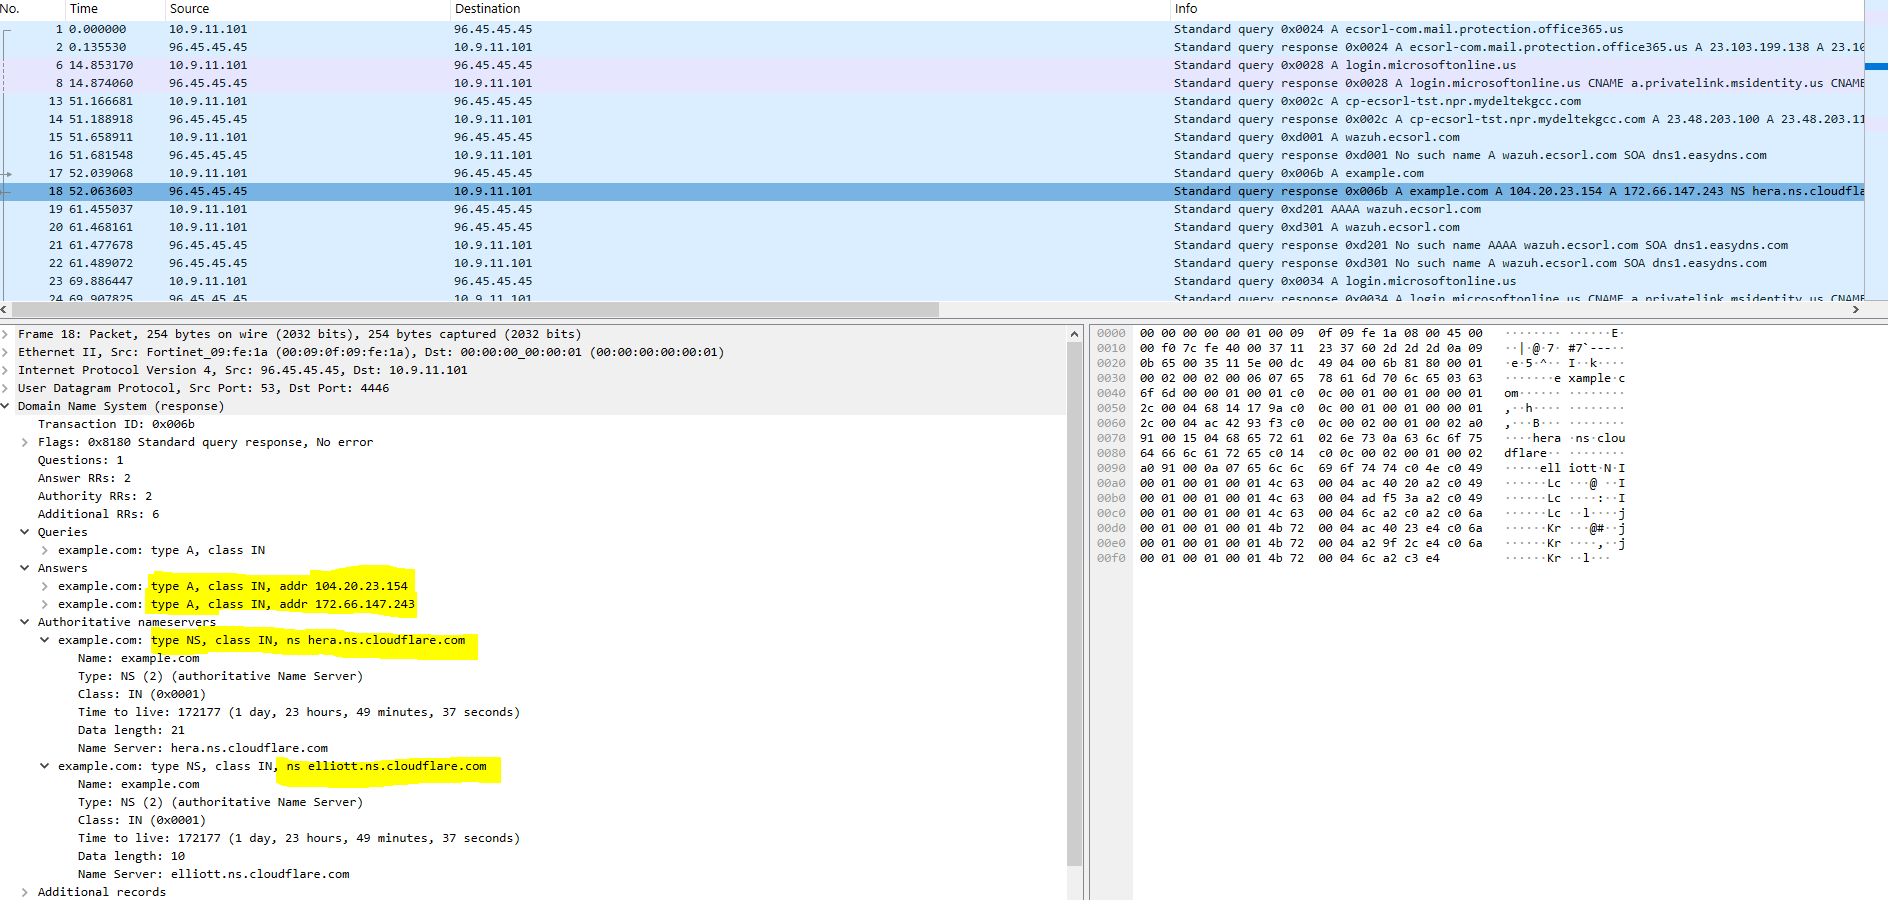
For DoT (DNS over TLS) deployments, replace udp port 53 with tcp port 853 in the sniffer filter.
Note:
A similar output will be displayed in the debug logs, whether the DNS protocol is configured as Cleartext or DoT (DNS over TLS).
Related article:
Technical Tip: FortiGate Troubleshooting DNS commands | 





