
Technical Tip: How to troubleshoot FortiGate Cloud internal error
| Description | This article describes how to solve the issue of FortiGate Cloud internal error on the latest versions. |
| Scope | FortiGate v7.0.12 or above. |
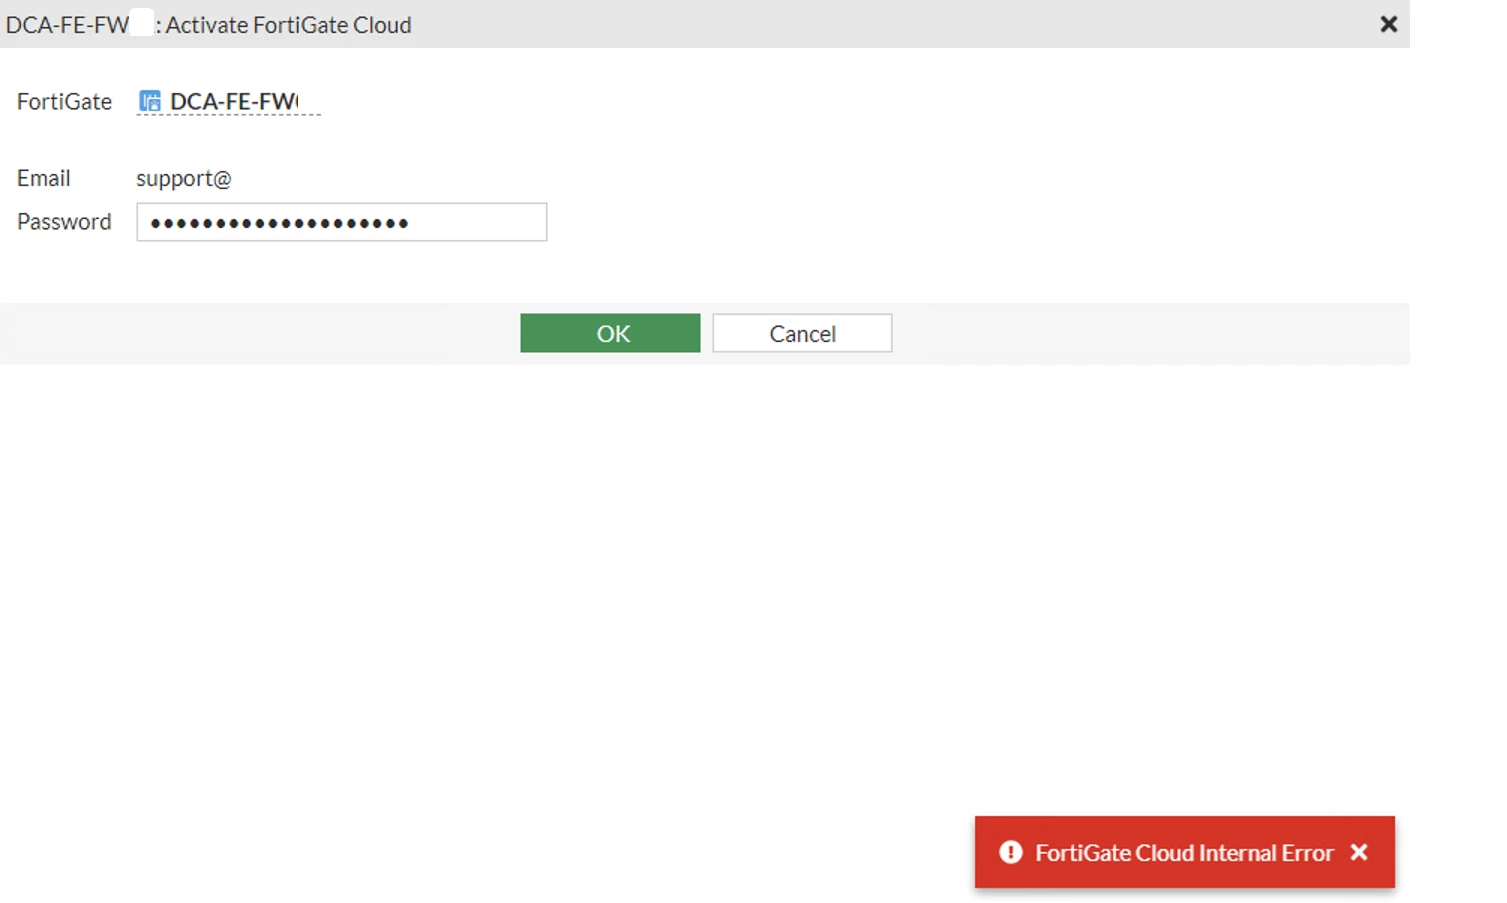
| Solution | If the following error appears in the GUI:
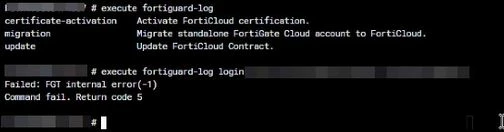
Or the same message is observed in CLI:
execute ping logctrl1.fortinet.com execute ping globallogctrl.fortinet.net execute ping service.fortiguard.net execute ping guard.fortinet.net execute ping securewf.fortiguard.net -----> Used for HTTPS service. execute ping update.fortiguard.net
If they are not reachable, then check DNS reachability on FortiGate and troubleshoot it accordingly: Technical Tip: DNS stops working when using custom DNS.
When deploying units in a high-availability (HA) cluster, ensure that each device is registered individually to the appropriate FortiCloud account. Refer to this article for step-by-step guidance:
config system fortiguard set auto-join-forticloud enable end
config system fortiguard
config system central-management set type fortiguard end
diagnose fdsm contract-controller-update
execute fortiguard-log login <email> <password> <location>
There are three options for domains like GLOBAL/EUROPE/US.
diagnose sys process pidof forticldd ------> To check the process ID of forticldd. diagnose sys kill 11 <forticldd pid> ------> Restart the specific process id. fnsysctl killall forticldd ------> Restart all instances of forticldd.
diagnose test application forticldd 3 Debug zone info:
execute telnet 154.52.10.188 514
diagnose debug disable diagnose debug reset diagnose debug application forticldd -1 diagnose debug enable
The following errors may be seen:
[1060] ssl_connect: SSL_connect failes: error:1409442E:SSL routines:ssl3_read_bytes:tlsv1 alert protocol version
config system global
[105] fds_print_msg: Status:down
diagnose sniffer packet any 'net 208.91.113.0/24 or net 173.243.132.0/24' 6 0 l
The issue can also occur due to a low PMTU of the link over which FortiCloud traffic is routed. In that case, test by trying to adjust the MTU of the external interface to lower values:
config system interface edit <interface_name> set mtu-override enable set mtu <value> next end
Note: The source IP and interface used to initiate the connection to the FortiCloud server are specified under the 'config log fortiguard setting'. It is 'auto' by default, which is similar to the FortiGuard setting.
config log fortiguard setting set source-ip <- IP address of the WAN interface that can reach service.fortiguard.net. set interface-select-method specify <----- Specify the interface selection method to be the same as FortiGuard. set interface <interface> <----- Specify the interface. end
If the issue persists, open a support ticket with Fortinet and attach the Configuration file along with the debug outputs captured above and the output of these commands:
diagnose fdsm account-info diagnose test application forticldd 1 diagnose test application forticldd 2 diagnose test application forticldd 3
Related documents: Technical Tip: FortiGate Cloud Report shows error 'Internal Server Error' Troubleshooting Tip: FortiCloud internal error when activating a FortiCloud account on FortiGate FortiGate Cloud Port and access control information Troubleshooting Tip: FortiCloud connection failure Troubleshooting Tip: Resolve 'Haven't set FortiCloud account id' by adding a FortiGuard service-account ID |