



Technical Tip: How to setup LACP between FortiGate and Juniper Switch
Description
This article describes a glimpse of the configuration of LACP between the FortiGate firewall and Juniper Switch.
Scope
FortiOS.
Solution
The topology setup is as follows:
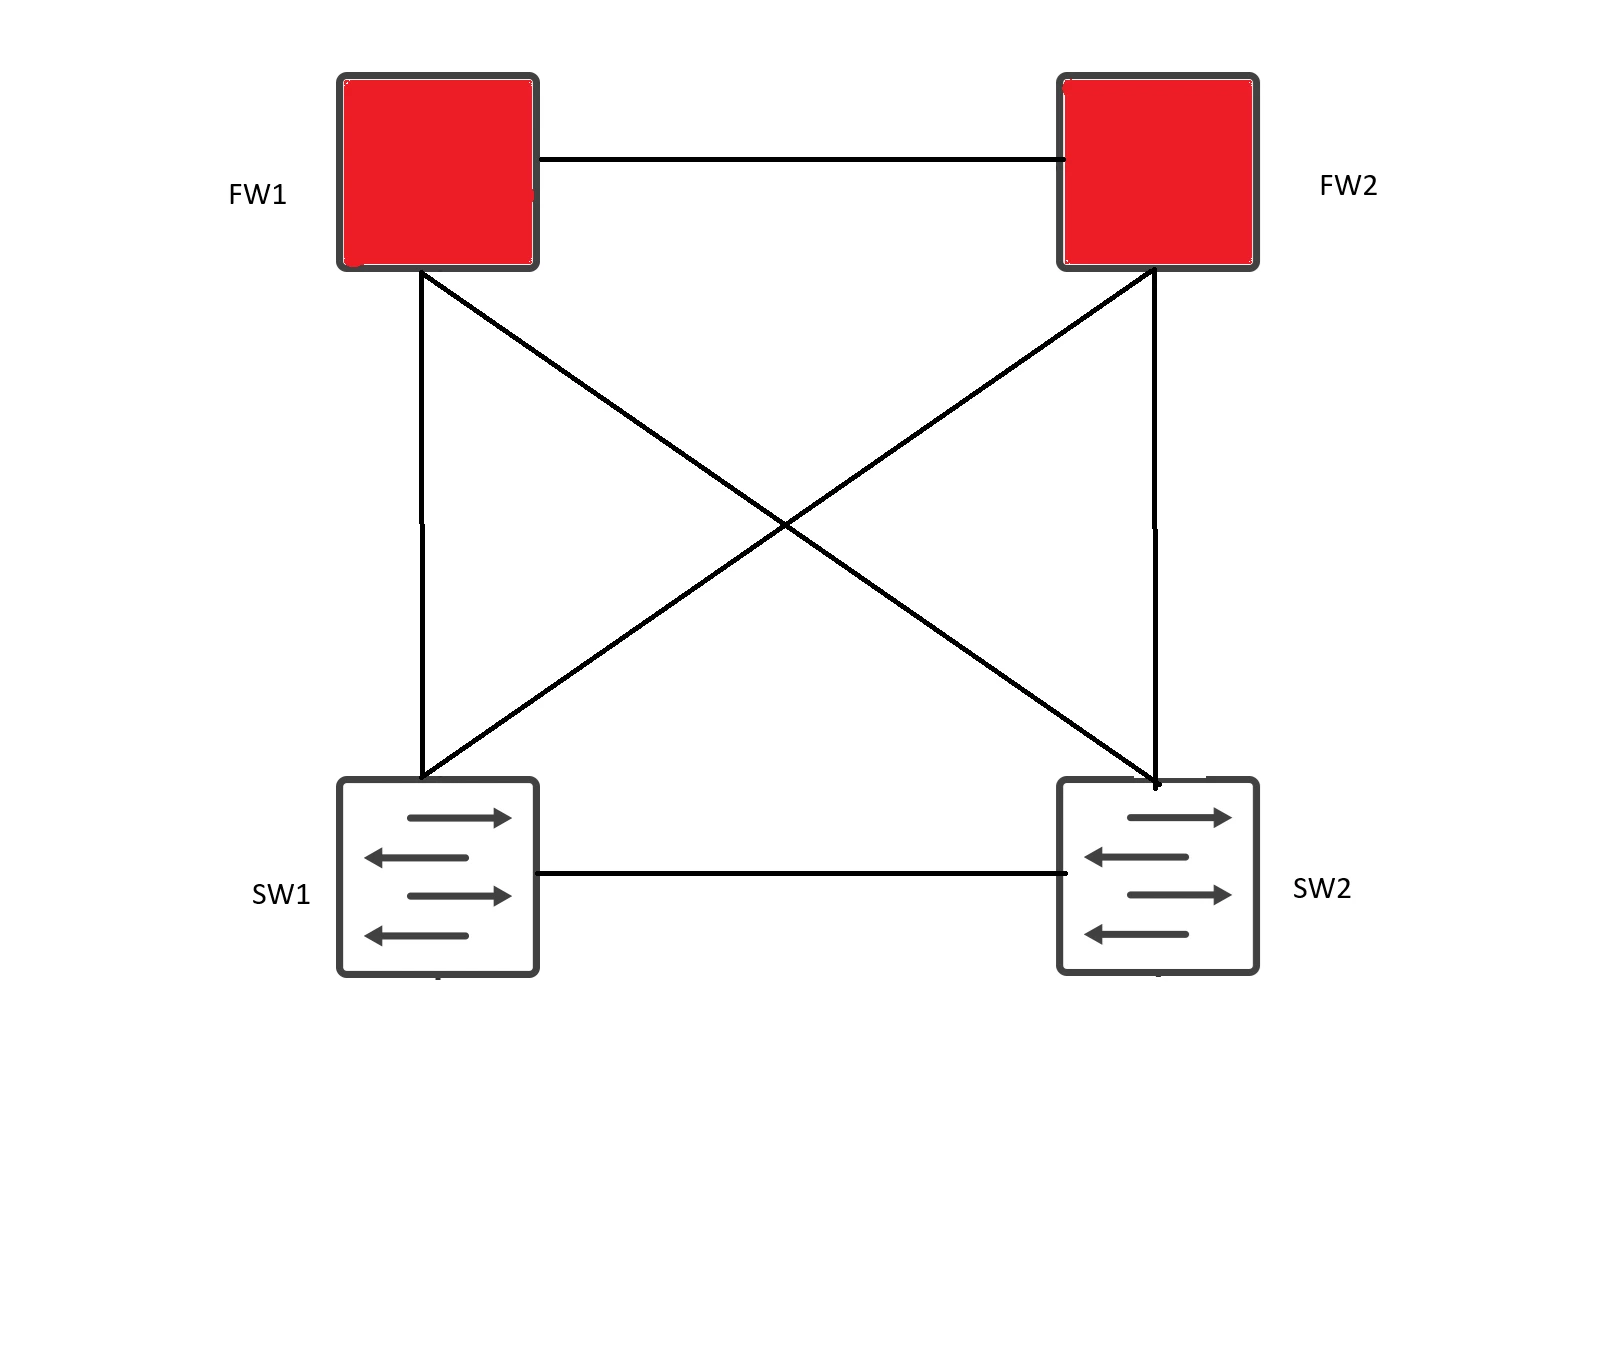
The FortiGate firewall is configured in an Active-Passive setup, and it is connected to a Juniper switch.
LACP configuration on the FortiGate Side:
config system interface
edit "LACP-X3-X4"
set vdom "root"
set type aggregate
set member "x3" "x4" --> Here it is selected X3, X4 port to be part of LAG.
set alias "sw-uplink"
set device-identification enable
set lldp-reception enable
set lldp-transmission enable
set role lan
set snmp-index 12
set lacp-mode active
set lacp-speed fast ---> Change lacp-speed from slow to fast.
next
end
Note: The default lacp-speed on FortiGate is set to slow (every 30 seconds) while the default speed setting on the Juniper side, in most cases, is set to fast. These settings must match on both sides to ensure proper LACP negotiation.
Since the FortiGate is in HA, the same config will get synced with the Slave device.
LACP configuration on the Juniper Side:
- Configure the interfaces for ae0:
set interfaces ge-0/0/6 ether-options 802.3ad ae0
set interfaces ge-0/0/7 ether-options 802.3ad ae0 - Configure the ae0 interface for VLAN tagging:
set interfaces ae0 vlan-tagging - Configure LACP for ae0 and configure periodic transmission of LACP packets:
set interfaces ae0 aggregated-ether-options lacp active periodic fast - Configure ae0 as a trunk port:
set interfaces ae0 unit 0 family ethernet-switching interface-mode trunk - Configure the VLAN:
set vlan vlan1000 vlan-id 1000 - Add the ae0 interface to the VLAN:
set interfaces ae0 unit 0 family ethernet-switching vlan members vlan1000 - If configuring the device is done, commit the configuration:
commit
Verify the LACP status on FortiGate and the Juniper switch:
Juniper Side:
show lacp interfaces ae0
Aggregated interface: ae0
LACP state: Role Exp Def Dist Col Syn Aggr Timeout Activity
ge-0/0/6 Actor No No Yes Yes Yes Yes Fast Active
ge-0/0/6 Partner No No Yes Yes Yes Yes Fast Passive
ge-0/0/7 Actor No No Yes Yes Yes Yes Fast Active
ge-0/0/7 Partner No No Yes Yes Yes Yes Fast Passive
LACP protocol: Receive State Transmit State Mux State
ge-0/0/6 Current Fast periodic Collecting distributing
ge-0/0/7 Current Fast periodic Collecting distributing
Note: The LACP protocol indicates the link is up if it is collecting and distributing packets.
Check detailed LACP information:
show interfaces <aggregate_interface_name> extensive
FortiGate Side:
diagnose netlink aggregate name LACP-X3-X4
status: up
npu: y
flush: n
asic helper: y
oid: 82
ports: 2
link-up-delay: 50ms
min-links: 1
ha: master
distribution algorithm: L4
LACP mode: passive
LACP speed: fast
LACP HA: enable
aggregator ID: 1
slave: x3
index: 0
link status: up
LACP state: established
slave: x4
index: 0
link status: up
LACP state: established
Check LACP configuration:
show system interface <aggregate_interface_name>

