


Technical Tip: How to send traffic out with the specific source IP address
Description
This article describes that in some cases, it is necessary to send out the traffic with the specific source IP address, which is not the wan1 or wan2 IP address at the external interface. Use the IP Pool feature with the firewall policy to achieve this.
Scope
FortiGate.
Solution
For v5.0:
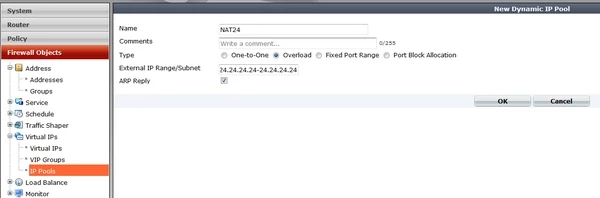
- Using the GUI, go to Firewall Objects -> Virtual IPs -> IP Pools -> Create New and set the parameter values as follows:
Name : NAT24
Type : Overload
External IP Range/Subnet : 24.24.24.24-24.24.24.24
ARP Reply : enable

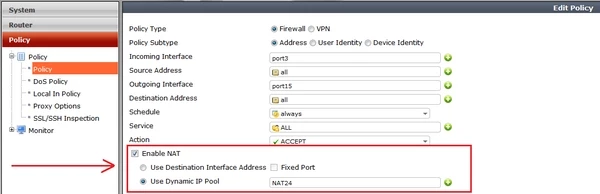
- Create the firewall policy from the source interface to the destination interface as required, and set the IP Pool to Enable NAT. Select the option to 'Use Dynamic IP Pool' and choose the one that was created in the previous step (For example: 'NAT24').
For v7.0, v7.2, v7.4, 7.6:
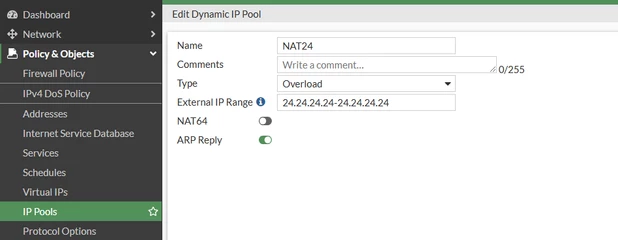
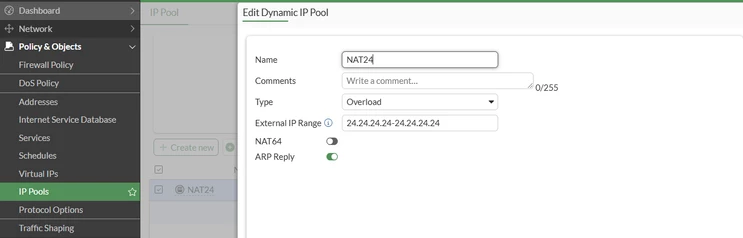
Using the GUI, go to Policy & Objects -> IP Pools -> Create New and set the parameter values as follows:
Name: NAT24.
Type: Overload.
External IP Range/Subnet: 24.24.24.24-24.24.24.24.
ARP Reply: enable.
For v 7.0, v7.2, v7.4 GUI:

From v7.6 GUI:

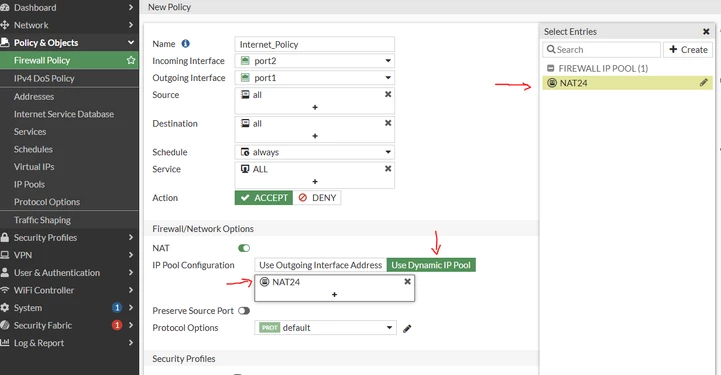
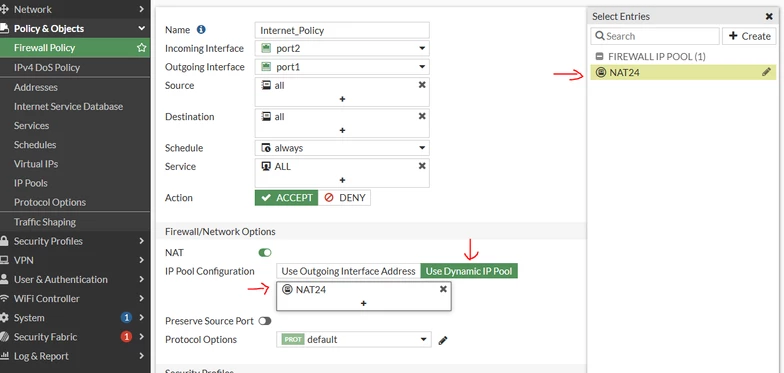
- Create the firewall policy from the source interface to the destination interface as required, and set the IP Pool to Enable NAT. Select the option to 'Use Dynamic IP Pool' and choose the one that was created in the previous step (For example: 'NAT24').
For v7.0, v7.2, v7.4 GUI:
For v7.6 GUI:
Note: There is an IP pool behavior change when 'set arp-reply enable' is configured in the IP Pools from version to version. For more information, refer to this article: Technical Tip: IP pool and virtual IP behavior changes in FortiOS v6.4, v7.0, v7.2, and v7.4.
Related article:
Technical Tip: Mapping VIP outbound connections (Source NAT)


