


Technical Tip: How to send logs to a different syslog server than the one from global settings for a specific VDOM
Description
This article demonstrates how to override global syslog settings so that a specific VDOM can send logs to a different syslog server. This also applies when just one VDOM should send logs to a syslog server.
This article also demonstrates configuring a FortiGate to send logs to a Tftpd64 Syslog Server.
Scope
FortiGate.
Solution
If syslog-override is disabled for a VDOM, that VDOM's logs will be forwarded according to the global syslog configuration. While syslog-override is disabled, the syslog setting under the VDOM -> Log & Report -> Log Settings will be grayed out and show the global syslog configuration, since it is not possible to configure VDOM-specific syslog servers in this case.
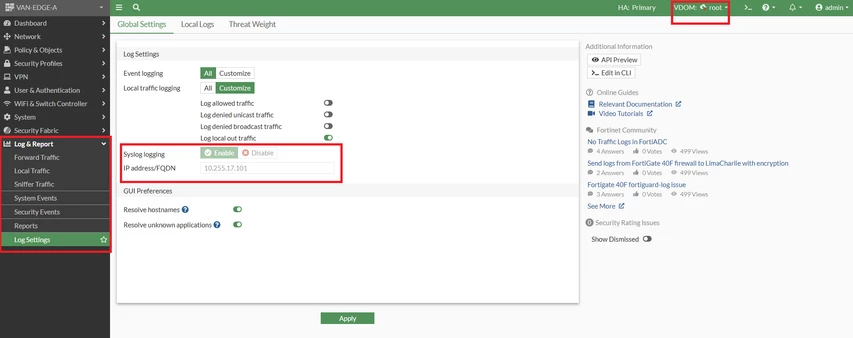
If syslog-override is enabled for a VDOM, the logs generated by the VDOM ignore global syslog settings. Any logs generated by that VDOM are forwarded according to 'config log syslogd/syslogd2/syslogd3/syslogd4 override-setting', including not sending any logs if there is no syslog server configured.
When syslog-override is enabled, VDOM-specific syslog logging is configurable in Select VDOM -> Log & Report -> Log Settings.
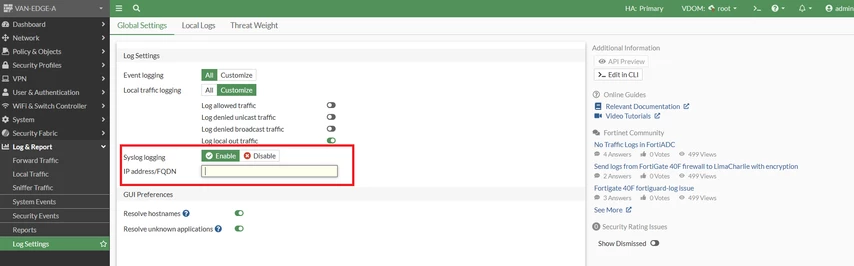
Note: all logs have an assigned VDOM including 'Global' logs such as system performance statistics and global configuration. Such logs are assigned to the management VDOM, so overriding syslog configuration for the management VDOM can change how these logs are sent. The default management VDOM is 'root'. See the following article for instructions on how to change the management VDOM: 'Technical Note: How to change management VDOM from GUI and CLI'.
See below for examples of how to override global syslog settings for a VDOM.
Solution 1 (the firmware versions 6.0.x and before):
The command 'set override enable' is available under the command 'config log syslogd override-setting', and the commands below can be used to configure the override.
From the CLI, execute the following commands, where:
x.x.x.x is the IP address of the syslog server.
'set source-ip x.x.x.x' is optional: it specifies the source IP from where the connections will originate.
config vdom
    edit "VDOM_NAME"
        config log syslogd override-setting
            set override enable
            set status enable
            set server x.x.x.x
            set port 514
            set source-ip x.x.x.x
    end
end
Solution 2 (the firmware version 6.2.x and above):
The command 'set override enable' is not available under the command 'conf log syslogd override-setting' as of FortiOS v6.2 and above. Instead, a new VDOM-wide 'set syslog-override enable' setting has been introduced to enable multiple FortiAnalyzer/syslog servers per VDOM (see Multiple FortiAnalyzer (or Syslog) Per VDOM).
From the CLI, execute the following command:
config vdom
    edit "VDOM_NAME"
        config log setting
            set syslog-override enable
        end
    end
end
Once syslog-override is enabled, the following CLI commands are available for configuring VDOM override:
To configure VDOM override for a Syslog server:
Configure the syslog override settings, where:
x.x.x.x is the IP address of the syslog server.
'set source-ip x.x.x.x' is optional: it specifies the source IP from where the connections will originate.
config log syslogd/syslogd2/syslogd3/syslogd4 override-setting
    set status enable
    set server x.x.x.x
    set port 514
    set source-ip x.x.x.x
end
Configure the override filters:
config log syslogd/syslogd2/syslogd3/syslogd4 override-filter
    set severity information
    set forward-traffic enable
    set local-traffic enable
    set multicast-traffic enable
    set sniffer-traffic enable
    set anomaly enable
    set voip enable
    set dns enable
    set ssh enable
    set ssl enable
end
The change can now be verified from the GUI.
Below is an example of how to configure the FortiGate to send logs to the Tftpd64 Syslog Server:
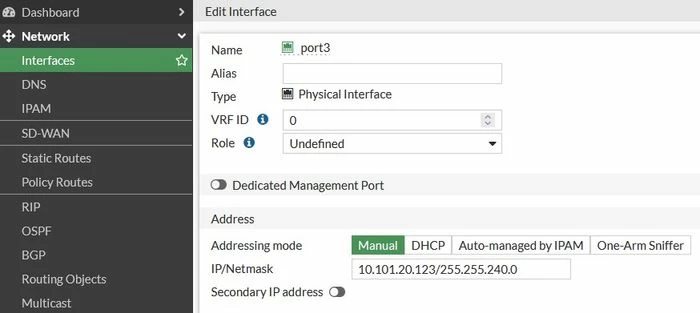
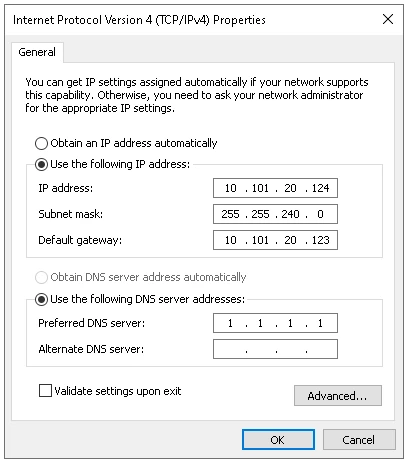
Configure the IP address form the FortiGate and from the Client where the Tftpd64 Syslog Server is installed.
10.101.20.123/20 is configured on port3 of the FortiGate.
10.101.20.124/20 is configured on the Ethernet port of the Client running on Windows 10. As a gateway, it is assigned the IP address of port3 on the FortiGate.
Execute the following commands to configure syslog settings on the FortiGate:
config log syslogd setting
    set status enable
    set server "10.101.20.124"
    set source-ip "10.101.20.123"
end
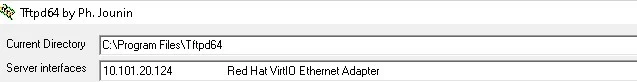
Install Tftpd64 on the client. After the installation is finished, open the application and choose the interface as below:
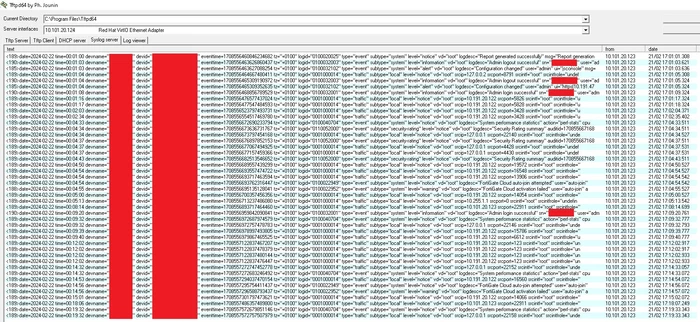
After choosing the interface, the logs will start to come to the Tftpd64 syslog server, as below:
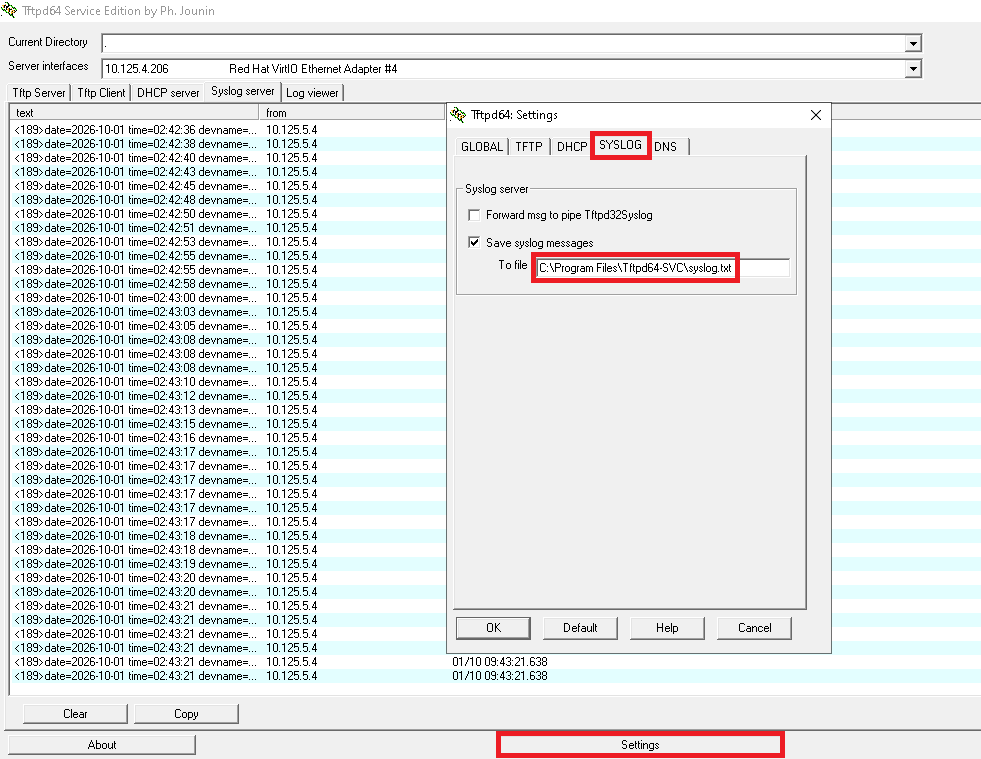
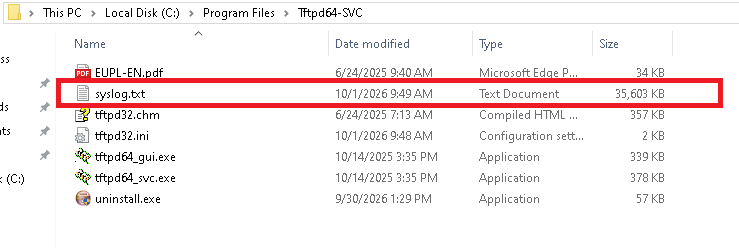
To store the output of the logs in a .txt file, go to: Settings -> SYSLOG and write the path where the file should be stored. It is only necessary to write the path: the file will be created by itself.
Note: Make sure the VDOM has a valid route to the configured syslog server, as FortiGate will otherwise not generate traffic:
config log syslogd override-setting
    set status enable
    set server "192.168.55.10"
    set interface-select-method specify
    set interface "wan1"
end

FW_prod (internet) # get router info routing-table  details  192.168.55.10

Routing table for VRF=0
Routing entry for 192.168.55.10/32
  Known via "static", distance 10, metric 0, best
  * vrf 0 192.168.0.1, via wan1
To generate a test syslog message, run the following command:
FW_prod (internet) # diagnose log test
masks:
        Virus: 0X00001
        URL: 0X00002
        DLP: 0X00004
        IPS: 0X00008
        BOTNET: 0X00010
        ANOMALLY: 0X00020
        APP: 0X00040
        APP6: 0X00080
        Deep App: 0X00100
        Email: 0X00200
        CR Web: 0X00400
        SSH: 0X00800
        SSL: 0X01000
        File Filter: 0X02000
        ICAP: 0X04000
        SCTP Filter: 0X08000
        Virtual Patch: 0X10000
        CASB: 0X20000
diag log test <repeat> [<sleep-duration(milliseconds)> <# of srcip> <# of dstip> <gen-traffic-log> <seed> <masks>]
diag log test (repeat: 1)  (sleep-duration(milliseconds): 10) (# of srcip: 10) (# of dstip: 10) (gen-traffic-log:True) (seed: 1785592185) (masks: ffffffff)
generating a system event message with level - warning
generating authentication event messages
1: generating an infected virus message with level - warning
1: generating a blocked virus message with level - warning
1: generating a URL block message with level - warning
1: generating a DLP message with level - warning
1: generating an IPS log message
1: generating an botnet log message
1: generating an anomaly log message
1: generating an application control IM message with level - information
1: generating an IPv6 application control IM message with level - information
1: generating deep application control logs with level - information
1: generating an antispam message with level - notification
1: generating a URL block message with level - warning
1: generating an ssh-command pass log with level - notification
1: generating an ssh-channel block with level - warning
1: generating an ssl-cert_blocklisted log with level - warning
1: generating FortiSwitch logs
1: generating a File Filter log with level - warning
1: generating a icap log with level - warning
1: generating a sctp filter log with level - warning
1: generating a virtual ot patch log with level - warning
1: generating a CASB monitor log with level - information
To check if there is outgoing traffic, run the following sniffer, which will show if local-out traffic is using the correct egress interface:
FW_prod (internet) # diagnose  sniffer packet  any " host 192.168.55.10 and port 514" 4 0 l
interfaces=[any]
filters=[ host 192.168.55.10 and port 514]
2026-08-01 16:08:49.114193 wan1 out 192.168.0.62.18154 -> 192.168.55.10.514: udp 575
2026-08-01 16:08:49.334115 wan1 out 192.168.0.62.18154 -> 192.168.55.10.514: udp 672
2026-08-01 16:08:50.124192 wan1 out 192.168.0.62.18154 -> 192.168.55.10.514: udp 750
2026-08-01 16:08:50.344201 wan1 out 192.168.0.62.18154 -> 192.168.55.10.514: udp 667
2026-08-01 16:08:51.354204 wan1 out 192.168.0.62.18154 -> 192.168.55.10.514: udp 672

