



Technical Tip: How to retrieve policy sequence groups from FortiGate
Description
This article describes how to see and retrieve the policy sequence groups and read them via CLI.
Scope
FortiGate up to v7.4.
Solution
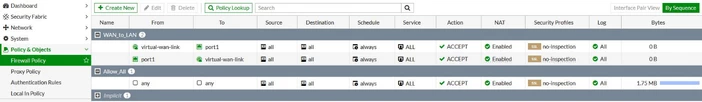
It is possible to configure sequence groups on FortiGate policies for easier management. However, if it is deleted, the user might want it back, and it does not appear in the device configuration when issuing show commands:
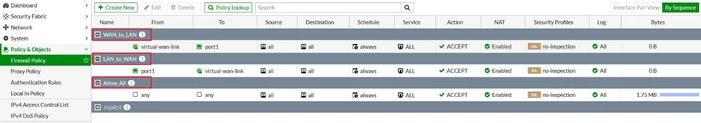
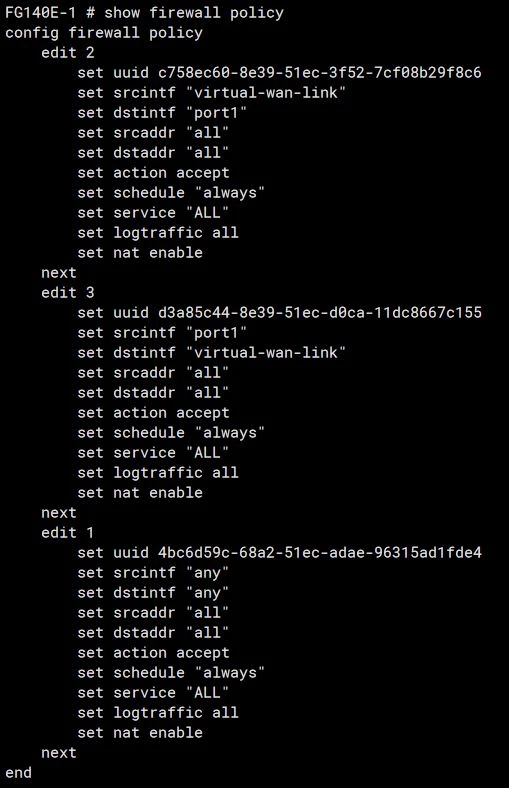
Even if sequence groups do not appear with show commands, they show on configuration backup under the name of 'global-label':
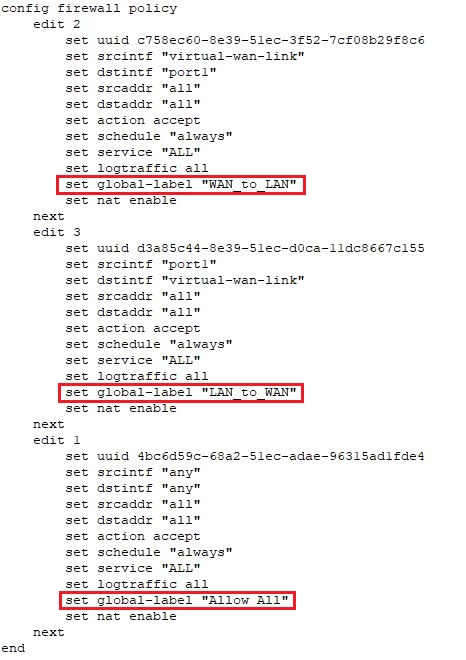
It is possible to reconfigure the group sequence either from the GUI or CLI.
CLI example:
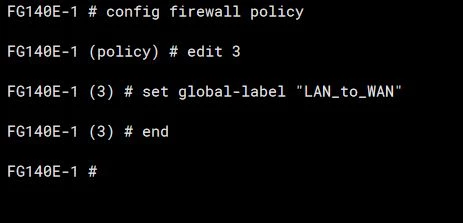
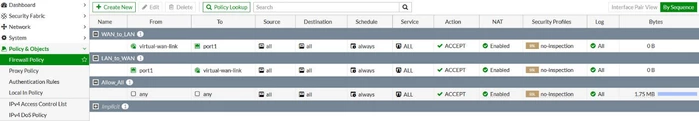
Note: The 'global-label' command is a hidden one. This means that it will not auto-complete, and it has to be completely typed out by the user.
Also, this command will not be shown in the output of a 'show' command. In order to view it, a backup of the configuration must be downloaded from the GUI.
Related articles:
Technical Tip: Design change on grouping policies in sequence groups
Technical Tip: Renaming sequence grouping for firewall policies for 'By sequence grouping' view

