




Technical Tip: How to resolve One-to-One IP Pool exhaustion
Description
This article describes how to diagnose and resolve dropped connections that occur when additional devices attempt to use a firewall policy that has an exhausted One-to-One IP Pool configured for Source NAT.
Scope
FortiOS using IP Pool for Source NAT.
Solution
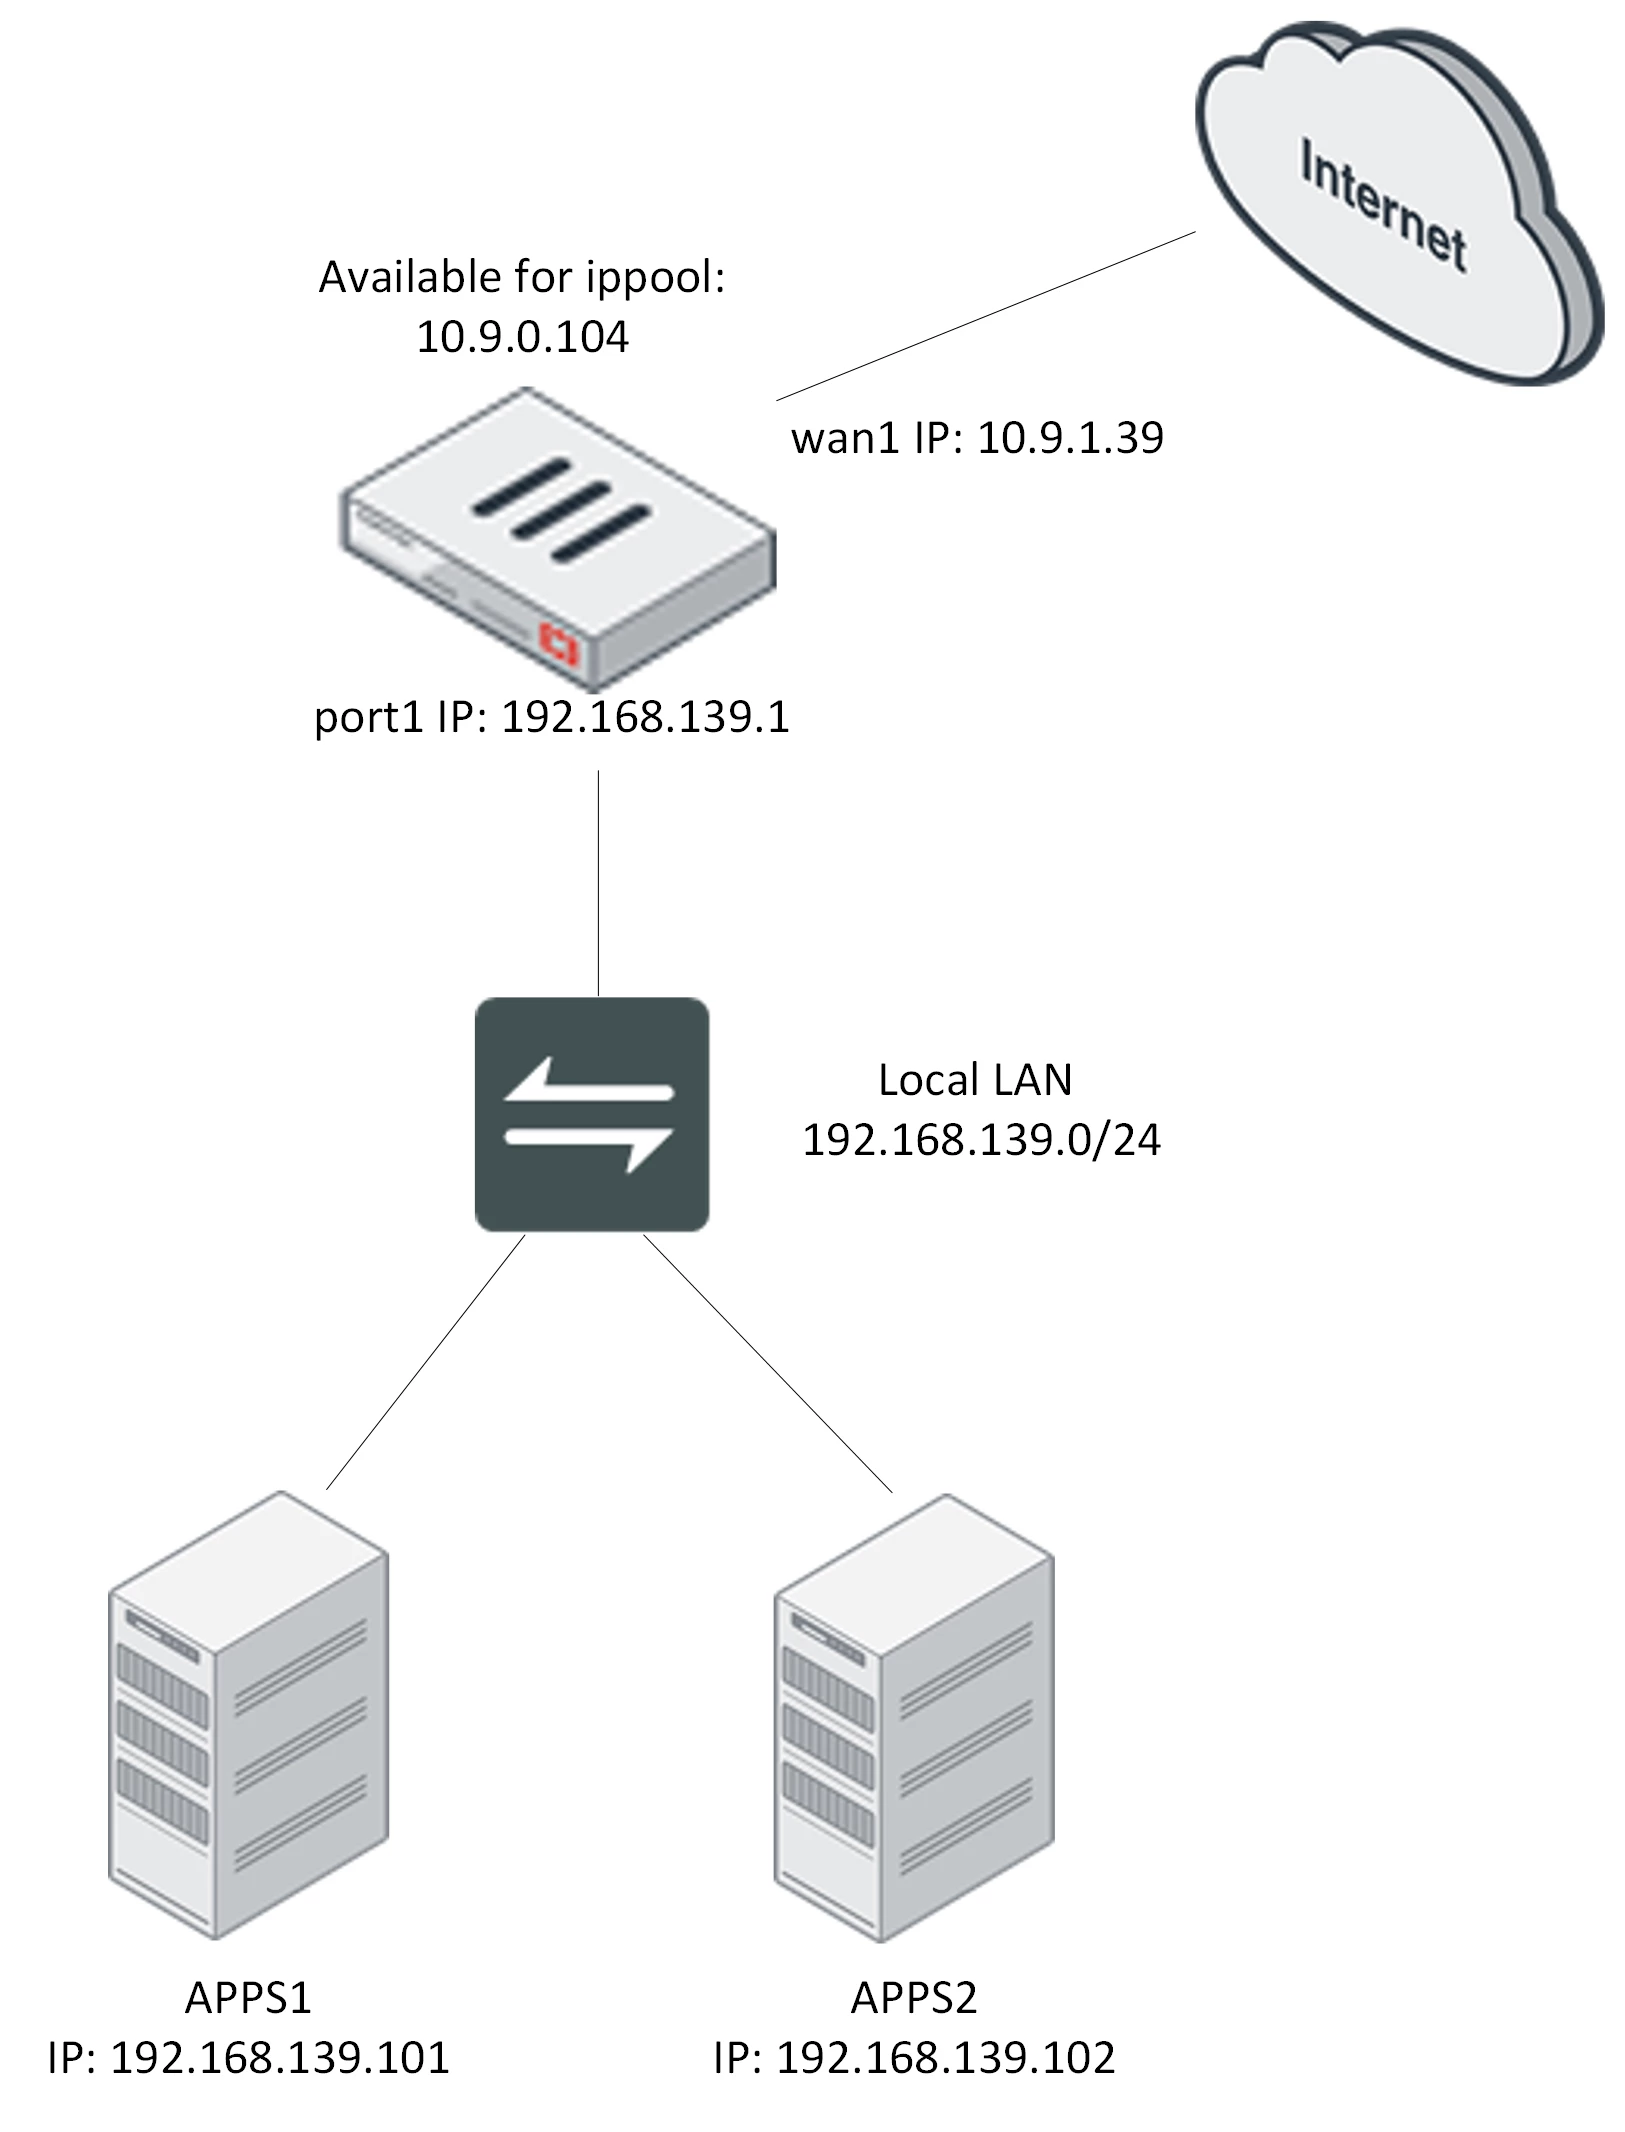
In the example topology below, the local network has two devices APPS1 and APPS2, and One-to-One IP Pool is in use. Both devices are using the FortiGate as a default gateway. APPS1 was previously able to reach resources over the Internet but is no longer able to. APPS2 is a new device and is able to access the internet.
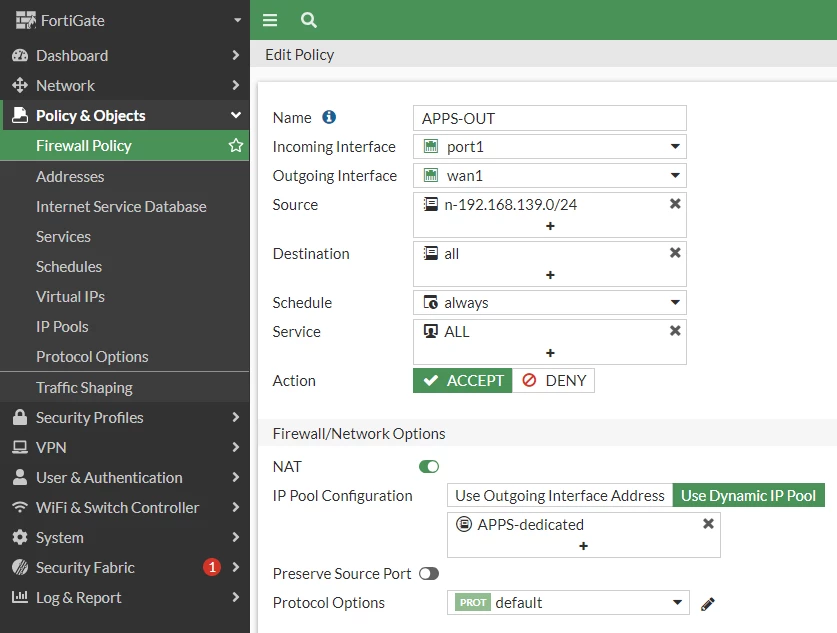
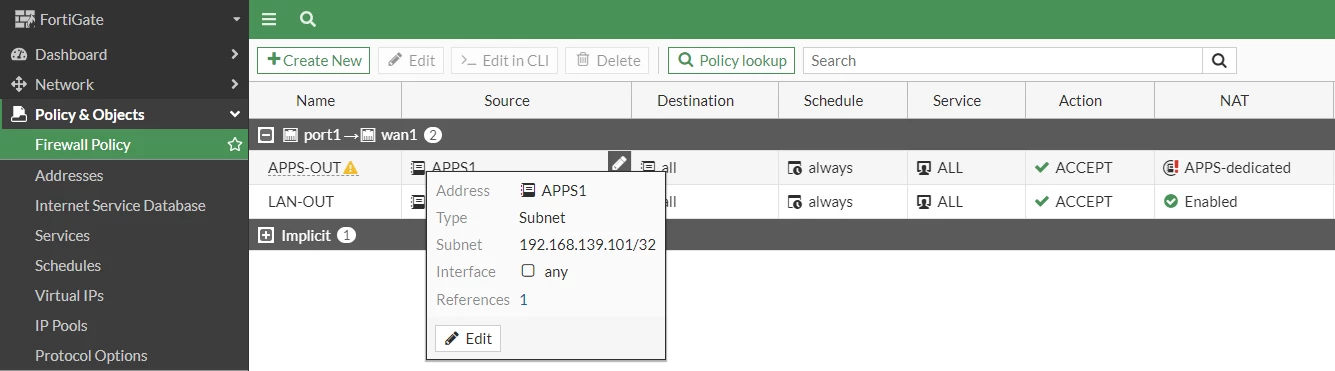
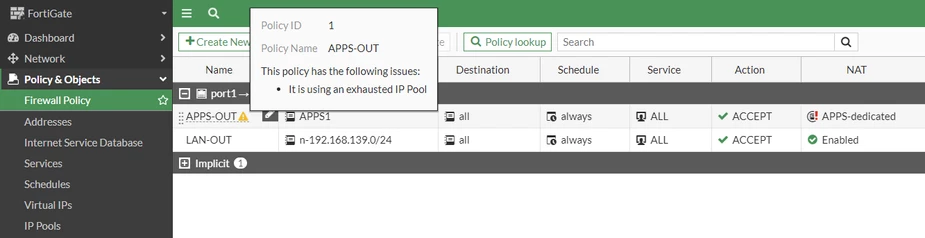
The only firewall policy currently allowing internet traffic is policy 1 'APPS-OUT', which performs source NAT to a custom IP Pool 'APPS-dedicated'.
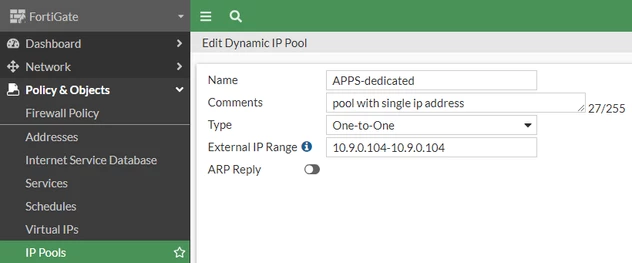
APPS-dedicated is a One-to-One IP Pool containing a single external IP address 10.9.0.104. IP Pools are configured under Policy & Objects -> IP Pools.
With this configuration, only the first device to attempt to access the Internet will be able to do so. In this case it was APPS2 and traffic from APPS1 is dropped.
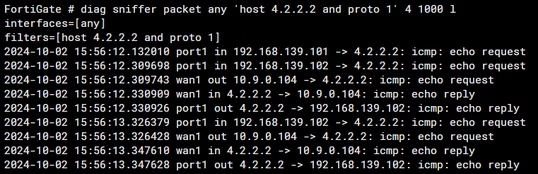
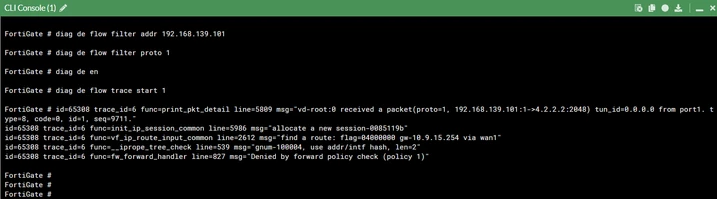
Debug flow for ICMP traffic from APPS1 shows the connection attempt is dropped by the intended policy, even though the configured action on the policy is 'accept' not 'deny'. This is by design since FortiGate can't perform the required NAT with this configuration.
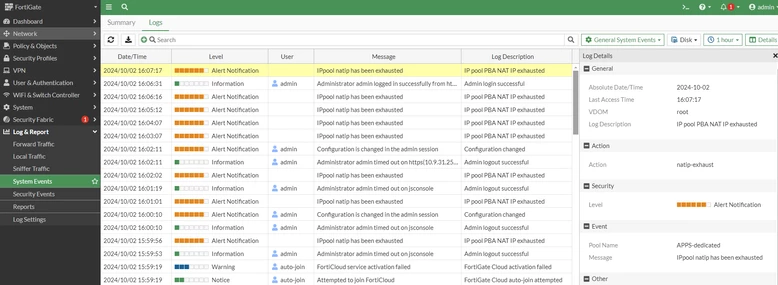
When the issue is occurring there are several logs in System Events with the Message 'IPpool natip has been exhausted'.
If the policy was configured to log all traffic, the issue will also show in Forward Traffic logs. Denied traffic will be logged with 'NAT Translation noop' for No Operation.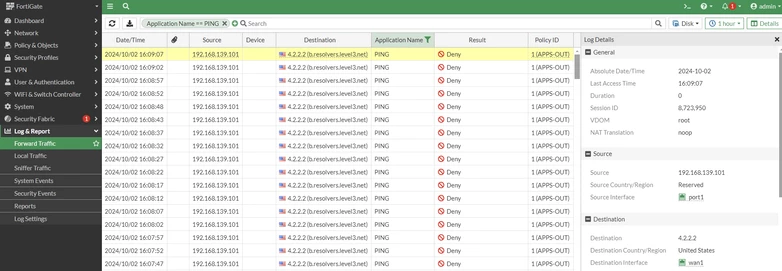
Logs showing the allowed traffic will have 'NAT Translation snat' as normal.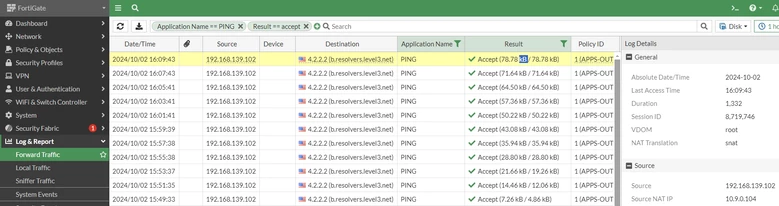
Resolution:
To resolve the dropped connections issue, use whichever of the following options match the existing network requirements.
- Change the IP Pool type to Overload, which allows multiple devices to share a single external IP address.
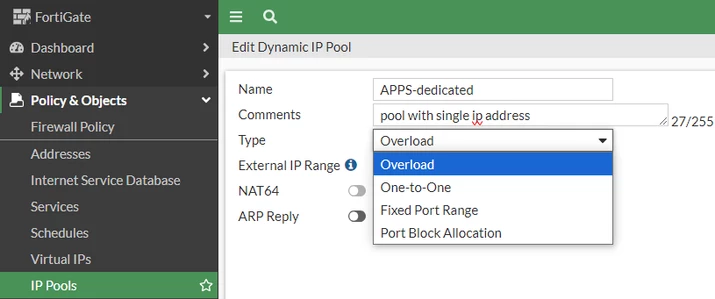
- Reconfigure the External IP Range in the IP Pool to include enough addresses for each device that will match the firewall policy.
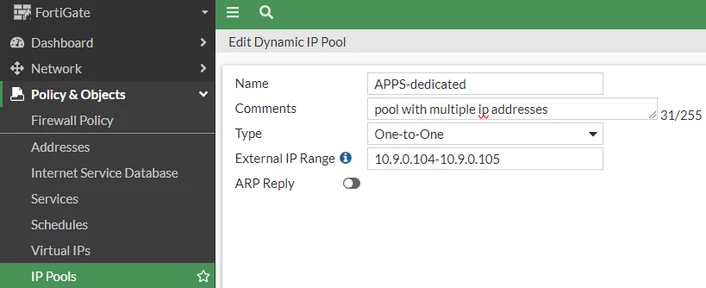
config firewall ippool
edit "APPS-dedicated"
set type one-to-one
set startip 10.9.0.104
set endip 10.9.0.105
next
end
- Restrict the existing firewall policies so that only intended devices will use the configured IP Pool. Configure additional firewall policies for additional devices as needed, and do not re-use the same IP Pool for these policies.
After implementing any of the above solutions, the intended internal devices will be able to access external resources with the intended NAT.
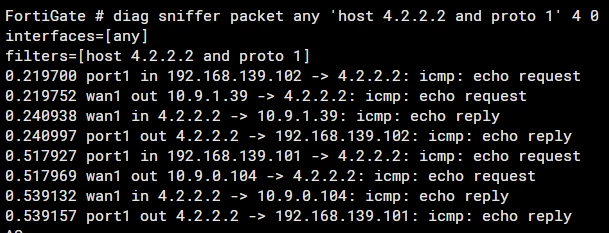 In this example, APPS1 is matching the APPS-OUT policy and APPS2 is matching the LAN-OUT policy. APPS2 has the default source NAT to FortiGate's wan1 ip.
Note the firewall policy will show an exhausted IP Pool warning in GUI if the policy is using a full One-to-One IP Pool. This warning appears whenever all addresses in the Pool are assigned to devices. In this example, only APPS1 can match the APPS-OUT policy so the warning is expected and not an issue.
Related documents: