
Technical Tip: How to Push FortiGate VPN Configurations via FortiManager
Description
This article describes how to create, manage, and push FortiGate IPsec VPN configurations using FortiManager, enabling centralized provisioning and simplified deployment of VPN tunnels across multiple devices.
Scope
FortiGate, FortiManager.
Solution
FortiGate is managed by FortiManager, and the configuration is in sync.
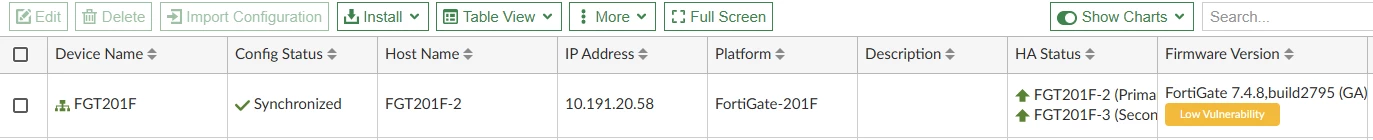
If the IPsec VPN configuration is performed locally on the FortiGate after it is managed by FortiManager, the configuration status will show as out of sync, which is not recommended. The best practice is to push the VPN configuration directly from FortiManager to the FortiGate.
- To create an IPsec VPN template in FortiManager, follow these steps:
Go to Device Manager -> Provisioning Templates -> IPsec Tunnel Templates.
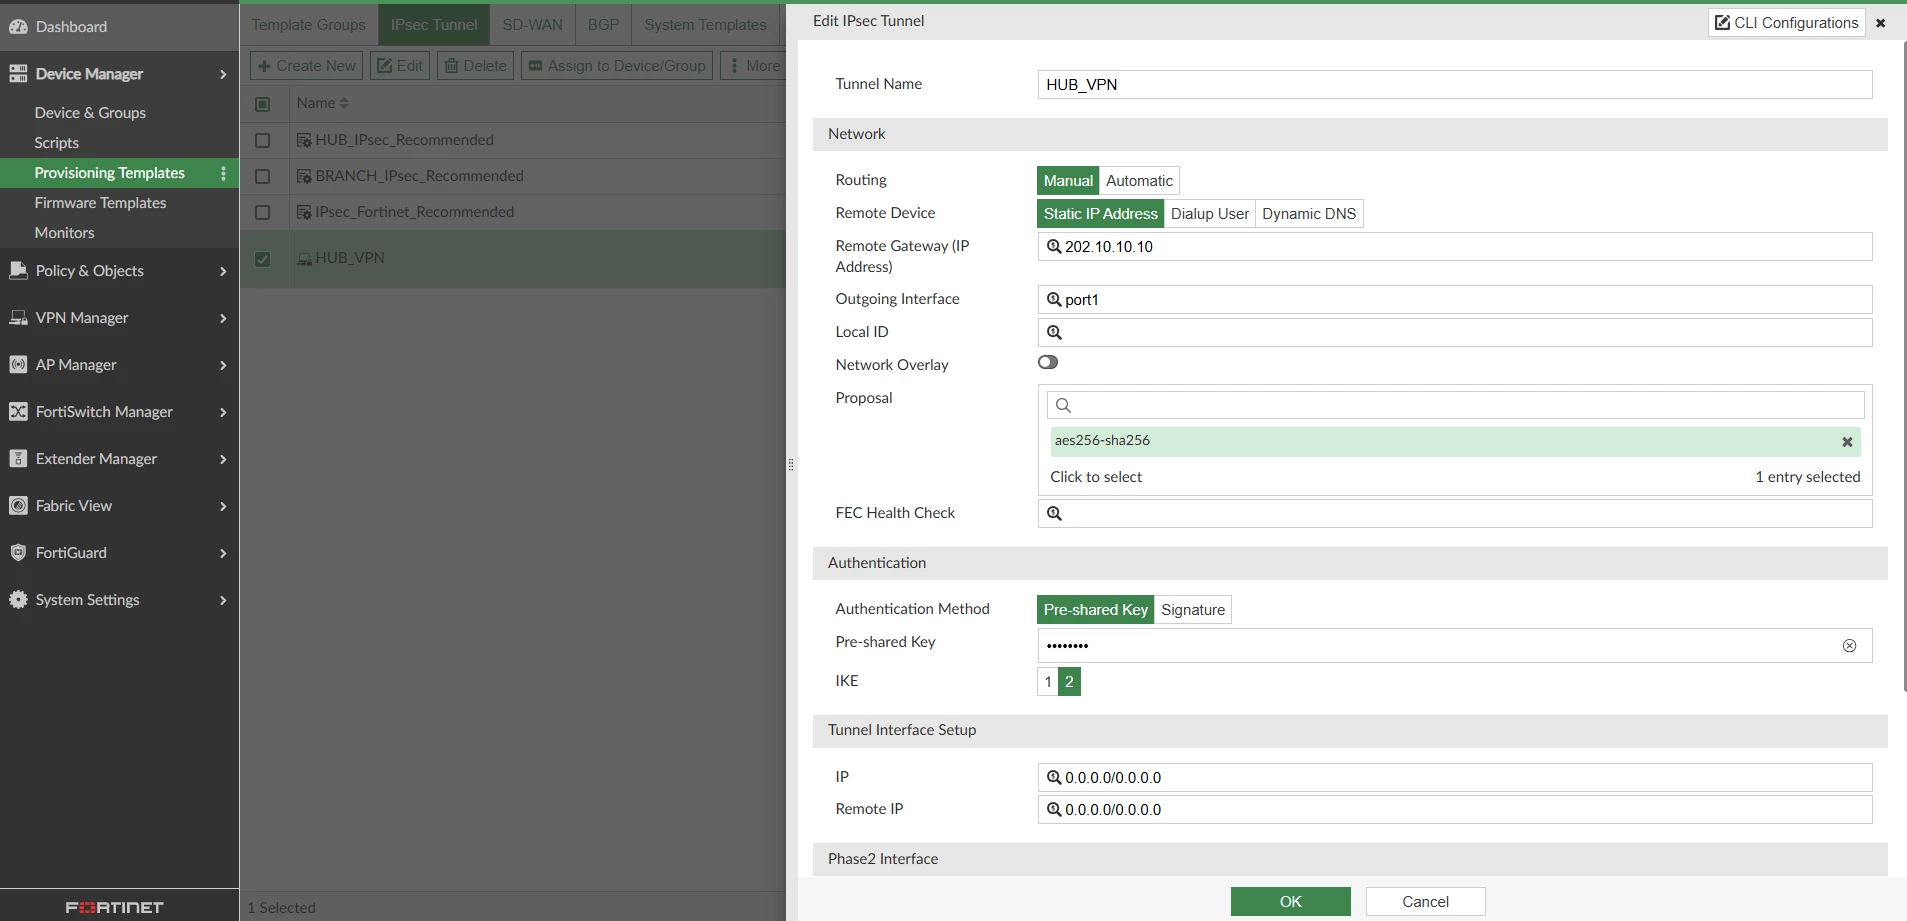
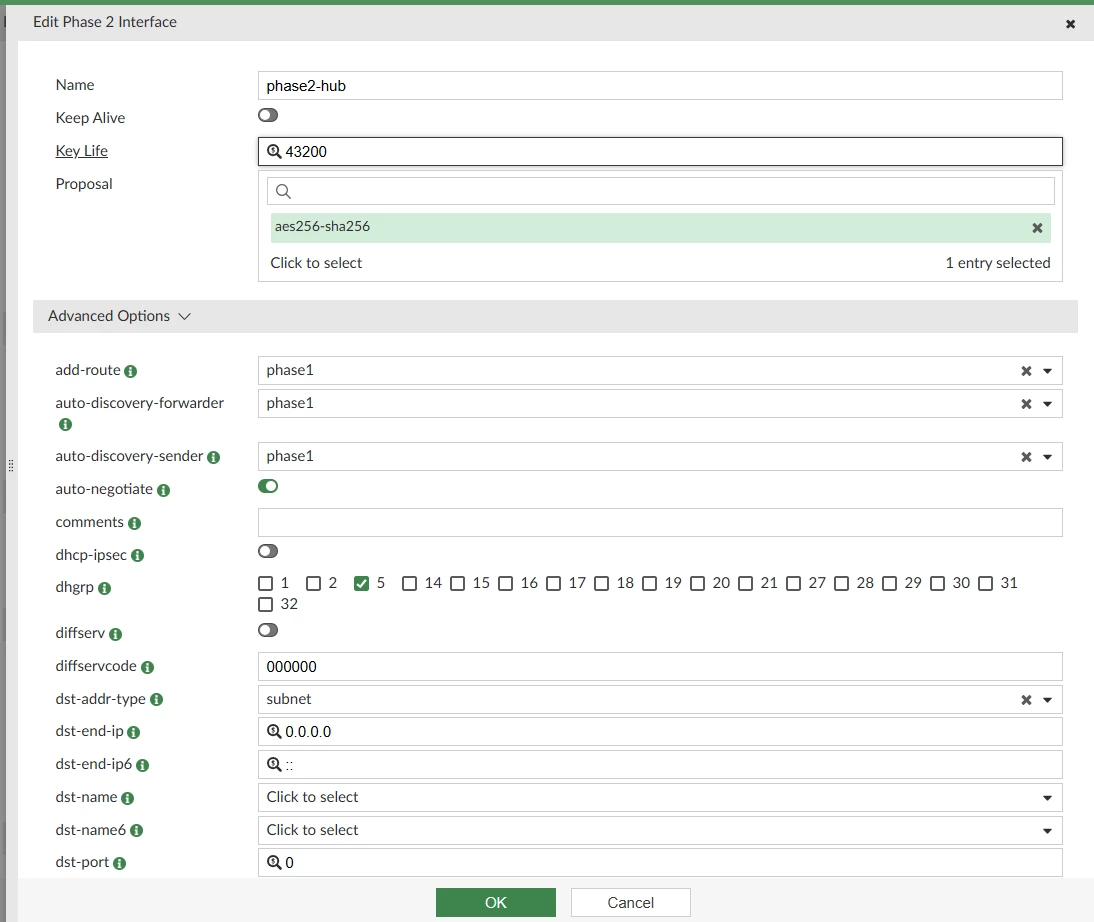
IPsec VPN templates in FortiManager follow the same setup procedure as the FortiGate GUI. All parameters available in the FortiGate CLI can also be configured in the FortiManager IPsec template GUI by expanding the advanced options.
Select OK to save the settings. The IPsec VPN template is now created and can be assigned to target devices
- The provision template can be assigned to the device as below:
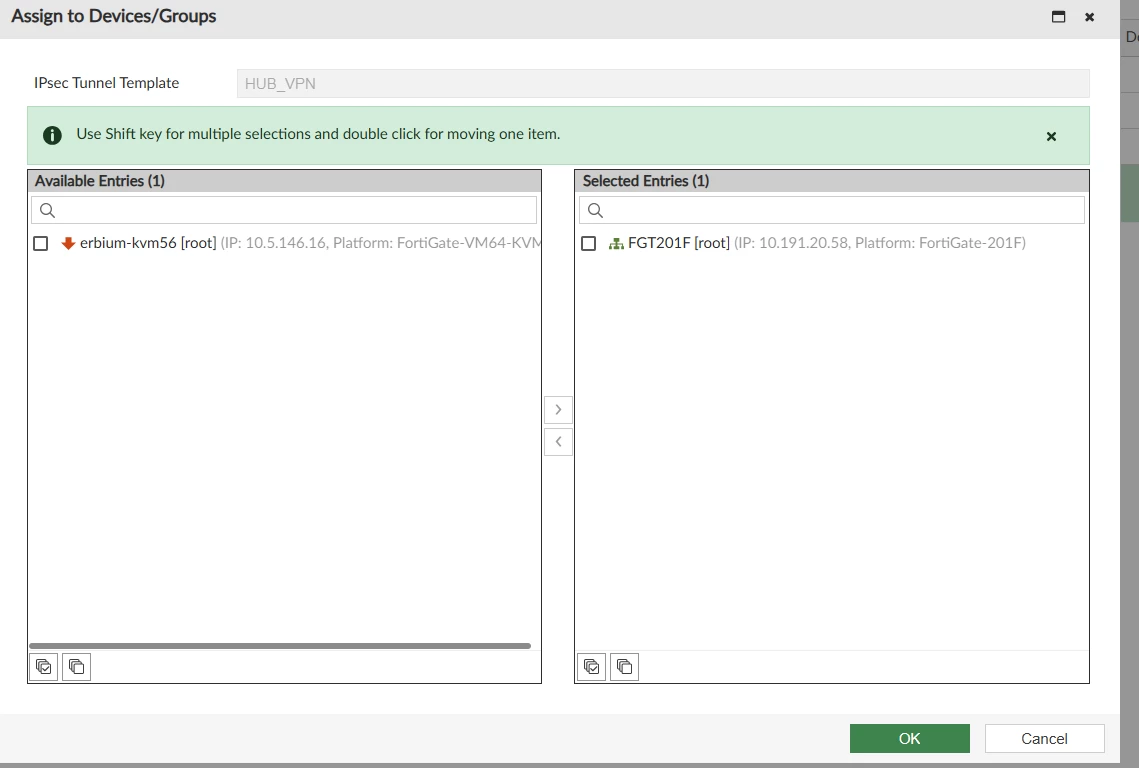
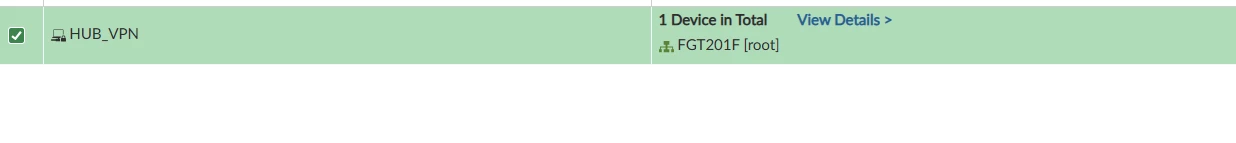
- To install the VPN configuration, select Install Wizard:
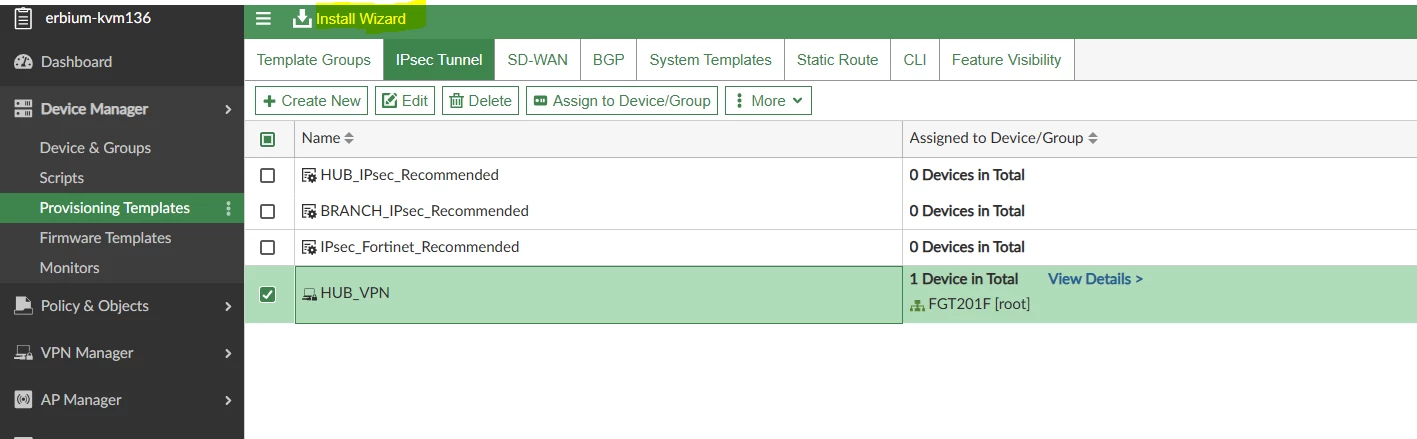
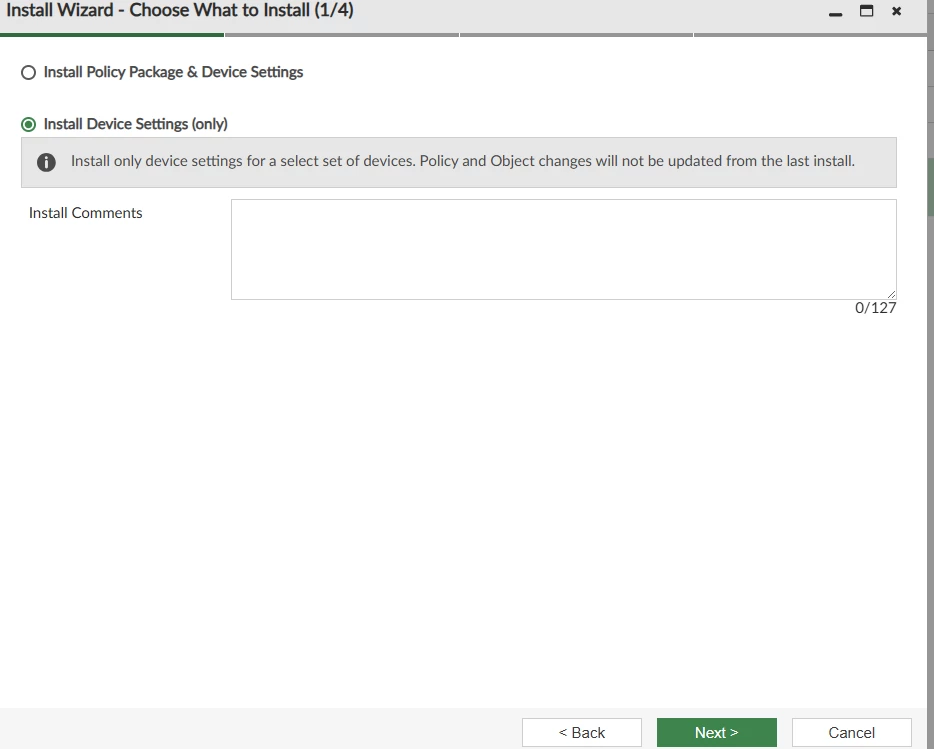
- Select on Device Settings only:
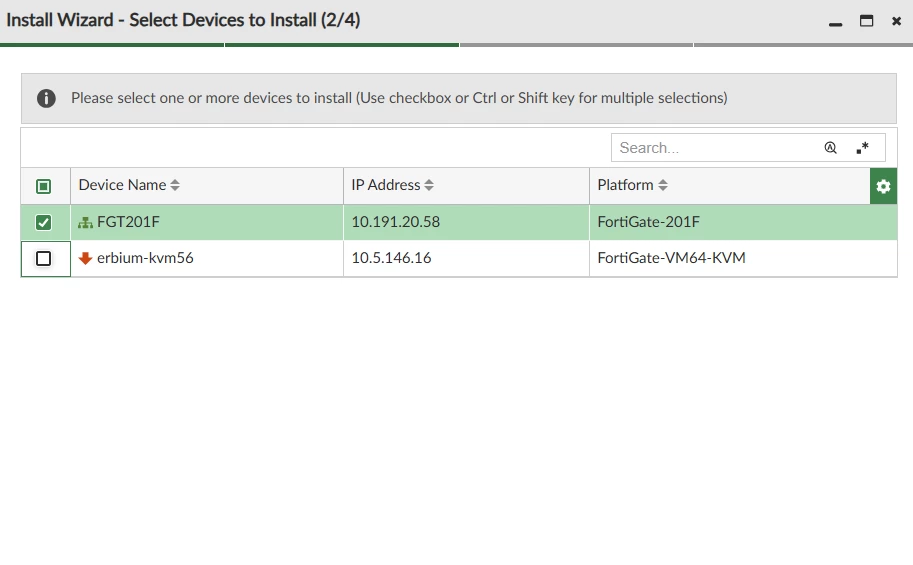
- Select the target device to which the configuration will be pushed.
- It is recommended to always review the installation preview, as it provides a clear view of the exact configuration that will be pushed.
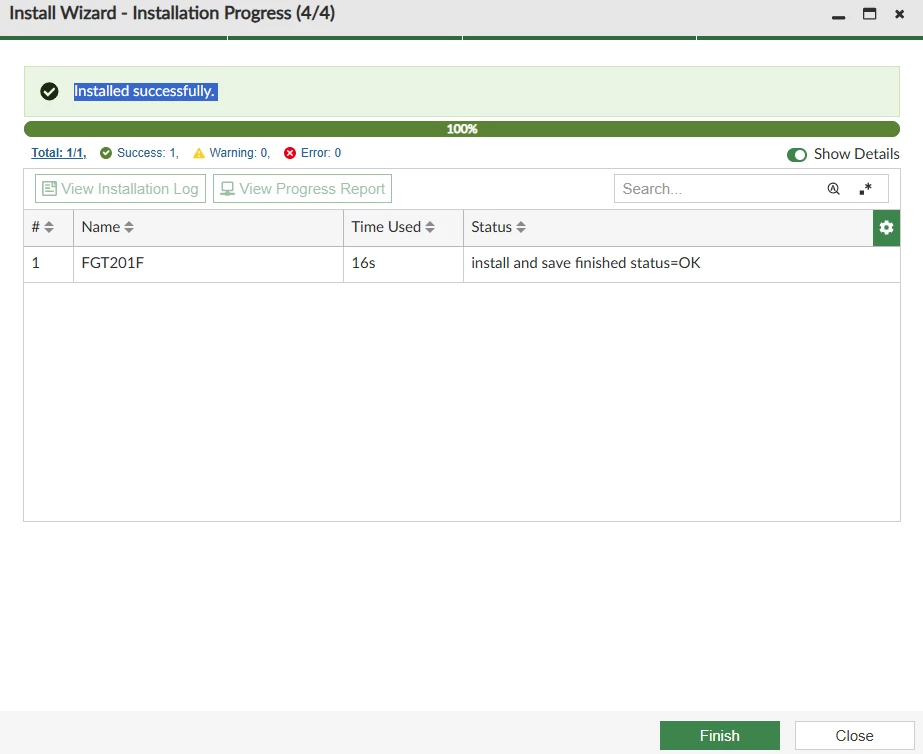
Once the installation completes, it will show as Installed successfully.
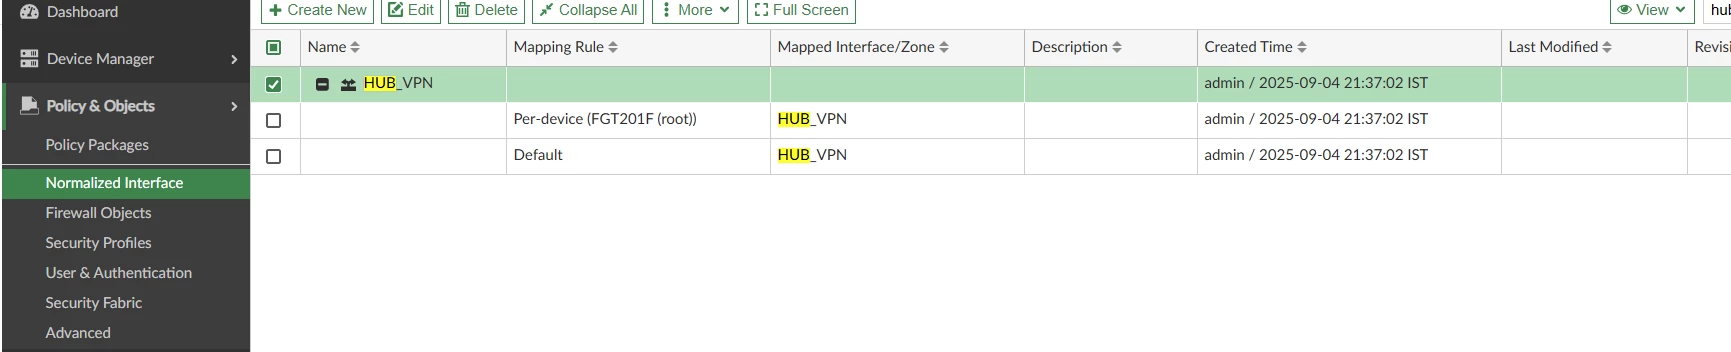
- Before pushing the policy packages for the VPN interface, create a normalized interface, and device mapping can be done.
- Policies can be created and then deployed to devices using the Install Wizard to push the policy package.
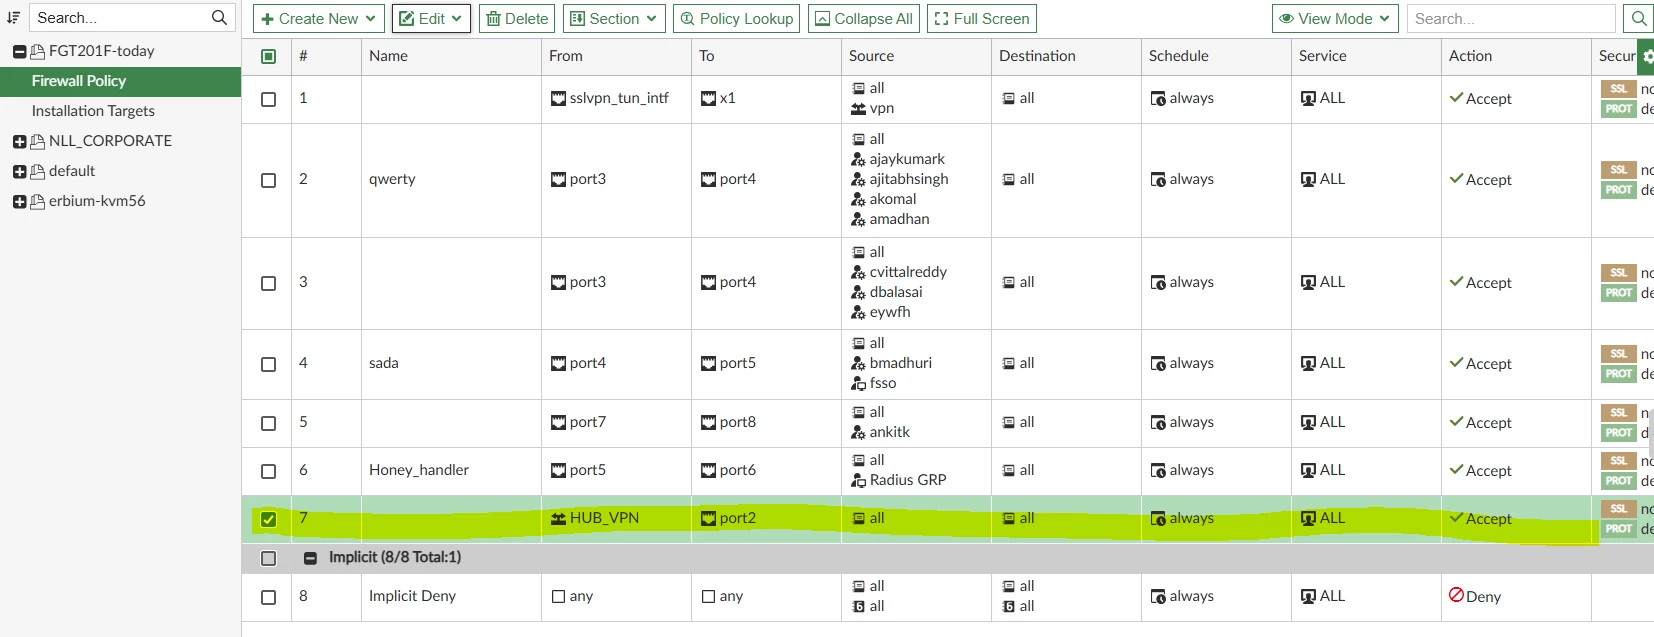
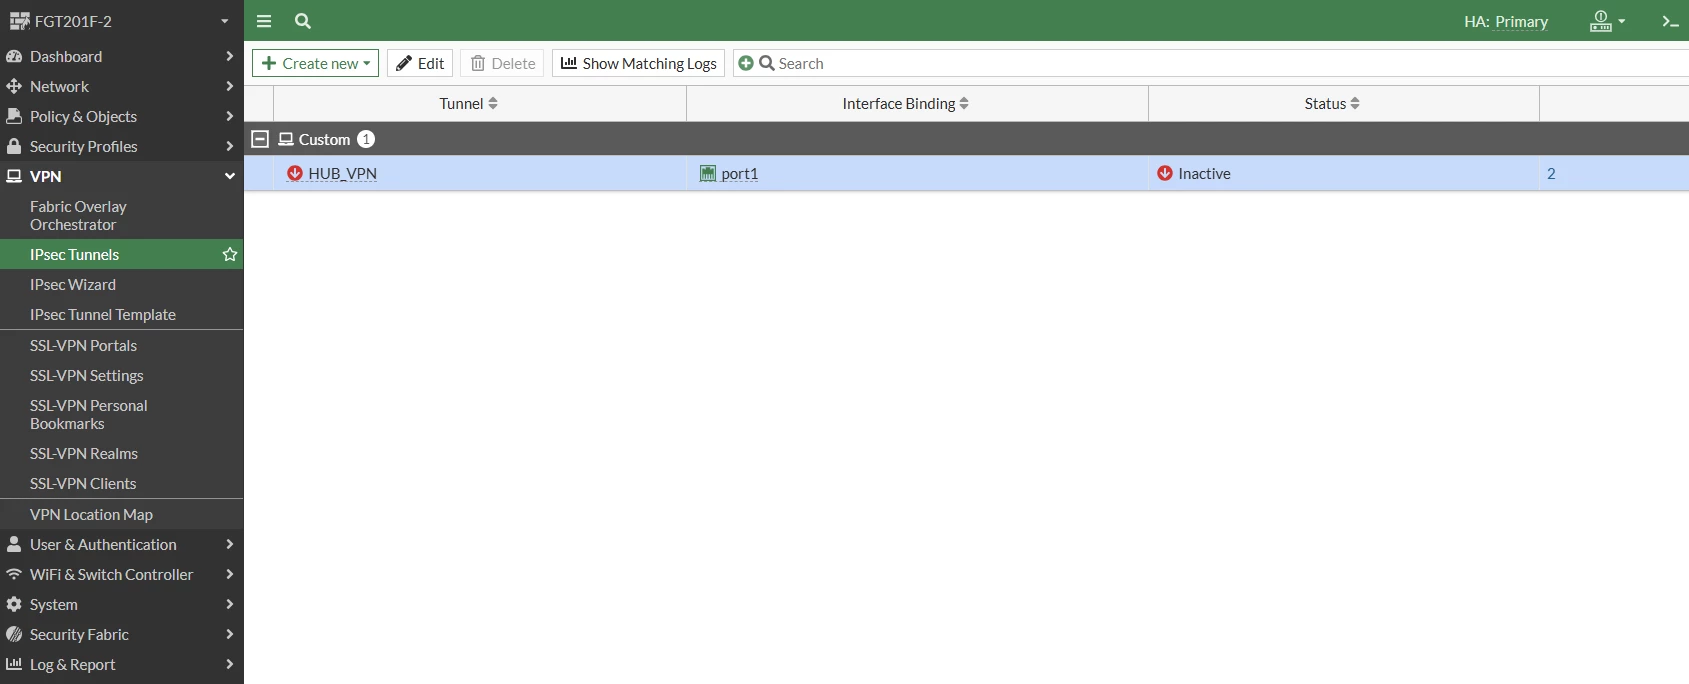
Once the install wizard is done and the policy package is pushed, it is possible to see the policy and VPN config present on the FortiGate, which indicates that FortiManager has successfully pushed the needful configuration.
Note: Static route can also be configured on the FortiManager and installed on the respective FortiGate.
- On the FortiGate, the presence of both the VPN and policy configurations can be verified.