anignan
Staff
Staff
November 20, 2023

Technical Tip: How to prevent IPv6 addresses from using NAT64

  • November 20, 2023
  • 0 replies
  • 1007 views
Description This article describes how to prevent one or more IPv6 addresses from using the NAT64 firewall policy.
Scope All versions of FortiOS.
Solution

There are 2 options to prevent IPv6 addresses from using NAT64 policies

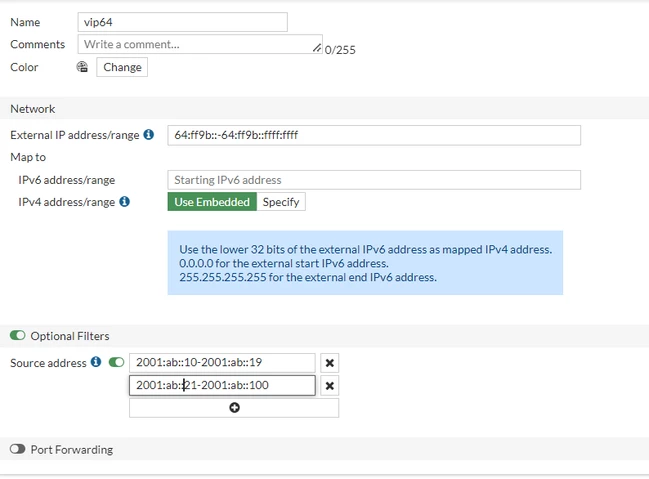
  • In the Virtual IP, specify the range of allowed IPv6 addresses in the source filter. In this screenshot, 2001:ab::20 is not in the range so it will be prevented from usingNAT64:


MicrosoftTeams-image.png


  • Use an IPv6 address group as a source in the NAT64 firewall with source-negate enabled, which means that all IPv6 addresses will be allowed except for the specified source:

config firewall policy
    edit 1
        set name "nat64"
        set srcintf "port5"
        set dstintf "WAN1"
        set action accept
        set nat64 enable
        set srcaddr6 "2001:ab::20"
        set dstaddr6 "vip64"
        set schedule "always"
        set service "ALL"
        set ippool enable
        set poolname "vip64"
        set srcaddr6-negate enable
    next
end


All IPv6 addresses will be allowed except for 2001:ab::20.. It is possible to have a range or a list of IPv6 addresses.


Related article:

Simplify NAT46 and NAT64 policy and routing configurations - FortiGate documentation.

    Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
    Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!