The FortiGate supports multiple certificates at a single SSL profile. 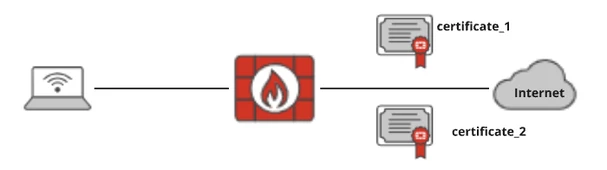 config firewall ssl-ssh-profile
set server-cert-mode
re-sign Multiple clients connecting to multiple servers.
replace Protect an SSL server.
set server-cert-mode replace
set server-cert
name Certificate list.
certificate_1
certificate_2
certificate_3
certificate_4
certificate_5
certificate_6
certificate_7
certificate_8
certificate_9
certificate_10
Note:
If the message shows 'Server certificate replace mode cannot support category exempt', follow these steps: Edit the offending SSL/SSH inspection profiles by switching from 'Protecting SSL Server' to 'Multiple Clients Connecting to multiple Servers' and then remove the FortiGuard categories from the 'Exempt from SSL inspection' list. After that, change back to 'Protecting SSL Server' and select OK.
config firewall ssl-ssh-profile
(ssl-ssh-profile) # edit "Multi-cert"
    edit "Multi-cert"
        config https
            set ports 443
            set status deep-inspection
            set quic inspect
        end
        config ftps
            set ports 990
            set status deep-inspection
        end
        config imaps
            set ports 993
            set status deep-inspection
        end
        config pop3s
            set ports 995
            set status deep-inspection
        end
        config smtps
            set ports 465
            set status deep-inspection
        end
        config ssh
            set ports 22
            set status disable
        end
        config dot
            set status disable
            set quic inspect
        end
set server-cert-mode replace
set server-cert "certificate_1" " certificate_2" " certificate_3" " certificate_4" " certificate_5" " certificate_6" " certificate_7" " certificate_8" " certificate_9" " certificate_10"
    next
end
For the configuration of the firewall policy that uses the SSL profile, refer to Define multiple certificates in an SSL profile in replace mode. FortiGate supports a maximum of 10 certificate files in a single SSL profile. Upon attempting to use multi-domain certificates to serve more than 10 domains in a single SSL profile, the system will only consider the first 10 certificate files. FortiGate will match the Server Name Indication (SNI) with the alternative names in these certificates during the SSL handshake. If the SNI matches any of the alternative names in the certificates, FortiGate will use the corresponding certificate for the connection. FortiGate will handle the SNI matching with the alternative names in the multi-domain certificates, allowing for flexibility in securing multiple domains with a single certificate.
Related document:
| 




