Technical Tip: How to make only IPv6 IP visible for IPsec VPN Remote Gateway
| Description | This article describes how to make only IPv6 visible for the IPsec VPN Remote Gateway. |
| Scope | FortiGate. |
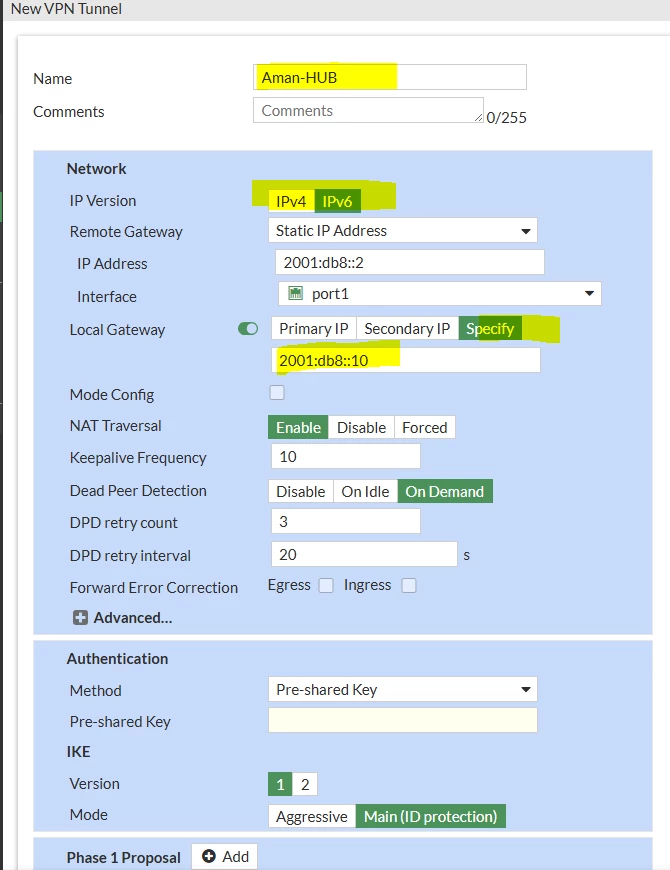
| Solution | Go to the IPsec phase1 settings, enable the 'Local Gateway' option, choose the option 'Specify' and enter the particular IPv4 and IPv6 address:
CLI commands for specifying the Local gateway IP:
config vpn ipsec phase1-interface edit "<name>" set local-gw x.x.x.x next end
Note: Always verify the local-id settings under phase1 configuration in case the remote side is specifying local and remote IDs. By default, FortiGate is going to use the primary IP for an IKE identification payload. Along with local-id settings, verify local-id type too. Additionally, while the SSL VPN configuration allows specifying the listen interfaces, it does not provide an option to designate a specific IP address as the gateway within the SSL VPN settings, like IPsec.
Note: FortiClient (Windows) v7.4.4–v7.4.5 and FortiClient (macOS) v7.4.5 do not support IPv6 for IPsec VPN: see the Special Notices in the FortiClient 7.4.5 (Windows) release notes.
Related article: |