Technical Tip: How to import missing CA certificate of certificate chain to resolve the certificate error message using OCSP information
| Description | This article describes how to import the missing CA certificates of the certificate chain to resolve the certificate error message using OCSP information.
A certificate error message can appear while using the certificate for accessing any site such as a captive portal site, SSL VPN page, etc. If Certificate Authority cannot be verified by the browser for the certificate being used. There can be times when a certificate can be signed by intermediate CA and Root CA as can be seen in the certificate chain. |
| Scope | FortiGate v7.x. |
| Solution | An internet protocol called OCSP, or Online Certificate Status Protocol, verifies a certificate's validity in real-time. An essential component of Extended Validation SSL certificate construction, OCSP is a real-time certificate status check. A user's browser often does an OCSP check with the CA that issued the SSL certificate when it establishes an https:// connection with a web server to make sure the certificate has not been revoked.
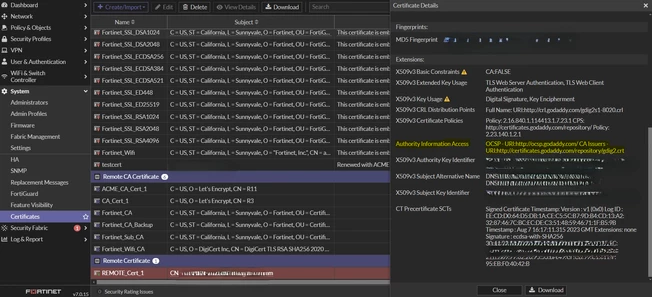
CA issuers can be verified by selecting the certificate on the FortiGate as shown in the screenshot:
Note the ‘Extension’ field 'Authority Information Access' as it provides the information of the CA of the certificate.
Authority Information Access: OCSP - URI: http://ocsp.godaddy.com/ CA Issuers- URL: http://certificates.godaddy.com/repository/gdig2.crt
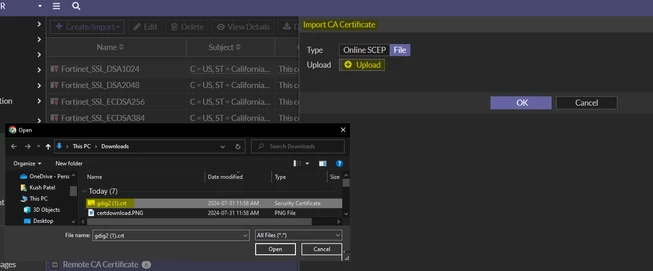
CA certificate ‘GDIG2.CRT’ can be downloaded using the link ‘http://certificates.godaddy.com/repository/gdig2.crt’ provided as ‘CA Issuers’ and imported as CA Certificate successfully.
To import, select ‘Create/Import’ -> ‘CA Certificate’ :
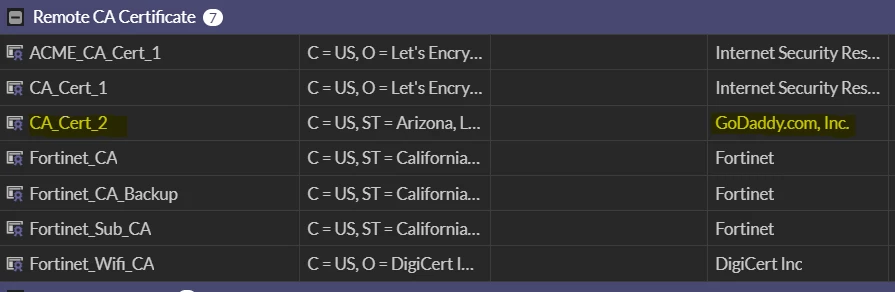
The CA certificate will be imported successfully as shown in the picture:
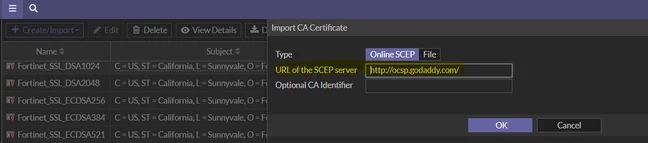
Another way to import the CA certificate is by using the OCSP URL provided as demonstrated in the screenshot:
Authority Information Access: OCSP - URI: http://ocsp.godaddy.com/ CA Issuers - URL: http://certificates.godaddy.com/repository/gdig2.crt.
Related article: Technical Tip: How to avoid certificate error message by chaining Root CA and Intermediate CA certificates on FortiGate |