shahrukh_khan
Staff
Staff
March 27, 2026

Technical Tip: How to implement daily internet data quota per user or per IP

  • March 27, 2026
  • 0 replies
  • 416 views
Description

This article describes how to enforce a daily internet usage quota (for example, 500 MB per day that automatically resets at midnight) for end users or source IPs.

Scope

Applies to FortiGate models running FortiOS v7.2.0 and above.

Works for both authenticated users and unauthenticated traffic (tracks by source IP).

Counts only HTTP/HTTPS traffic that passes through proxy-based web filtering + SSL inspection.

Non-web protocols are not counted.

Solution

The solution uses the built-in Category Usage Quota feature inside a proxy-based Web Filter profile.

FortiGate does not have a global 'total traffic quota' for all protocols, but the Category Usage Quota inside a Web Filter profile achieves the desired result for typical internet usage.


Step-by-Step Configuration:

  1. Create a Category Group that covers 'All Web Traffic':
    Add all FortiGuard categories (or at least the high-usage ones: Bandwidth Consuming, General Interest, Streaming Media, Social Media, etc.).


config webfilter category

    edit "All-Web-Traffic"

        set members "Bandwidth_Consuming" "General_Interest" "Streaming" "Social_Media" ... (add all desired categories)

    next

end


  1. Create a Web Filter Profile:


config webfilter profile
    edit "Daily-Quota-500MB"
        set feature-set proxy
            config web
                  set category-usage-quota enable
            end
            config ftgd-wf
                config filters
                    edit 1
                        set category "All-Web-Traffic"
                        set action monitor
                    next
                end
                config quota
                    edit 1
                        set category "All-Web-Traffic"
                        set type bandwidth
                        set value 500
                        set unit MB
                    next
                end
            end
    next
end


  1. Apply the Web Filter Profile to the Internet Firewall Policy:


config firewall policy
    edit <policy-ID>
        set web-filter "Daily-Quota-500MB"
        set ssl-ssh-profile "deep-inspection" <----- Or any applicable deep-inspection profile.
        set utm-status enable
    next
end


Configure the Category usage Quota using the GUI:


Navigate to Security Profiles -> Select Web Filter > edit the Web Filter Profile. 

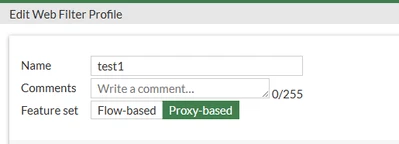
Enable proxy-based feature settings.


image.png


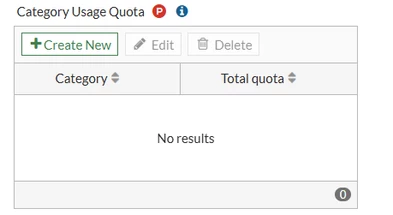
Select Create New in the Category Usage Quota.

 image.png


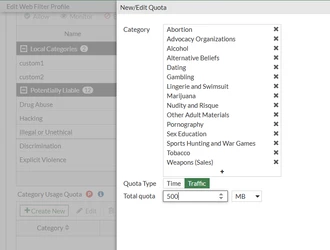
Select the category that should be allowed in the Quota.

Set the type to Traffic with a bandwidth of 500MB.

Select OK to apply the settings.


image.png


Once the settings above have been configured, create a new policy and enable the web filter feature on the policy and call the profile 'Daily-Quota-500MB' and save the configuration.

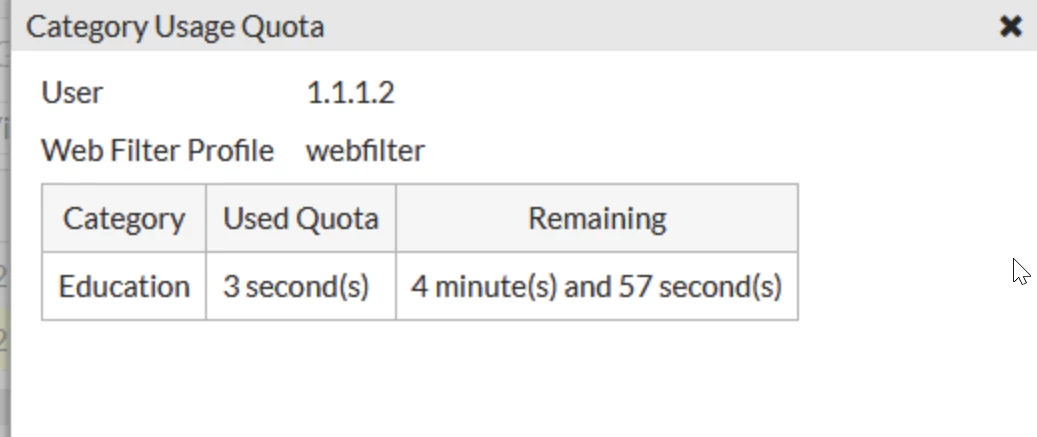
To verify the quota usage
go to Dashboard -> FortiGuard Quota Monitor to check the used and remaining time.

Usage quota.png


Important notes and limitations:

  • Only web (HTTP/HTTPS) traffic is counted.
  • This process requires proxy-based inspection + deep SSL inspection.
  • For all-protocol daily quotas or strict per-IP enforcement without authentication, consider adding a FortiAuthenticator (official best practice).
Thought Leadership Security Summit. Outpace New Threats with AI - enhanced defense. Tuesday, Septmeber 15, 8:30 AM - 2:30 PM PT. The Golf Club at Newcastle, WA.
Virtual event | September 2026. SASE summit. The age of autonomous trust. Register here!