



Technical Tip: How to identify the direction of frames in a packet capture
| Description | This article describes how to identify the direction of frames in a packet capture when using 'any' interface when running 'diagnose sniffer command'. The following scenario uses UDP an example and transparent mode FortiGate. |
| Scope | FortiGate. |
| Solution | Using the verbose 4, 5 or verbose 6 on a 'diagnose sniffer command' it will be possible to determine whether a packet is incoming or outgoing.
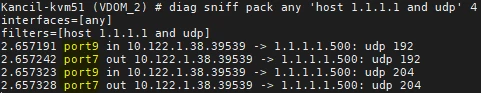
However, it can be challenging to identify the UDP packet direction on a transparent mode FortiGate when the packet capture(pcap) file alone is available where the said pcap file was gathered while filtering 'any' interface when running 'diagnose sniffer command' from a transparent mode FortiGate.
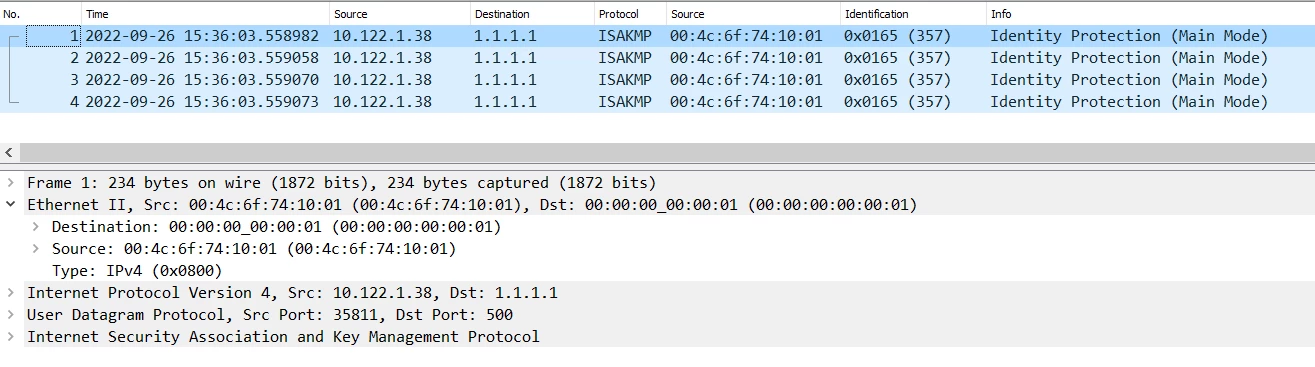 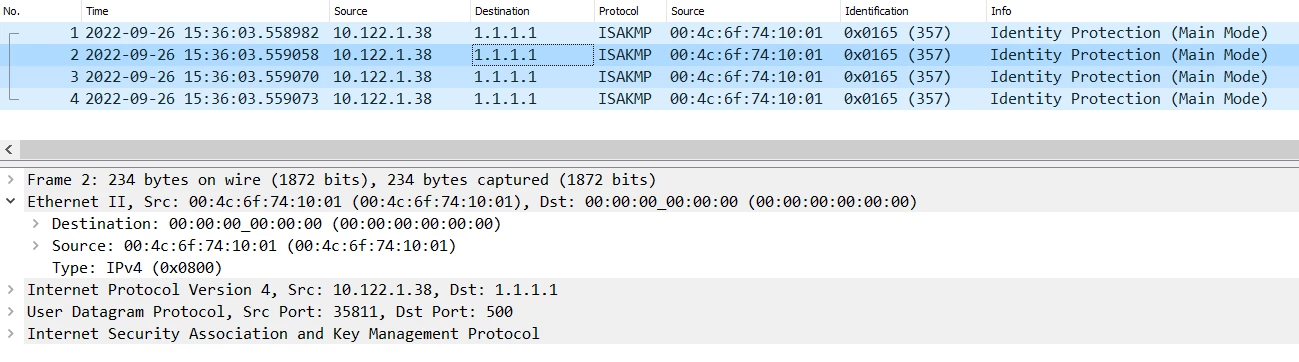
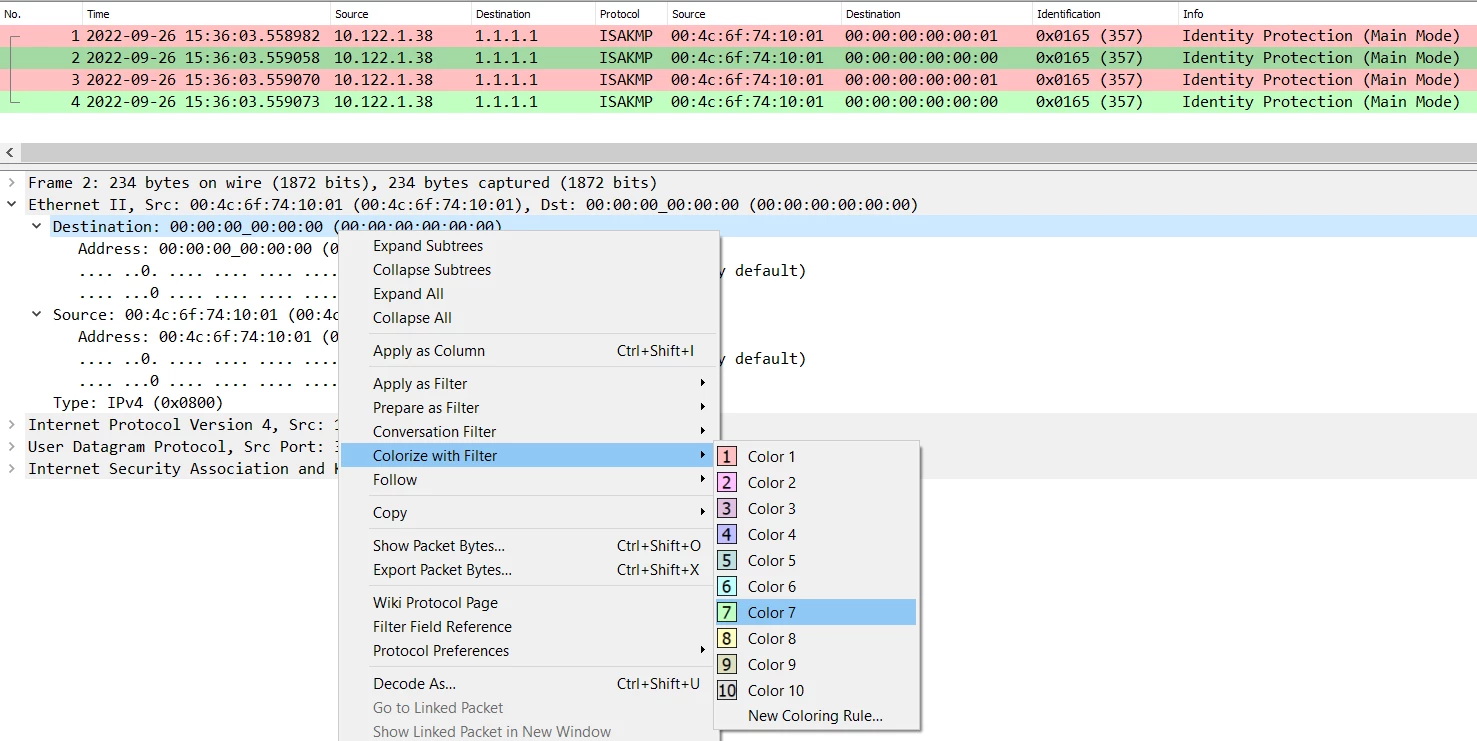
To identify whether a particular frame is incoming or outgoing, it is necessary to look at the destination Ethernet address.
00:00:00:00:00:01 means the packet is incoming 00:00:00:00:00:00 means the packet is outgoing
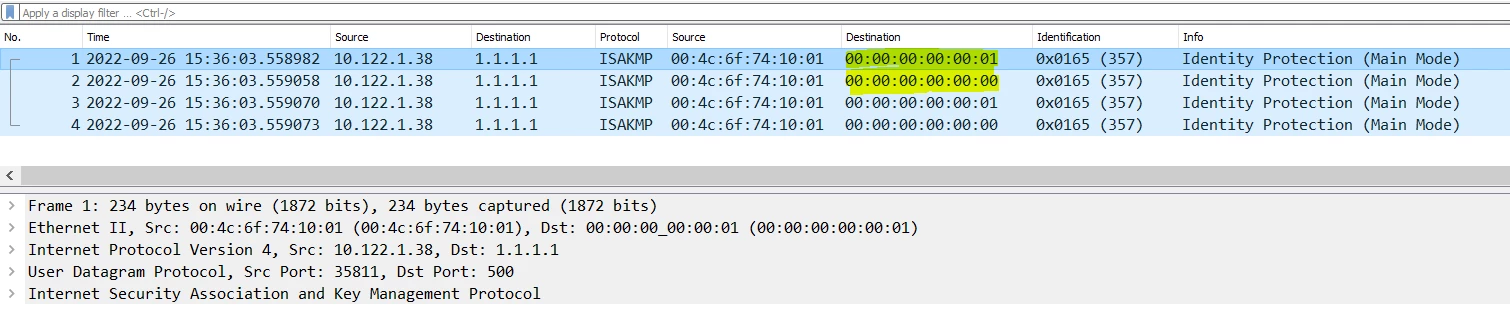
Put a color tagging on it by 'right-clicking' at the Destination Ethernet -> Colorize with Filter -> Color so it could be determined easily which packets are inbound and which are outbound.
Note. While this information can be more useful when reviewing a packet capture gathered from a transparent firewall, the same pattern of mac addressing applies to NAT mode firewall as long as 'any' interface was used in the filter when using the 'diagnose sniffer packet' command. |

