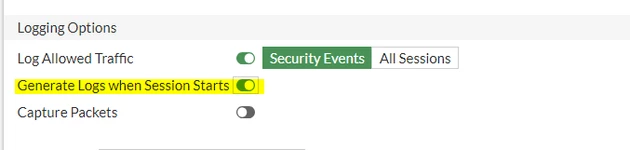
Solution | This can be enabled on the specific firewall policy: config firewall policy
edit <id>
set logtraffic-start enable
end
 Notes: It can be checked by the command:
diagnose sys session filter <filter>
diagnose sys session list
Refer to the following article to understand more information about the session table:
Troubleshooting Tip: FortiGate session table information
Normal behavior is that the logs are generated when the session closes.
For creating logs when the session starts, as well as the 'Generate logs when session starts' must be enabled.
This way, two logs will be generated, one at the start and one when the session ends. Security Rating under Security Setting -> Security Posture -> Audit Logs Setting recommends enabling this feature. This feature will affect CPU and Memory utilization depending on the traffic size, log size, etc., therefore, caution is recommended when enabling this feature. This feature is not recommended for small-grade devices as this will trigger conserve mode. This can be enabled when troubleshooting.
For Deny traffic:
The 'Generate log when session start' option is useful for Deny policies specifically when the 'ses-denied-traffic' option is enabled: Technical Tip: How to enable denied session to be added into the session table The user may encounter issues where this option is not visible in the GUI for Deny policies, but it can be configured through the CLI. In this case, the 'logtraffic-start' command will work and make sense.
|




