



Technical Tip: How to enable TCP sessions without SYN
Description
This article describes how TCP sessions without SYN can be configured when creating or editing a policy from the GUI.
Scope
FortiGate.
Solution
From CLI:
config system settings
    set tcp-session-without-syn enable
end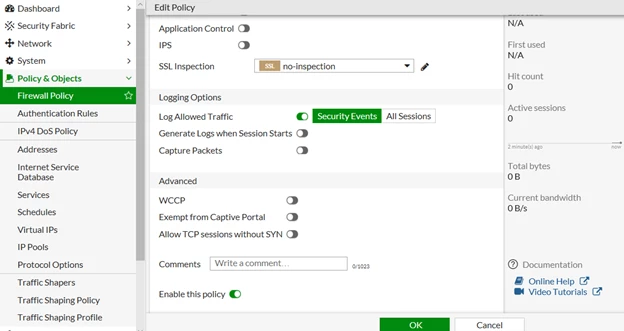
TCP sessions without SYN can now be configured when creating or editing a policy from the GUI.
If traffic is bidirectional with different policies, mirror a specific reverse policy and 'set tcp-session-without-syn' consistently for the reverse flow.
Keep the reverse rule as tight as possible on addresses/ports.
Note:
The 'tcp-session-without-syn' command allows the creation of a TCP session on the firewall without checking the SYN flag on the first packet.
Normally, a TCP session starts with a three-way handshake, beginning with a SYN (synchronize) packet. This ensures both sides know the connection and establishes initial sequence numbers for data transmission.
Enabling 'tcp-session-without-syn' is risky because it bypasses the normal SYN packet handshake in TCP connections. This makes it easier for attackers to hijack sessions, perform replay attacks, confuse connection states, and bypass security measures, thereby compromising network security.

