
Technical Tip: How to enable IKE debugging with various debug levels using a bitmask to isolate specific types of information for troubleshooting IKE negotiation failures
| Description | This article describes how to enable and capture debug information for troubleshooting IKE negotiation failures on a FortiGate device. IKE debugging can help identify configuration errors, negotiation failures, and issues related to NAT-T, DPD, and key exchanges during IPsec VPN setup. |
| Scope | FortiGate. |
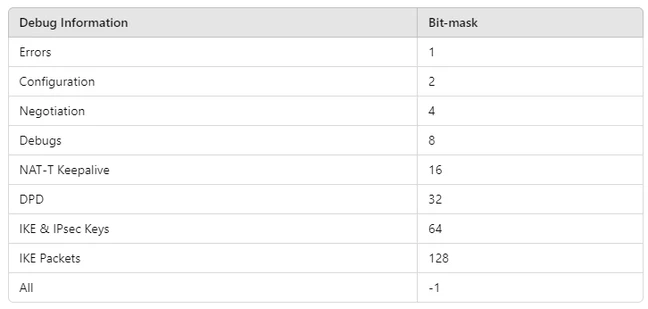
| Solution | Debug Levels and Information: FortiGate offers various debug levels using a bitmask to isolate specific types of information. The following are the available debug information levels:
diagnose debug application ike «debug-level»
IKE debug with appropriate filters:
diagnose debug disable diagnose debug reset
To stop debugging:
diagnose debug disable diagnose debug reset
Starting from v7.4.1, the command to filter logs related to a specific Remote Peer IP has been changed to:
diagnose vpn ike log filter rem-addr4 <ip.of.remote.peer> These steps will enable IKE debugging on the FortiGate to capture detailed information related to IKE negotiation failures, certificate authentication, NAT-T issues, and other related factors. The debug output can then be analyzed to identify and resolve VPN negotiation problems.
Note: Starting from FortiOS v7.6.3, it is possible to run IKE debugging directly from the GUI by navigating to VPN -> VPN Tunnels. 'Right-click' on the tunnel and select 'CLI diagnostics'. For more information, refer to Technical Tip: Collect IKE Debug Logs for IPsec VPN Directly from the GUI. |