
Technical Tip: How to distribute a Fortinet CA SSL certificate on a local domain on a Windows Server
| Description | The article explains how to distribute a Fortinet Root or Intermediate Certificate (CA) to ensure that devices on the network trust the certificate used by the FortiGate, especially in the case of SSL Inspection or SSL VPN. This is done using Group Policies (GPO) in an Active Directory environment. |
| Scope | FortiOS Windows Server. |
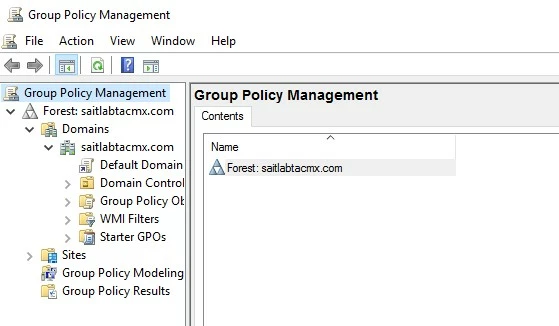
| Solution | Go to Group Policy Management on the Windows Server.
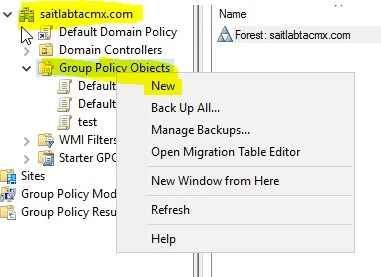
Create a new GPO if it does not exist:
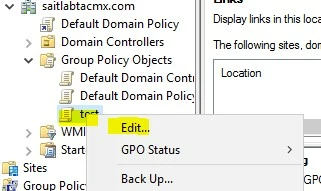
In this case, the GPO's name is 'test'. Right-click and select 'Edit'.
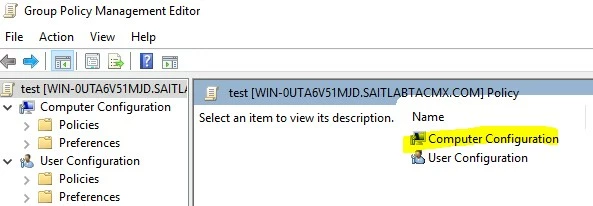
After, navigate to Computer Configuration -> Windows Settings -> Security Settings -> Public Key Policies -> Trusted Root Certification Authorities -> 'Right-Click' and choose the Import option -> Next, choose the path where the certificate file is, then finish the installation.
The client PCs can either be restarted or have the GPO manually synced by running the following command: gpupdate /force
Fortinet devices do not apply GPOs directly; this is an Active Directory functionality. It is mandatory that an Active Directory domain controller with GPMC, or a device running RSAT, can reach a domain controller. |