Technical Tip: How to decrypt TLS traffic generated by the browser (Windows operating system)
Description
This article describes how to decrypt TLS traffic generated by the browser (Windows operating system).
Scope
For Microsoft Windows products.
Solution
Note that decrypting TLS traffic may expose sensitive information.
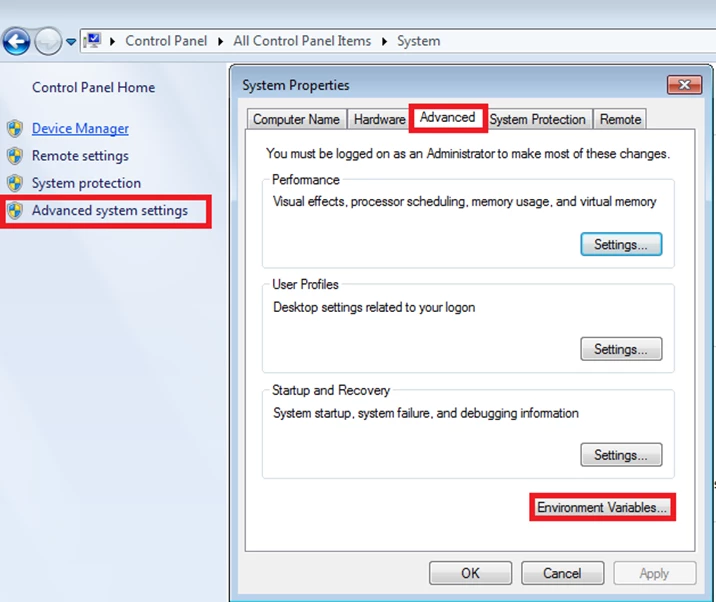
- Go to Control Panel -> Advanced system settings and select 'Environment Variables...'
-
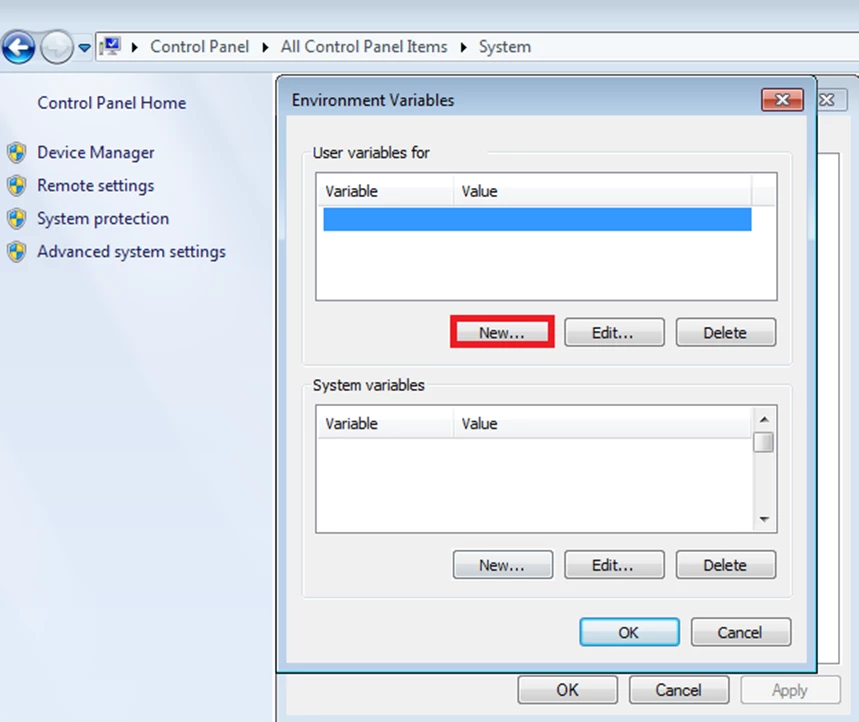
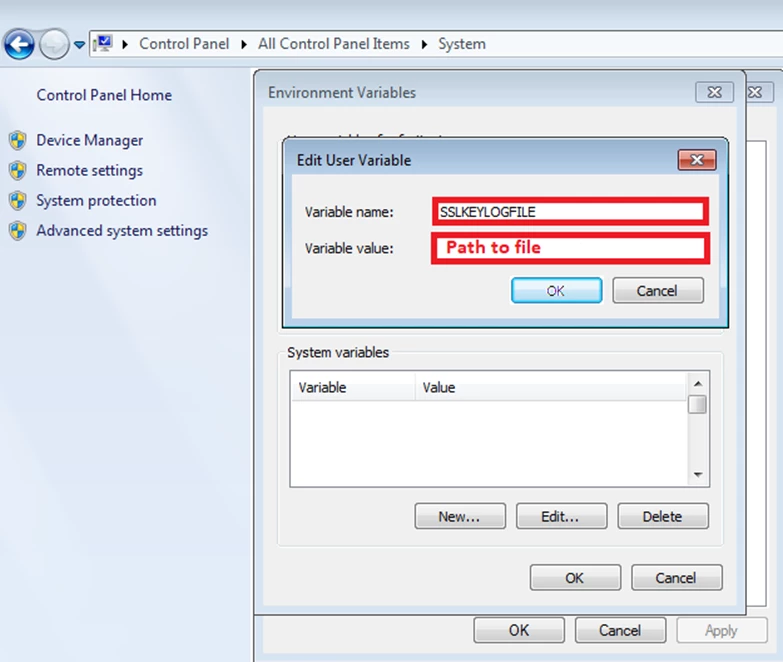
Select 'New' and add a new user variable 'SSLKEYLOGFILE' and point it at the location (full path) for the TLS session keys log file.
- Start packet capturing before starting the browser.
- Start the browser and navigate to the TLS website. TLS session keys are logged in the file specified in step 2.
- Stop packet capturing.
- Open Wireshark and go to Edit -> Preference -> Protocols -> SSL and select the '(Pre)-Master-Secret log filename' file specified in step 2.Note: In the new Wireshark releases, the protocol is not SSL anymore, but TLS.
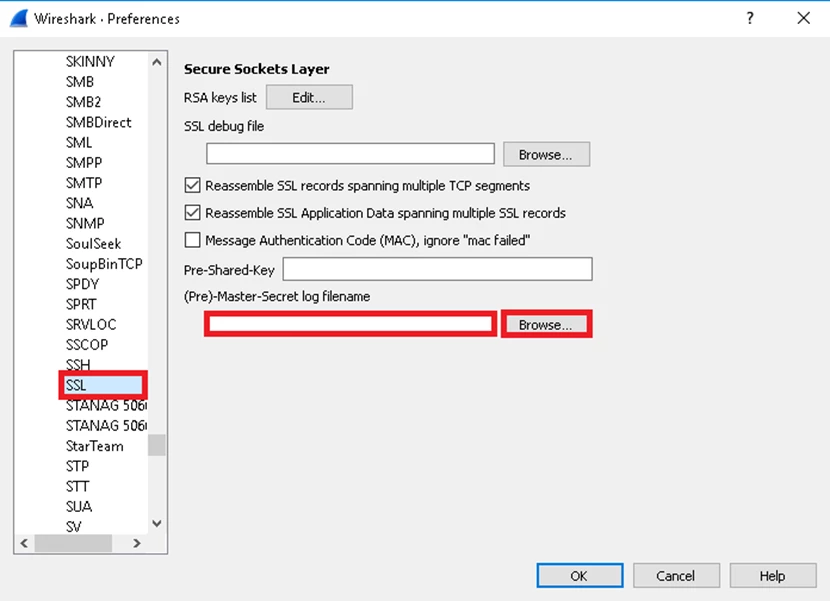
-
Open a '.pcap' file in Wireshark.
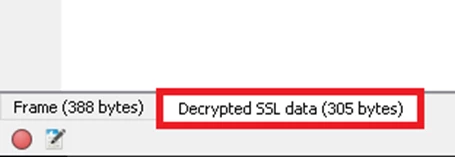
In case traffic is decrypted correctly, there will be a 'Decrypted SSL data' tab in the left bottom corner.